
 Do Son
Microsoft debuts Maia 200, a 3nm AI powerhouse with 140B transistors. Designed for GPT-5.2 and Copilot, it triples the performance of Amazon’s Trainium 3.

NVIDIA doubles down on AI infrastructure with a $2B stake in CoreWeave. Together, they aim to build a massive 5GW "AI Factory" ecosystem by 2030.

Google Calendar integrates Gemini AI to scan schedules and suggest the perfect meeting times. Say goodbye to back-and-forth emails with this new AI concierge.

OpenAI is pitching ChatGPT ads at a premium $60 CPM—triple Meta's rate. Is "high-intent" AI conversation worth the price despite limited tracking data?

Cloudflare reveals how an inadvertent policy change in Miami triggered a 25-minute BGP route leak, impacting global IPv6 traffic and exposing network vulnerabilities.

Apple releases iOS 26.2.1 to power the new AirTag 2. Discover how UWB 2 and a Gemini-backed Siri are set to redefine the Find My experience this spring.

CVSS 9.8 vm2 flaw (CVE-2026-22709) affects 3.7 million users, allowing total sandbox escape via async functions. Update to v3.10.2 immediately.

New React Server Components flaw CVE-2026-23864 (CVSS 7.5) exposes apps to DoS attacks. Previous patches were incomplete. Update to v19.0.4+ now.

Critical WD Discovery flaw CVE-2025-30248 (CVSS 8.9) allows DLL hijacking during installation. Update to v5.3 immediately to prevent system takeover.

Trend Micro uncovers PeckBirdy, a JScript C&C framework used by China-aligned APTs. It uses lightweight, fileless tactics to target Asian governments.

Microsoft patches zero-day CVE-2026-21509, actively exploited in the wild. The flaw bypasses OLE security in Office 2016/2019. Update to Build 16.0.10417+.

Your IR plan probably isn’t failing because it’s “bad.” It fails because, when something suspicious shows up,...

When you put your career on the line over AI-driven decisions, those decisions had better be defensible,...

CVE-2026-0994 (CVSS 8.2) in Google Protobuf Python allows DoS via nested "Any" messages. Recursion limit bypass causes crashes. Update now.

Attackers exploit GitHub forks ("Repo Squatting") to push HijackLoader malware via official-looking URLs. Technique remains active; verify all downloads.

Public PoC exploit released for critical Firefox WebRTC flaw CVE-2025-14321 (CVSS 9.8). AI-discovered bug allows remote code execution. Update now.

Malicious npm package "ansi-universal-ui" drops "G_Wagon" infostealer to steal cloud keys and wallets. Check for .gwagon_status and rotate creds now.
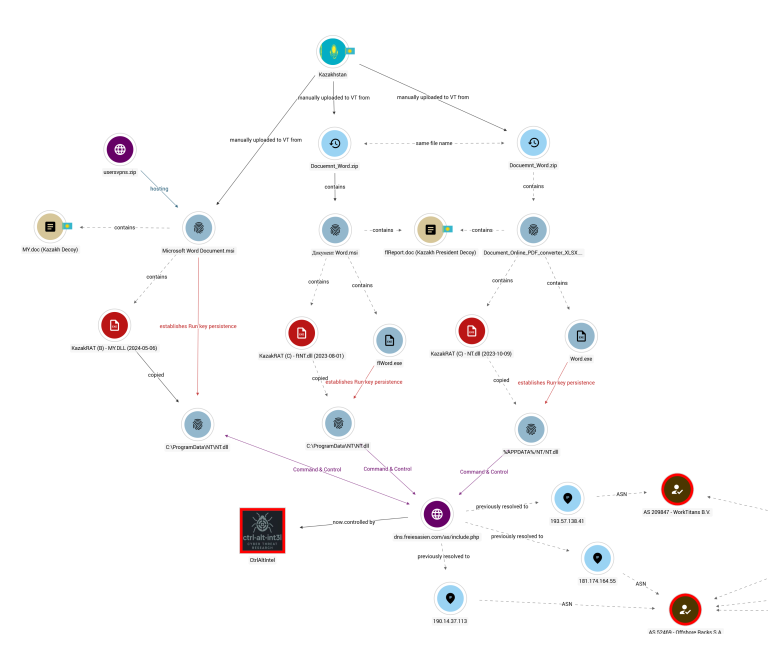
Researchers uncover "KazakRAT," a state-affiliated spyware targeting Kazakhstan & Afghanistan. A lapsed domain allowed experts to sinkhole the C2.

New ClearFake malware uses fake CAPTCHAs & "ClickFix" tactics to trick users into pasting malicious code. 150k victims infected via blockchain.
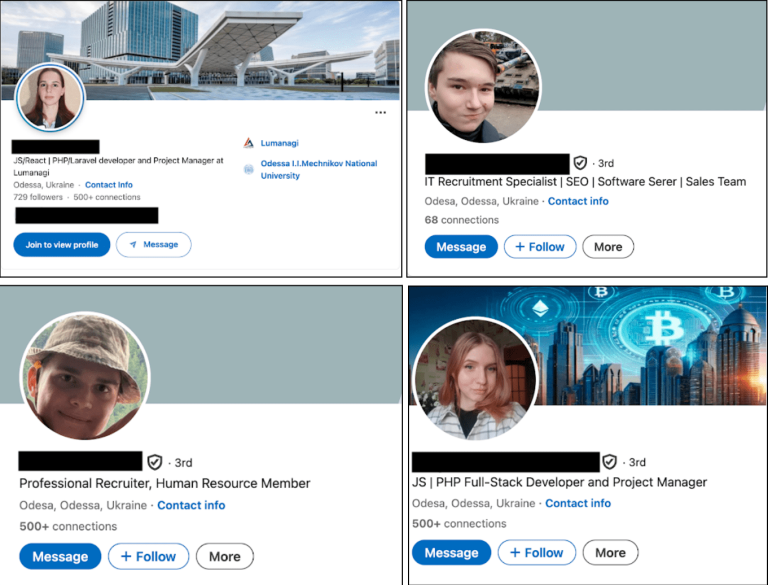
North Korean group PurpleBravo uses fake job offers to breach IT firms. The "Contagious Interview" campaign deploys malware via coding tests.

Official EmEditor installer hijacked to push malware. This supply chain attack steals credentials & evades detection. Check your logs for these domains.

1Password launches a new layer of security that warns you before pasting credentials into suspicious sites. Stop phishing scams before they steal your login.