
 Do Son
A Steam game, BlockBlasters, was compromised with malware in an update, which is stealing crypto and credentials from unsuspecting gamers.

A new BankBot campaign targets Android users in Indonesia and Vietnam. The malware uses spoofed app stores and a WebSocket-based download for stealth.

AhnLab has uncovered Kawa4096, a Go-based ransomware targeting Windows, Linux, and VMware ESXi. The malware uses advanced crypto and covert backup deletion.

A new report reveals attackers are abusing ScreenConnect to deliver AsyncRAT and custom malware payloads, a serious supply chain risk for enterprises and MSPs.

A new report reveals Subtle Snail, an Iran-nexus group, is using fake LinkedIn jobs to deliver a custom backdoor for espionage against European telecom and defense firms.

A new report from Black Lotus Labs reveals SystemBC, a malware-powered proxy network. The botnet compromises VPS systems and fuels global ransomware attacks.
According to Microsoft’s list of known issues updated on September 19, 2025, Windows 11 version 24H2 encounters...

Microsoft is bringing native video wallpaper support to Windows 11. The feature will let you set your favorite video file as a dynamic desktop background.

MediaTek's new Dimensity 9500 chip, built on a 3nm process, features an all-big-core design and dual NPUs to deliver massive gains in AI, gaming, and efficiency.

Apple's new C1X and N1 chips in the iPhone Air, along with a powerful A19 Pro, signal its push to control hardware and enable a new era of on-device AI.

A new technique, "EDR-Freeze," uses a built-in Windows feature to suspend antivirus and EDR processes, giving attackers a critical window to operate undetected.

LastPass warns of a new SEO poisoning campaign that uses fake GitHub repos to trick Mac users into downloading Atomic Stealer, a malware that steals data.
Meta has open-sourced its MobileLLM-R1 series, a new family of models designed for on-device reasoning in math, coding, and science.

Although Apple’s new iPhone 17 series and iPhone Air have only just launched this year, market attention...

A critical flaw (CVE-2025-41243) in Spring Cloud Gateway with a CVSS 10.0 score allows unauthenticated RCE via SpEL injection. A PoC has been released.

A new malware loader, CountLoader, is linked to Russian ransomware groups. The malware uses phishing lures impersonating the Ukrainian National Police to deliver payloads.
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
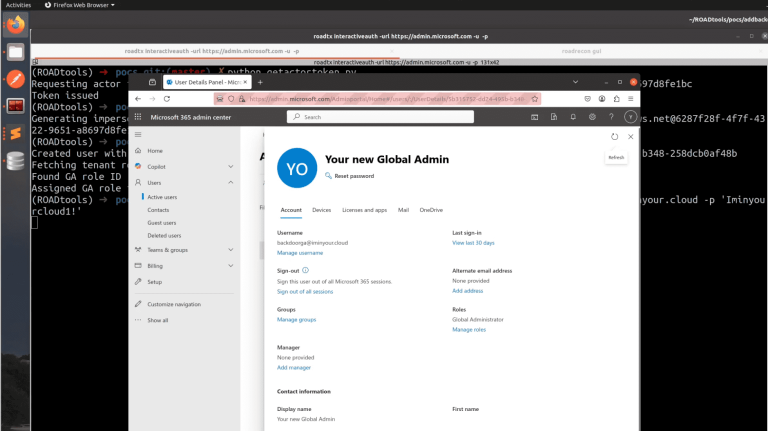
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
A critical flaw (CVE-2025-55241) in Microsoft Entra ID could have allowed a compromise of every tenant worldwide by bypassing security with "Actor tokens."
A decade-old browser flaw, "BiDi Swap," allows attackers to craft deceptive URLs for phishing. The bug, found by Varonis, exploits mixed-text direction.

A new report reveals that a Russian influence network, CopyCop, has created over 200 new AI-powered fake media sites to spread propaganda and deepfakes globally.

AhnLab has uncovered BlackLock, a Go-based ransomware targeting Windows, Linux, and VMware ESXi. The malware uses advanced crypto and covert backup deletion.

A new supply chain attack on PyPI is delivering SilentSync, a Python RAT. The malware steals credentials and files from developers' systems.

A new report reveals that an exposed Oracle Database was the entry point for a ransomware attack. Hackers used a scheduler function to gain access and deploy malware.