Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
CVE-2025-34158 (CVSS 10): Plex Media Server Users Warned to Patch Critical Vulnerability Now Plex vulnerability, CVE-2025-34158
  • Vulnerability Report

CVE-2025-34158 (CVSS 10): Plex Media Server Users Warned to Patch Critical Vulnerability Now

Do Son August 22, 2025 0

A critical vulnerability in Plex Media Server, with a CVSS score of 10.0, has been patched. Users are urged to update immediately to prevent exploitation.

CVE-2025-55746: Critical Directus Flaw Exposes Servers to Unauthenticated File Upload and RCE CVE-2025-55746
  • Vulnerability Report

CVE-2025-55746: Critical Directus Flaw Exposes Servers to Unauthenticated File Upload and RCE

Do Son August 22, 2025 0

A critical vulnerability in the Directus API (CVE-2025-55746) allows unauthenticated attackers to silently upload and modify files, leading to webshells and RCE.

CVE-2024-36401 Exploited in Stealthy Bandwidth-Monetization Campaign Passive monetization, GeoServer vulnerability
  • Cybercriminals
  • Vulnerability Report

CVE-2024-36401 Exploited in Stealthy Bandwidth-Monetization Campaign

Do Son August 22, 2025 0

A new report reveals a stealthy attack on GeoServer using a critical RCE flaw. Instead of ransomware, attackers are hijacking servers to earn passive income.

UAC-0057 Targets Ukraine and Poland with Weaponized Archives and Evolving Implants BlueNoroff macOS Attack GhostCall Campaign Carding Underground Bulletproof Hosting DPRK Contagious Interview, npm Flood Stonefly group -HiatusRAT Actors
  • Cybercriminals

UAC-0057 Targets Ukraine and Poland with Weaponized Archives and Evolving Implants

Do Son August 22, 2025 0

A new report from HarfangLab details two recent UAC-0057 (Ghostwriter) campaigns targeting Ukraine and Poland with malicious archives and multi-stage implants.

CVE-2025-9288: Critical Flaw in Popular JavaScript Library Threatens Global Web Security CVE-2025-9288 Cryptography Vulnerability
  • Vulnerability Report

CVE-2025-9288: Critical Flaw in Popular JavaScript Library Threatens Global Web Security

Do Son August 22, 2025 0

A critical flaw in the widely used sha.js library (CVE-2025-9288) can lead to hash collisions and private key extraction, threatening web applications.
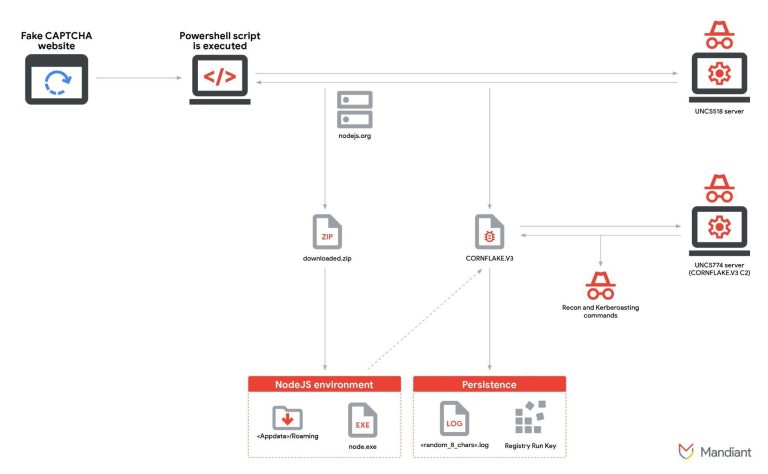
ClickFix and CORNFLAKE.V3: Mandiant Uncovers a New Wave of Access-as-a-Service Campaigns ClickFix, UNC5518
  • Cybercriminals

ClickFix and CORNFLAKE.V3: Mandiant Uncovers a New Wave of Access-as-a-Service Campaigns

Do Son August 22, 2025 0

UNC5518 is using "ClickFix," a new technique that weaponizes fake CAPTCHAs to trick users into launching malware and providing access to other criminal groups.

DDoS Onslaught: Hacktivists and Botnets Drive Massive Surge in Cyber Attacks Hacktivism
  • Cybercriminals

DDoS Onslaught: Hacktivists and Botnets Drive Massive Surge in Cyber Attacks

Do Son August 22, 2025 0
The latest analysis from NETSCOUT highlights a dramatic escalation in botnet-driven distributed denial-of-service (DDoS) attacks during July...
Read More Read more about DDoS Onslaught: Hacktivists and Botnets Drive Massive Surge in Cyber Attacks
Spear-Phishing Campaign Targets CFOs with Sophisticated Multi-Stage Intrusion Spear-phishing, MuddyWater
  • Cybercriminals

Spear-Phishing Campaign Targets CFOs with Sophisticated Multi-Stage Intrusion

Do Son August 22, 2025 0

A new report reveals a sophisticated spear-phishing campaign targeting finance executives. The attack uses social engineering and legitimate tools to evade detection.
RapperBot Botnet Dismantled: US Charges 22-Year-Old for Massive DDoS Attacks Winos 4.0 Malware Silver Fox APT RapperBot BVIEC cyberattack - CNC group DAMASCENED PEACOCK, malware analysis
  • Cybercriminals

RapperBot Botnet Dismantled: US Charges 22-Year-Old for Massive DDoS Attacks

Do Son August 21, 2025 0

A 22-year-old Oregon man has been charged with operating the RapperBot botnet, a network of 10,000s of devices that launched over 370,000 attacks.

AI’s New Attack Vector: How Real-Time Bots Are Straining Websites Mozi Botnet AI bots
  • Technology

AI’s New Attack Vector: How Real-Time Bots Are Straining Websites

Do Son August 21, 2025 0

A new report shows that AI bots, especially real-time inference queries from tools like ChatGPT, are causing server-overloading traffic that mimics DDoS attacks.

AMD’s FSR 4 Leaked: The Accidental Open Source Release AMD AM5 platform support AMD Embedded Processors Vulnerabilities
  • Data Leak

AMD’s FSR 4 Leaked: The Accidental Open Source Release

Do Son August 21, 2025 0

AMD accidentally uploaded the FSR 4 source code to GitHub before pulling it, sparking speculation about unofficial support for older graphics cards.

Free YouTube Downloads: The Catch and What You Need to Know YouTube End Screens, User Experience YouTube ad blocker YouTube Age Detection, AI Content Restrictions Youtube page load YouTube AI Overviews
  • Technology

Free YouTube Downloads: The Catch and What You Need to Know

Do Son August 21, 2025 0

ouTube is now letting free users download videos. But what's the catch? We break down the new limits on resolution and content for free downloads.

Privacy Fail: Grok Chatbot Exposes 370,000 Private Conversations Grok privacy
  • Data Leak

Privacy Fail: Grok Chatbot Exposes 370,000 Private Conversations

Do Son August 21, 2025 0

A design flaw in xAI's Grok chatbot has led to over 370,000 private conversations being indexed by search engines and exposed to the public.

Windows Update Is Reportedly Breaking SSDs, And Microsoft Is Finally Responding C Windows SecureBoot folder KB5089549 Windows 11 BSOD Microsoft Windows, Rust programming WINS Service Deprecation Windows Server DNS Migration Windows Driver Standard OEM Kernel Privileges Windows Agentic OS Task Manager Bug, Windows 11 Performance Windows 11, Microsoft, WinRE, Update Bug, Tech Support Windows 11 OOBE, Microsoft Account Mandatory Windows 11, SSD failures Windows 11 Recovery, Black Screen of Death Windows 11 Update Issue, KB5062324 Windows 11, Indicator Bar
  • Windows

Windows Update Is Reportedly Breaking SSDs, And Microsoft Is Finally Responding

Do Son August 21, 2025 0

Microsoft and Phison are investigating reports that recent Windows 11 updates are causing some SSDs to lock up, disappear, and even corrupt data.

Beyond Google Assistant: Gemini for Home Brings a New AI Experience—and Subscriptions Gemini Smart Home Smart home, Google Nest
  • Technology

Beyond Google Assistant: Gemini for Home Brings a New AI Experience—and Subscriptions

Do Son August 21, 2025 0

Google's new Gemini for Home is set to replace Google Assistant, bringing multimodal AI and a new subscription model to smart displays and speakers.

Warlock Ransomware: How a New Group Is Weaponizing Unpatched SharePoint Servers Warlock Ransomware
  • Cybercriminals

Warlock Ransomware: How a New Group Is Weaponizing Unpatched SharePoint Servers

Do Son August 21, 2025 0

A new report from Trend Micro details how the Warlock ransomware group is exploiting a vulnerability in unpatched Microsoft SharePoint servers to attack organizations.
AI’s Dark Side: How a New Website Builder Is Fueling a Surge in Cybercrime AI cybercrime, phishing
  • Cybercriminals

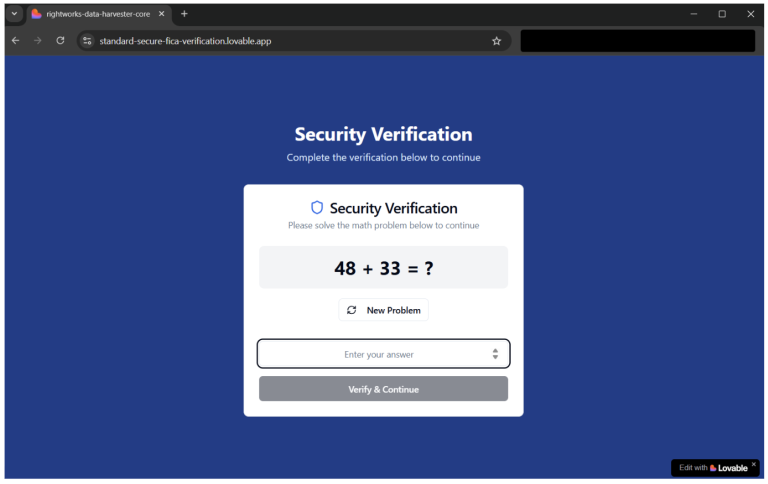
AI’s Dark Side: How a New Website Builder Is Fueling a Surge in Cybercrime

Do Son August 21, 2025 0

A new report reveals how criminals are using the AI website builder Lovable to create tens of thousands of convincing phishing, malware, and fraud websites.
A Decade of Espionage: How a Russian APT Exploited Cisco Devices (CVE-2018-0171) for Years Static Tundra CVE-2018-0171
  • Cyber Security
  • Vulnerability Report

A Decade of Espionage: How a Russian APT Exploited Cisco Devices (CVE-2018-0171) for Years

Do Son August 21, 2025 0

A new report from Cisco Talos exposes Static Tundra, a Russian state-sponsored group that has exploited unpatched Cisco devices for over a decade.

IBM X-Force Exposes the Stealthy QuirkyLoader Malware Malware loader, QuirkyLoader
  • Malware

IBM X-Force Exposes the Stealthy QuirkyLoader Malware

Do Son August 21, 2025 0

IBM X-Force has exposed QuirkyLoader, a new malware loader that uses DLL side-loading and .NET AOT compilation to deliver Agent Tesla and other threats.
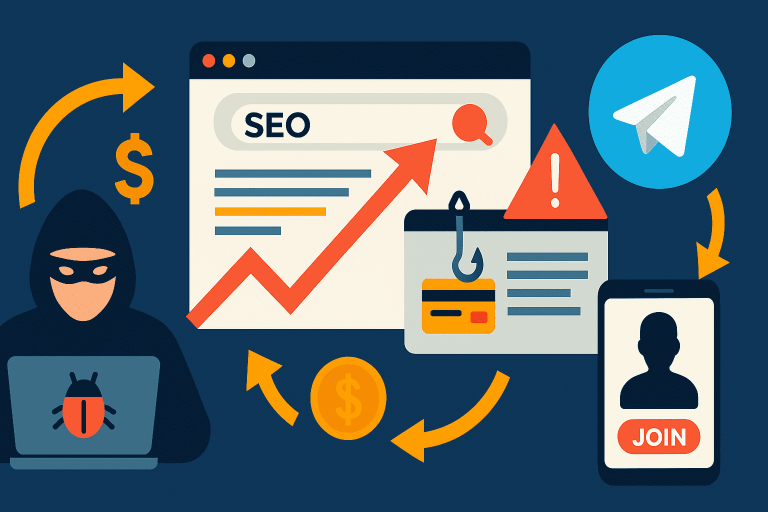
Inside the “Traffer” Economy: How a Thriving Cybercrime Ecosystem Professionalized Data Theft SEO
  • Cybercriminals

Inside the “Traffer” Economy: How a Thriving Cybercrime Ecosystem Professionalized Data Theft

Do Son August 21, 2025 0

A new report uncovers the "Traffer" economy, a sophisticated cybercriminal ecosystem that uses business-like structures and SEO abuse to steal data at scale.

Kudelski Security Exposes Critical CodeRabbit Vulnerability: RCE, Secret Leaks, and Access to 1M Repositories AI tool vulnerability, supply chain attack
  • Vulnerability Report

Kudelski Security Exposes Critical CodeRabbit Vulnerability: RCE, Secret Leaks, and Access to 1M Repositories

Do Son August 21, 2025 0

A critical flaw in the AI tool CodeRabbit allowed a researcher to gain RCE and write access to over a million repositories via a malicious pull request.
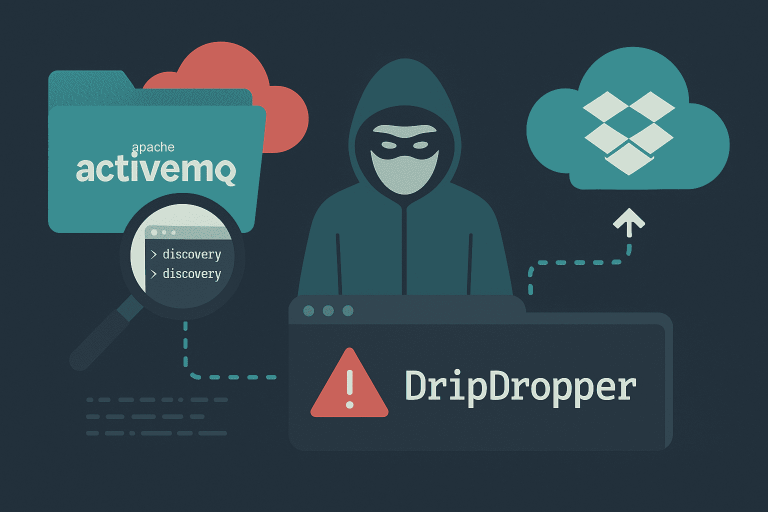
How Attackers Exploit and Then Patch a Vulnerability to Hide in Linux Systems Apache ActiveMQ, self-patching malware
  • Malware

How Attackers Exploit and Then Patch a Vulnerability to Hide in Linux Systems

Do Son August 21, 2025 0

A Red Canary report reveals attackers are exploiting an Apache ActiveMQ flaw to breach Linux systems, then patching the vulnerability to hide their presence.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.