Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
How Attackers Exploit and Then Patch a Vulnerability to Hide in Linux Systems Apache ActiveMQ, self-patching malware
  • Malware

How Attackers Exploit and Then Patch a Vulnerability to Hide in Linux Systems

Do Son August 21, 2025 0

A Red Canary report reveals attackers are exploiting an Apache ActiveMQ flaw to breach Linux systems, then patching the vulnerability to hide their presence.

Mandiant Uncovers USB-Borne Malware Campaign Deploying Cryptocurrency Miners xmring
  • Malware

Mandiant Uncovers USB-Borne Malware Campaign Deploying Cryptocurrency Miners

Do Son August 21, 2025 0

A new Mandiant report reveals a multi-stage USB malware campaign that uses DLL side-loading and stealthy loaders to deploy backdoors and coinminers.

CVE-2025-54988: Critical XXE Vulnerability in Apache Tika PDF Parser Exposes Sensitive Data Apache Tika XXE, Malicious PDF Exploit Apache Tika, XXE vulnerability CVE-2025-54988
  • Vulnerability Report

CVE-2025-54988: Critical XXE Vulnerability in Apache Tika PDF Parser Exposes Sensitive Data

Do Son August 21, 2025 0

A critical XXE flaw in Apache Tika's PDF parser could allow attackers to access sensitive data and pivot into internal networks via crafted PDF files.
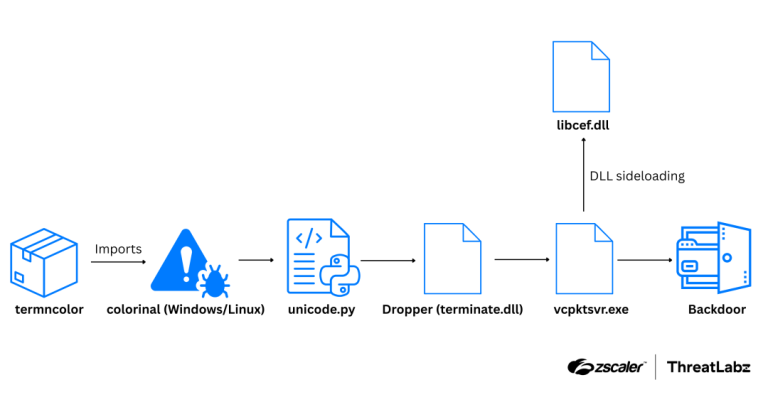
A Trojan in Disguise: New Python Package on PyPI Hides a Multi-Stage Malware Operation Supply chain attack
  • Malware

A Trojan in Disguise: New Python Package on PyPI Hides a Multi-Stage Malware Operation

Do Son August 21, 2025 0

A new report reveals a malicious Python package on PyPI that uses a stealthy dependency and DLL sideloading to deliver a multi-stage malware.

Beyond the Inbox: How a Cyber-Espionage Group Is Exploiting Two WinRAR Vulnerabilities WinRAR Zero-day
  • Cybercriminals
  • Vulnerability Report

Beyond the Inbox: How a Cyber-Espionage Group Is Exploiting Two WinRAR Vulnerabilities

Do Son August 21, 2025 0
BI.ZONE Threat Intelligence uncovered a series of targeted cyber-espionage campaigns conducted by the Paper Werewolf (GOFFEE) cluster,...
Read More Read more about Beyond the Inbox: How a Cyber-Espionage Group Is Exploiting Two WinRAR Vulnerabilities
Beyond Cellular: Qualcomm’s New Wearable Chips Bring Satellite Communication to Your Wrist Snapdragon W5 Gen 2
  • Technology

Beyond Cellular: Qualcomm’s New Wearable Chips Bring Satellite Communication to Your Wrist

Do Son August 20, 2025 0

Qualcomm’s new Snapdragon W5+ Gen 2 and W5 Gen 2 wearable chips are the first to support two-way satellite messaging, providing a new layer of safety.

Google Unveils the Pixel 10 Series: New Tensor G5, AI Features, and a Magnetic Interface Google Pixel 10, Tensor G5Pixel AI Strategy Auto Best Take
  • Android

Google Unveils the Pixel 10 Series: New Tensor G5, AI Features, and a Magnetic Interface

Do Son August 20, 2025 0

Google has launched the Pixel 10 series, featuring the new Tensor G5 chip, advanced AI features, the Pixelsnap magnetic interface, and a new foldable.

Critical Docker Desktop Vulnerability Exposes Host Systems to Container Abuse Docker Malware Campaign Docker Vulnerability CVE-2025-9074
  • Vulnerability

Critical Docker Desktop Vulnerability Exposes Host Systems to Container Abuse

Do Son August 20, 2025 0

A critical vulnerability (CVSS 9.3) in Docker Desktop could allow malicious containers to gain full control of the host system. Update now to version 4.44.3.

Apple Issues Urgent Patch for Zero-Day Vulnerability CVE-2025-43300 Exploited in the Wild Apple Bounty $5M, Zero-Click Exploit Zero-day, Apple security CVE-2025-43300
  • Vulnerability Report

Apple Issues Urgent Patch for Zero-Day Vulnerability CVE-2025-43300 Exploited in the Wild

Do Son August 20, 2025 0

Apple has released an urgent security update to patch a zero-day vulnerability (CVE-2025-43300) in its Image I/O framework that is being actively exploited in targeted attacks.

Link11 Highlights Growing Cybersecurity Risks and Introduces Integrated WAAP Platform link11_PDP_WAAP_Accordion_Web-Application-Firewall_1755592757I4cYWk4aE2
  • Press Release

Link11 Highlights Growing Cybersecurity Risks and Introduces Integrated WAAP Platform

cybernewswire August 20, 2025
Frankfurt am Main, Germany, 20th August 2025, CyberNewsWire
Read More Read more about Link11 Highlights Growing Cybersecurity Risks and Introduces Integrated WAAP Platform
DuckDNS Is Down: What Happened to the Free DDNS Service? DuckDNS Down
  • Technology

DuckDNS Is Down: What Happened to the Free DDNS Service?

Do Son August 20, 2025 0

The free DDNS service DuckDNS has gone offline, leaving users unable to access their home servers. Users are urged to migrate to an alternative service.

Google’s Big Concession: A New Policy Could Upend the Play Store in the EU Google Self-Preferencing Fine Idealo Antitrust Damages Anthropic, Google TPUs Google DMA Compliance, Search Self-Preferencing Google Play Store Ruling, Epic Games Victory Google fine, ad tech Google lawsuit, privacy violation Gmail security, false alarm Google Play EU regulation Google Security, Phone Number Leak Google 2025 - Google China’s Anti-Monopoly Law Google monopoly, ad tech Pixel 7a battery, battery swelling
  • Technology

Google’s Big Concession: A New Policy Could Upend the Play Store in the EU

Do Son August 20, 2025 0

Google is overhauling its Play Store in the EU to comply with the Digital Markets Act, offering developers new options to steer users to external payment systems.

CVE-2025-54336 (CVSS 9.8): Critical Flaw in Plesk Obsidian Exposes Servers to Full Compromise CVE-2025-54336 Plesk Vulnerability
  • Vulnerability Report

CVE-2025-54336 (CVSS 9.8): Critical Flaw in Plesk Obsidian Exposes Servers to Full Compromise

Do Son August 20, 2025 0

A critical vulnerability (CVE-2025-54336) in Plesk Obsidian could allow attackers to bypass the admin password and take complete control of affected servers.

Firefox Switches to CRLite, Ditching OCSP for Better Speed and Privacy Firefox 32-bit Linux Firefox, CRLite Firefox 141, AI Tab Groups Firefox Focus Android
  • Technology

Firefox Switches to CRLite, Ditching OCSP for Better Speed and Privacy

Do Son August 20, 2025 0

Firefox is switching to CRLite for certificate revocation, a major change that improves security and privacy by eliminating the need for real-time OCSP queries.

Apple’s “Made in India” Revolution: iPhone 17 Production Ramps Up Ahead of Launch Apple HomePad delay Tesla CarPlay integration 2026 Apple CarPlay AI integration 2026 Apple 2026 product roadmap rumors, foldable iPhone release date Apple Vision Pro sales slump, Vision Pro production cut Russia FaceTime Ban Network Blockade Apple Apple 2026 Roadmap, iPhone Foldable, Apple Intelligence Apple Maps ads, iOS monetization Apple, Digital Markets Act FCC Leak, iPhone 16e Schematics iPhone Fold Apple Made in India Apple US Investment, Indian Tariffs Apple Leadership, Tim Cook Tenure Siri Redesign, Apple AI Apple App Store Apple EU, Digital Markets Act CVE-2022-32898 Third-Party iOS Apps Apple Antitrust, DOJ Lawsuit
  • Technology

Apple’s “Made in India” Revolution: iPhone 17 Production Ramps Up Ahead of Launch

Do Son August 20, 2025 0

Apple is reportedly manufacturing all four iPhone 17 models in India for the first time, marking a major shift in its strategy to reduce reliance on China.

The Backdoor Is No More: UK Government Drops Demand for Access to iCloud Apple Background Security CVE-2026-20643 Apple Background Security Improvement Apple Backdoor Apple Lawsuit, Data Exfiltration CVE-2024-44131 - CVE-2025-24118 PoC
  • Data Leak

The Backdoor Is No More: UK Government Drops Demand for Access to iCloud

Do Son August 20, 2025 0

Following U.S. intervention, the UK government has reportedly dropped its demand for Apple to install a backdoor in iCloud, which could restore Advanced Data Protection.

Windows Update is Breaking SSDs and Recovery, and Microsoft is Scrambling to Fix It Windows SSD issues
  • Windows

Windows Update is Breaking SSDs and Recovery, and Microsoft is Scrambling to Fix It

Do Son August 20, 2025 0

A new Windows update is causing major issues, including SSD lock-ups on some systems and broken reset/recovery options on all supported versions.

Qualcomm Unveils Snapdragon 7s Gen 4: A New Chip That Pushes Entry-Level Phones Closer to Flagships Snapdragon 7s Gen 4
  • Technology

Qualcomm Unveils Snapdragon 7s Gen 4: A New Chip That Pushes Entry-Level Phones Closer to Flagships

Do Son August 20, 2025 0

Qualcomm unveils the Snapdragon 7s Gen 4, a new mobile platform that brings significant CPU and GPU gains, plus flagship camera features to mid-range devices.

Hacker Tied to Yemen Cyber Army Sentenced for Stealing Data of 4 Million People Cybercrime, Hacker
  • Cybercriminals

Hacker Tied to Yemen Cyber Army Sentenced for Stealing Data of 4 Million People

Do Son August 20, 2025 0

A 26-year-old UK hacker, tied to the Yemen Cyber Army, has been sentenced to 20 months in prison for breaching thousands of websites and stealing data.

CERT/CC Warns of Critical Flaws in Workhorse Municipal Accounting Software Municipal software, Vulnerability
  • Vulnerability Report

CERT/CC Warns of Critical Flaws in Workhorse Municipal Accounting Software

Do Son August 20, 2025 0

Critical design flaws in Workhorse Software's municipal accounting platform could allow unauthenticated users to download full database backups with sensitive PII and financial records.

Google Chrome Issues High-Severity Fix for V8 Engine Vulnerability (CVE-2025-9132) Chrome 148 lazy loading Chrome for Linux ARM64 Chrome 145 Update Chrome Security Fixes Chrome Security Update CVE-2026-1220 Chrome 144 Security Update CVE-2026-0899 Chrome Memory Safety, WebGPU UAF Chrome V8 Type Confusion, Google Updater Flaw Chrome V8 Flaw, CVE-2025-13042 Chrome V8, Type Confusion, Chrome 142 Update Chrome V8 Flaw, CVE-2025-12036 Chrome 141, WebGPU Overflow Google Chrome preloading Chrome, V8 vulnerability CVE-2025-9132 Chrome Security Update, Use-After-Free Chrome V8, Type Confusion Chrome Telemetry, Windows 10 EOL Microsoft Family Safety, Chrome Blocking Chrome Security Update, High-Severity Google Chrome, Antitrust CVE-2024-10487 and CVE-2024-10488 Google Chrome Root Program Chrome Update, CVE-2025-3619 Chrome Acquisition, Perplexity.ai
  • Vulnerability Report

Google Chrome Issues High-Severity Fix for V8 Engine Vulnerability (CVE-2025-9132)

Do Son August 20, 2025 0

Google has released an urgent update for Chrome, patching a high-severity, out-of-bounds write vulnerability in the V8 JavaScript engine. Update your browser now.

Spies in Your Skype: GodRAT Malware Uses Steganography to Target Financial Firms Cyber-espionage, GodRAT
  • Malware

Spies in Your Skype: GodRAT Malware Uses Steganography to Target Financial Firms

Do Son August 20, 2025 0

A new report reveals GodRAT, a sophisticated backdoor based on the Gh0st RAT family, is using steganography to launch attacks via Skype messenger.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.