
 Do Son
The Amazon Threat Intelligence team has uncovered a highly sophisticated threat campaign exploiting multiple zero-day vulnerabilities in...
Latest news

A new malware distribution trend is emerging across the macOS threat landscape, according to fresh research from...

Zoho Corporation has released an urgent security advisory addressing a critical severity SQL injection vulnerability affecting Analytics...

Microsoft has patched a newly disclosed local privilege escalation (LPE) vulnerability affecting the Host Process for Windows...

 cybernewswire
New York, New York, 13th November 2025, CyberNewsWire

Transferring data between cloud-storage services has long been a persistent frustration. Some conscientious platforms, either due to...

Apple has announced a significant update to Apple Wallet, formally enabling users to digitize their United States...

Microsoft had previously announced that Windows 11 would introduce new APIs enabling password-manager applications to integrate directly...

Following the enormous success of the Steam Deck in the handheld market, Valve has now formally unveiled...

The well-known MAS activation team reports that Microsoft has modified the KMS activation mechanism in Windows 11...

The vulnerability, tracked as CVE-2024-4577, could potentially allow unauthenticated attackers to take full control of affected PHP servers

Sophos researchers have uncovered a sophisticated and long-running cyberespionage campaign, dubbed Operation Crimson Palace

The attack begins with hackers compromising websites and inserting malicious code, often through the legitimate WordPress plugin "Hustle."

CVE-2023-33246 in RocketMQ versions 5.1.0 and below, allowing attackers to remotely execute code and download the notorious Muhstik malware
The vulnerabilities, tracked as CVE-2024-20404 and CVE-2024-20405, could be exploited by unauthenticated, remote attackers to carry out SSRF and stored XSS attacks

Researchers have identified a concerning resurgence of attacks targeting known vulnerabilities in the ThinkPHP web application framework

Trustwave SpiderLabs has uncovered a dangerous cyberattack campaign targeting users of the popular network scanning tool, Advanced IP Scanner

ReversingLabs researchers uncovered a malicious open-source package on the Python Package Index (PyPI) called xFileSyncerx

RansomHub attackers gained initial access by exploiting the Zerologon vulnerability (CVE-2020-1472), which grants domain administrator privileges

Cybersecurity researchers have uncovered a novel cryptojacking campaign dubbed "Commando Cat," actively targeting Docker Remote API servers

The impact of CVE-2024-5171 and CVE-2024-5197 is significant due to the widespread use of libaom and libvpx in various applications

A CoinMiner, a type of malware that hijacks systems to mine cryptocurrency, unwittingly left a backdoor open

A massive DNS probing operation, dubbed "Secshow," has been underway since June 2023, targeting open DNS resolvers worldwide

ASEC has recently identified a phishing campaign leveraging HTML files distributed via email to execute malicious commands on targeted systems

This vulnerability, designated as CVE-2024-4295, carries a severity rating of 9.8 (CVSS), making it a prime target for exploitation

Kali Linux, the renowned open-source, Debian-based Linux distribution, has officially released its latest version, Kali Linux 2024.2

Trend Micro's threat-hunting team has uncovered a new Linux variant of the TargetCompany ransomware, marking a significant escalation

Parrot OS 6.1 brings a slew of improvements and upgrades designed to bolster system performance, stability, and security
In a recent wave of cyberattacks, TikTok has confirmed a zero-day vulnerability within its direct messaging system has been exploited
Security researcher published the technical details and a proof-of-concept (PoC) code for a vulnerability, identified as CVE-2023-3390
CVE-2024-36522 discovered in earlier versions of Apache Wicket, stemmed from a potential XSLT injection attack, enabling malicious actors to RCE
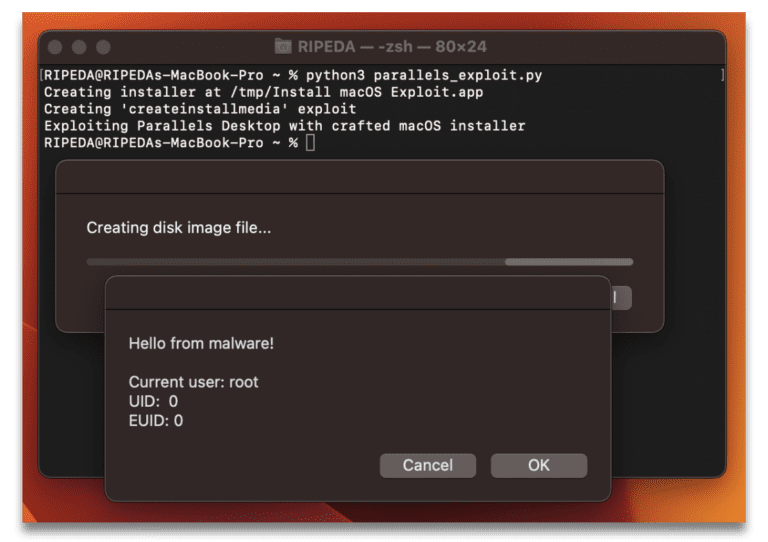
The technical details and a proof-of-concept (PoC) exploit code for a vulnerability (CVE-2024-34331) in Parallels Desktop for Mac