
 Do Son
Apple has announced the launch of a new App Store Mini Apps Partner Program, offering reduced fees...
Latest news
“Is it working?” It can be easy to drop an AI SOC agent into your environment and...

Cybersecurity firms are sounding the alarm over a critical vulnerability in Fortinet FortiWeb, the company’s Web Application...
ASUS has released an urgent security advisory addressing a critical authentication bypass vulnerability affecting several models in...

Qualcomm has announced the launch of its first processor series designed specifically for industrial-grade computers (Industrial PCs,...

OpenAI has announced the release of GPT-5.1, a major revision within the GPT-5 generation, designed not only...

Apple has recently released the macOS Tahoe 26.2 Developer Beta, within which a new feature known as...

Microsoft is gradually weaving a wide range of artificial intelligence capabilities into Windows 11, with the most...

The Socket Threat Research Team has uncovered a highly sophisticated malicious Chrome extension posing as an Ethereum...

NVIDIA has released an important security update for its NeMo Framework, addressing two high-severity vulnerabilities that expose...

Schneider Electric has released a critical security patch to address multiple vulnerabilities in its SAGE Remote Terminal Unit (RTU) devices

Veeam, a prominent backup and disaster recovery solutions provider, has recently addressed a critical vulnerability (CVE-2024-29855)

This vulnerability is currently being actively exploited by malicious actors in a widespread ransomware campaign known as "TellYouThePass."

A high-severity vulnerability (CVE-2024-5585) has been identified in multiple versions of PHP, the widely used server-side scripting language

Researchers have demonstrated that teams of AI agents, powered by large language models, can successfully exploit zero-day vulnerabilities

IBM X-Force Red, a team of cybersecurity researchers, has uncovered critical vulnerabilities in Precor smart treadmills

Tracked as UNC5537, this financially motivated threat actor has systematically compromised hundreds of Snowflake customer accounts

CVE-2024-5452 enables attackers to remotely manipulate the entire application state, potentially leading to complete system takeover

Mustang Panda has been conducting a series of targeted attacks since April 2024, focusing on entities with interests in tax compliance and education

A newly released proof-of-concept (PoC) exploit has heightened concerns about a critical vulnerability (CVE-2024-29849)

A security researcher has published a proof-of-concept (PoC) exploit code targeting a recent important severity vulnerability (CVE-2024-30043)

A surge in cyber activity associated with the Sticky Werewolf group, a threat actor with suspected geopolitical or hacktivist ties
A series of critical vulnerabilities in the popular Netgear WNR614 N300 router, exposing users to significant security risks

A new variant of an ongoing cryptojacking campaign targeting misconfigured Kubernetes clusters has been uncovered
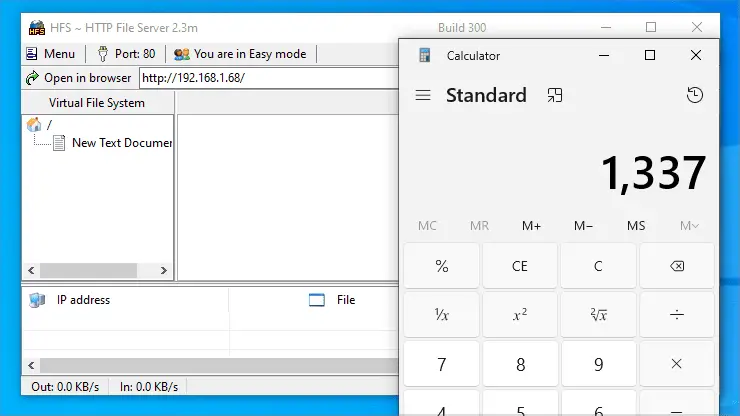
A critical vulnerability, identified as CVE-2024-23692, has been discovered in Rejetto HTTP File Server (HFS) versions 2.x

FortiGuard Labs has recently identified a new phishing campaign deploying a variant of the notorious Agent Tesla malware

Bitdefender, a leading cybersecurity provider, has addressed a vulnerability (CVE-2024-4177) in its GravityZone Console On-Premise product

eSentire's Threat Response Unit (TRU) has unveiled a persistent and sophisticated cyber campaign employing the notorious more_eggs malware

A critical vulnerability (CVE-2024-5480) has been discovered in PyTorch's distributed RPC (Remote Procedure Call) framework

TRU has unveiled a sophisticated attack campaign utilizing counterfeit KMSPico activators to deliver the notorious Vidar Stealer malware

chip design giant Arm has disclosed a critical zero-day vulnerability (CVE-2024-4610) actively being exploited in the wild

watchTowr published the technical details and a PoC exploit code for a recently disclosed critical vulnerability (CVE-2024-4577) in PHP