 Do Son
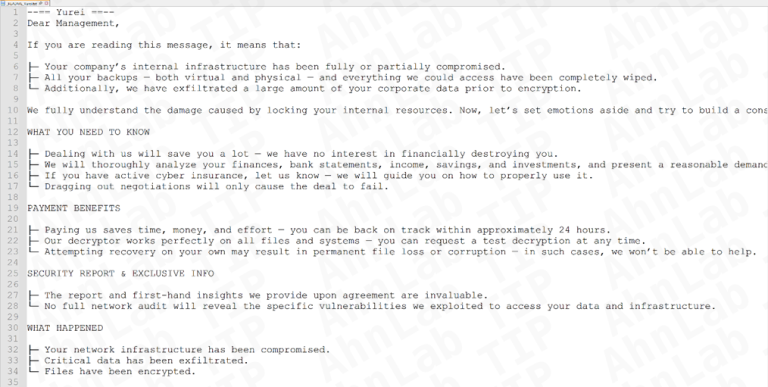
Security researchers at AhnLab have identified Yurei, a newly emerging ransomware group first observed in early September...
Latest news

OpenAI CEO Sam Altman has confirmed via his personal X account that ChatGPT has finally addressed one...


Google recently announced an expansion of its investment in Texas, a state where the company has maintained...

Microsoft has announced that it is officially opening its internal Xbox Game Publishing Guide to the public—a...

To comply with the EU Digital Markets Act (DMA), Meta has announced that WhatsApp will soon become...

Amazon has announced that its satellite communications initiative, formerly known as Project Kuiper, will be officially rebranded...

Sender Policy Framework (SPF) is a vital component of modern email authentication protocols, designed to combat email...

The Symfony project has released security updates to address a newly disclosed vulnerability affecting its widely used...

A newly disclosed high-severity vulnerability in the Cisco Catalyst Center Virtual Appliance could allow attackers with low-level...

A security researcher has published PoC code targeting a recently patched high-severity vulnerability in Microsoft Windows (CVE-2024-26229)

Hundreds of fraudulent websites have been identified, falsely claiming to sell tickets to the Paris 2024 Summer Olympic Games

A high-severity vulnerability, identified as CVE-2022-23829 (CVSS 8.2), has been discovered in various AMD processors

A new phishing technique exploiting Progressive Web Apps (PWAs) has been brought to light by cybersecurity researcher Mr.d0x

ASEC has disclosed a new cyberespionage campaign attributed to the North Korean state-sponsored group Kimsuky

cybersecurity researchers have unveiled a sophisticated new backdoor, dubbed "BadSpace," that poses a significant threat to internet users

A recent analysis by security researcher Jacob Malimban at Cofense has revealed a resurgence in activity from the STR RAT malware

TAG and Mandiant's frontline intelligence team have detailed the unique and intricate cyber threat landscape facing Brazil

 Dan Agbo
Software Staff Engineer at international fintech company One Inc. explains how attackers managed to steal data from...

Google has released a critical security update for Pixel devices, addressing a zero-day vulnerability (CVE-2024-32896)

A security researcher has published details and proof-of-concept (PoC) exploit code for a critical vulnerability (CVE-2024-37051)

The campaign begins with a seemingly innocuous phishing email containing an HTML attachment disguised as a routine document

CVE-2024-35213 could allow attackers to trigger a denial-of-service (DoS) condition or even execute malicious code on affected systems.


CVE-2024-30299 impacts Adobe FrameMaker Publishing Server and is rated with a critical CVSSv3.1 base score of 10.0

ASEC has published a report detailing a significant shift in the tactics employed by the Bondnet threat actor

The Black Basta ransomware group may have exploited a previously unknown vulnerability (CVE-2024-26169) in Windows Error Reporting Service

A security researcher has published a PoC exploit code for a CVE-2024-27801 vulnerability affecting multiple Apple platforms

Videolan, the organization behind the popular VLC media player, has released urgent security updates to address two critical vulnerabilities

SuiteCRM has released urgent security patches to address multiple critical vulnerabilities that could expose sensitive customer data and compromise system integrity

Cybersecurity researchers at Trend Micro have unveiled a previously undocumented backdoor malware dubbed "Noodle RAT,"

CVE-2024-35241 and CVE-2024-35242, both involve command injection attacks through malicious git/hg branch names