
 Do Son
In mid-October 2025, engineers discovered an architectural flaw in the AMD Zen 5 series processors related to...
Latest news

Many users encounter the 0x80070103 error code when attempting to download and install driver updates through Windows...

For years, Windows 10 lacked support for Bluetooth audio sharing—a feature that has only recently entered testing...

In his latest Power On newsletter, Bloomberg journalist Mark Gurman reported that Apple is expected to release...

If you are using Windows 11 version 24H2 or 25H2, you may have noticed some peculiar behavior...

According to a report by The Wall Street Journal, Elon Musk’s SpaceX is expected to secure a...

According to Bloomberg journalist Mark Gurman in his latest Power On newsletter, Apple retail employees have been...

Researchers at SEQRITE Labs have uncovered a stealthy cyber espionage campaign dubbed “Operation SkyCloak”, which has been...

Fortinet’s FortiGuard Labs has identified a widespread cloud abuse campaign, dubbed “TruffleNet,” that leverages stolen AWS credentials...
Tap-and-Steal: Over 760 Android Apps Exploit NFC/HCE for Payment Card Theft in Global Financial Scam

Tap-and-Steal: Over 760 Android Apps Exploit NFC/HCE for Payment Card Theft in Global Financial Scam
Researchers from Zimperium zLabs have uncovered a rapidly growing cybercrime trend involving Android applications that abuse NFC...

CVE-2024-20380 could allow unauthenticated, remote attackers to crash ClamAV services, causing a Denial-of-Service (DoS) condition.

A detailed analysis by Sucuri has uncovered a sophisticated malware campaign that has shifted strategies to become more elusive and harder to detect

A recent security advisory has shed light on a vulnerability (CVE-2024-32462) within Flatpak, a popular framework for packaging

The DuneQuixote campaign, active since at least February 2023, utilizes a custom malware known as "CR4T" alongside droppers

GhostLocker 2.0 builds upon the original version, demonstrating the active development and sophistication of this threat

Keycloak, a widely used open-source solution for authentication and authorization, has released important security updates addressing multiple flaws

Further complicating the malware's capabilities was the introduction of the previously undocumented Kaolin RAT.

This critical vulnerability (CVE-2024-28890) allows attackers to upload malicious files of dangerous types to a vulnerable website

Security researchers have uncovered a persistent, multi-component virus known as OfflRouter that has been quietly infecting Ukrainian systems

The attack typically begins with cybercriminals scanning for internet-exposed Kubernetes workloads running vulnerable OpenMetadata instances

HashiCorp has issued an urgent security advisory regarding a critical vulnerability (CVE-2024-3817) within its widely used go-getter library

Researchers have uncovered a dangerous new variant of the Redline Stealer malware that uses clever obfuscation tactics

PSIRT has confirmed that proof-of-concept exploit code exists for the IMC command injection vulnerability (CVE-2024-20295

SoumniBot malware is notable for its employment of unconventional obfuscation techniques centered on manipulating the Android manifest file

Cybersecurity researchers are tracking a significant escalation in activity from the GOLD IONIC ransomware group

Mamont malware, currently targeting Russian-speaking individuals, masquerades as a fake Google Chrome app to trick unsuspecting users

the cybersecurity landscape faces a formidable threat in the form of "Mobile NotPetya," a potential zero-click, wormable mobile malware
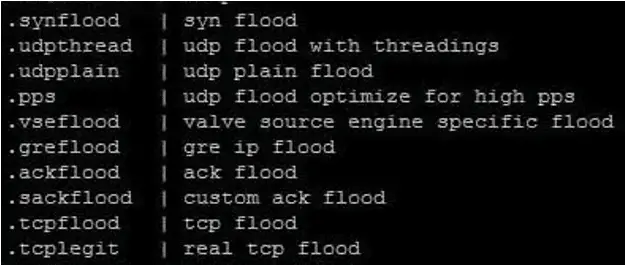
This vulnerability, found in the TP-Link Archer AX21's web management interface, allows hackers to inject malicious code without needing the router's password

The Evil Ant ransomware, written in Python and compiled using PyInstaller, targets a wide array of files in a victim's folders

To increase their attacks' success rate, TA427 often impersonates respected members of the foreign policy community.

A new report by cybersecurity firm Resecurity highlights a marked increase in misinformation campaigns and hacktivist activity targeting the Philippines

Security researchers published the technical details and PoC exploit code for a dangerous zero-day CVE-2024-21338 vulnerability