
 Do Son
In a recent Windows 11 Insider build, Microsoft released an update addressing a long-standing issue where the...
Latest news

The Jenkins project has issued a major security advisory addressing a wave of vulnerabilities, including high-severity flaws...

The Internet Systems Consortium (ISC) has issued a security advisory warning users of a denial-of-service (DoS) vulnerability...

The Wordfence Threat Intelligence team has issued an urgent warning about CVE-2025-11533, a critical privilege escalation vulnerability...

The Google Chrome team has urgently promoted Chrome version 142 to the stable channel for Windows, Mac,...

The Socket Threat Research Team has uncovered an extensive supply chain attack targeting the npm ecosystem, involving...

Security researcher Crnkovic has disclosed three critical vulnerabilities — CVE-2025-9152, CVE-2025-10611, and CVE-2025-9804 — in WSO2 API...

In a study titled “TEE.fail: Breaking Trusted Execution Environments via DDR5 Memory Bus Interposition,” researchers from Georgia...

The AhnLab Security Intelligence Center (ASEC) has published a new report revealing that the Trigona ransomware threat...

Researchers from the Internet Initiative Japan (IIJ) have analyzed a previously unknown malware loader that can simultaneously...

Successful exploitation of CVE-2023-6154 (CVSS 7.8) requires the attacker to have local access to the target machine.

A new report released by AhnLab Security Intelligence Center (ASEC) uncovers a disturbing tactic hackers are using to spread malware
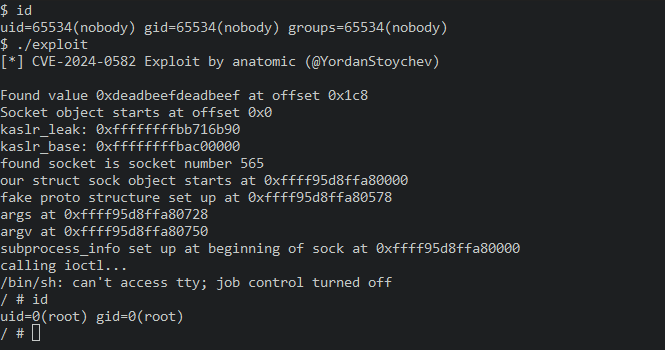
Researchers have provided a detailed analysis of the CVE-2024-0582 vulnerability, including a proof-of-concept (PoC) exploit

In a startling discovery, the Phylum Research Team has exposed a malicious npm package masquerading as a legitimate toolkit

CVE-2024-23538 and CVE-2024-23539: These vulnerabilities stem from improper neutralization of special elements used in an SQL command

Cisco has issued a critical warning about a widespread password spraying campaign targeting Remote Access VPN (RAVPN)

A report by CyberArk reveals a sinister trend: the rise of 'infostealer' malware specifically designed to steal web session cookies.

The CVE-2024-27281 vulnerability could allow attackers to execute arbitrary code remotely on systems using affected versions of RDoc
A severe backdoor vulnerability (designated CVE-2024-3094) has been unearthed in versions 5.6.0 and 5.6.1 of the widely used XZ

Stagg explains that the CVE-2024-0333 vulnerability stemmed from a peculiarity in how Chrome handles CRX files

CVE-2023-50969 (CVSS 9.8), could allow attackers to bypass security rules designed to prevent common web attacks like SQL injection and XSS

Security researchers at Fox-IT have uncovered a significantly enhanced version of the Vultur Android banking malware.

The CVE-2024-1212, vulnerability allows for unauthenticated command injection, potentially giving attackers full control of affected systems

CRIL have exposed a worrying nexus between recent Solana wallet draining attacks and the notorious MS Drainer malware

The CVE-2024-0980 (CVSS 7.1) vulnerability stems from flaws in the auto-update service of Okta Verify for Windows

PyPi, a vital repository for open-source software, has taken the drastic step of temporarily halting new user registrations and project creation

Security researchers at Kaspersky Labs have uncovered a dangerous new variant of the DinodasRAT malware that targets Linux operating systems
CVE-2023-6371: "High" Severity XSS in Wiki Pages: This vulnerability could allow an attacker to inject malicious code into Wiki pages

Synology has released a critical security advisory detailing multiple vulnerabilities in their Surveillance Station software

A new report from EclecticIQ analysts has uncovered a sophisticated cyber espionage campaign dubbed "Operation FlightNight"

Security researchers have uncovered a critical vulnerability (CVE-2024-28872) in Stork, a popular open-source network monitoring tool

CVE-2024-1313 exposes a vulnerability in Grafana, allowing any user, even those outside the snapshot owner's organization