
 Do Son
The Symantec Threat Hunter Team has uncovered two major cyber intrusions in Ukraine attributed to Russian-aligned threat...
Latest news

Progress Software Corporation has issued a security advisory warning of a high-severity vulnerability in its MOVEit Transfer...

 cybernewswire
Silver Spring, USA/ Maryland, 30th October 2025, CyberNewsWire

Microsoft recently released its Q1 FY2026 financial results, revealing that surging demand for cloud and AI services...

Shortly after last week’s large-scale AWS outage, Microsoft’s Azure cloud platform also experienced a significant service disruption,...

OpenAI has officially announced the expansion of its AI video creation platform, Sora App, into the Asian...

Earlier in 2025, OpenAI released its own open-source artificial intelligence models, namely GPT-OSS-20B and GPT-OSS-120B, both of...

OpenAI’s AI video creation tool Sora has ignited legal controversy following the debut of its new “Cameo”...

The Microsoft Design Team recently unveiled a new set of icons for Microsoft 365, now available across...

Founded in 2009 and long celebrated as one of the most popular AI-powered writing assistants, Grammarly has...

A recent security advisory from Veridium has exposed a series of significant vulnerabilities in their popular VeridiumID authentication platform

This campaign delivers the Rhadamanthys Stealer, an advanced Malware-as-a-Service (MaaS), through a complex

Ivanti has released an urgent security advisory detailing multiple critical vulnerabilities affecting their popular ICS and Policy Secure gateways

Security researchers at ReversingLabs have uncovered a new threat vector within the popular Visual Studio Code (VS Code) Marketplace

A researcher found multiple high-severity vulnerabilities in the REHub WordPress theme and the associated REHub Framework plugin

The expansion of the fake e-shop campaign to target 18 banks in Malaysia, coupled with its reach into Vietnam and Myanmar
Consulting is a big part of the IT industry, as companies often find themselves in need of...

Two of these vulnerabilities, labeled CVE-2024-29745 and CVE-2024-29748, are already being exploited by bad actors

threat actors are targeting consumer users, particularly younger audiences drawn to popular video games, by promoting cracked software

Check Point Research has lifted the veil of anonymity surrounding two cybercrime actors responsible for recent Agent Tesla malware campaigns

VMware has released critical security patches to address multiple vulnerabilities in its SD-WAN (Software-Defined Wide Area Network) solution
A new report highlights a disturbing increase in targeted phishing attacks launched by a loosely affiliated group of cybercriminals

The flaw, designated CVE-2024-3159, involves an out-of-bounds memory access vulnerability in the V8 JavaScript engine.

A new report from McAfee Labs reveals a troubling evolution in the PikaBot malware campaign, showcasing an alarming range of infection vectors
The vulnerability, designated CVE-2024-2879 with a CVSS score of 9.8, could allow unauthenticated attackers to inject malicious SQL code

A newly updated variant of the StrelaStealer malware is actively targeting organizations across Europe, according to a recent report
The flaw, designated as CVE-2024-2389, could give attackers unfettered access to sensitive network infrastructure.

The flaw, tracked as CVE-2024-29834, enables unauthorized users to make changes to sensitive data streams and system access rules.
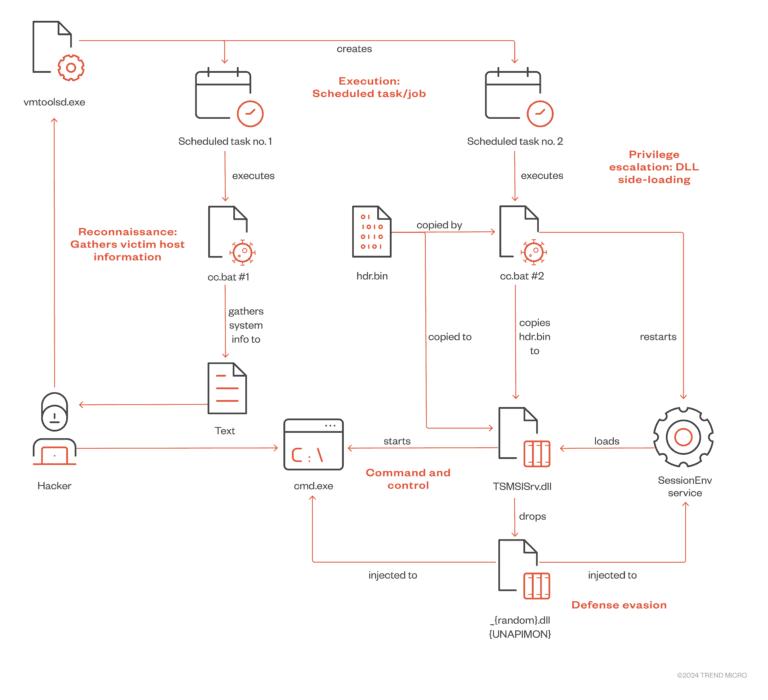
In a cyberespionage campaign attributed to Earth Freybug, security researchers from Trend Micro observed a unique malware, dubbed UNAPIMON

Octopus Deploy has released a security advisory and subsequent patches to address a critical vulnerability (CVE-2024-2975

The most serious of these vulnerabilities (CVE-2024-21473) carries a CVSS score of 9.8 and could allow attackers to corrupt device memory

JumpServer has recently been found to contain CVE-2024-29201 and CVE-2024-29202 that could allow attackers to execute arbitrary code remotely