
 Do Son
PayPal, the U.S.-based payments giant, has announced a strategic partnership with OpenAI, adopting the company’s newly introduced...
Latest news

MediaTek has announced the launch of the Kompanio 540, a processor purpose-built for the education market, promising...

When Microsoft released the Windows 11 24H2 update in 2024, it was rolled out first to Microsoft...

At its Adobe Max 2025 annual creativity conference, Adobe not only unveiled a series of AI-driven innovations...

OpenAI has officially announced the completion of its long-anticipated and closely watched corporate restructuring, marking its transformation...

At the Money20/20 financial conference held in Las Vegas, Jennifer Bailey, Vice President of Apple Pay and...

Adobe has recently unveiled a major update to its generative AI suite Firefly, dramatically expanding its capabilities...

The AhnLab Security Intelligence Center (ASEC) has published an in-depth analysis of the Gunra ransomware group, which...

Cybersecurity researchers at ThreatFabric have discovered a new Android banking Trojan dubbed Herodotus, a malware strain that...

The Docker Compose project has disclosed a high-severity path traversal vulnerability tracked as CVE-2025-62725 (CVSS v4 8.9),...

The vulnerability (CVE-2024-23755, CVSS 8.4) affects both macOS and Windows versions of the ClickUp Desktop app.

The employment of WINELOADER, endowed with features overlapping with other APT29 malware families such as BURNTBATTER and MUSKYBEAT
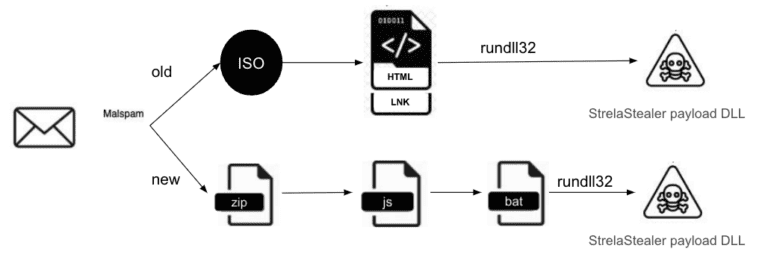
Researchers at Unit 42 have uncovered a major new attack campaign deploying an updated version of the StrelaStealer malware

CVE-2024-29190 allows attacker to trick the MobSF server into making requests to internal or otherwise inaccessible resources within your network

AcidPour malware, like its predecessor, is tailored to attack Linux-based systems. This broad category includes everything

A serious security vulnerability (CVE-2024-30156) has been uncovered in Varnish Cache, a widely used tool for boosting website speed
For years, drones have been seen as a technological marvel, offering a new perspective for photography, delivery,...

a trend in China-linked cyberattacks: a sustained focus on compromising Operational Technology environments within critical infrastructure

The vulnerabilities in question, CVE-2024-29944, and CVE-2024-29943, were expertly exploited by researcher Manfred Paul (@_manfp)

Mandiant assesses with moderate confidence that UNC5174 operates as an initial access broker for the Chinese MSS.

A security researcher has published details and proof-of-concept (PoC) code for a Windows CVE-2023-36424 vulnerability

Curious Serpens has long been a harbinger of cyber espionage, with a notorious history of targeting the aerospace and energy sectors for espionage

Given the severity of CVE-2024-27438, Apache Doris users are strongly advised to upgrade to version 2.0.5 or 2.1.x immediately

a new evolution of the notorious Sysrv botnet exhibits sophisticated tactics, including the abuse of a Google subdomain to spread its payload

The malware installs AteraAgent, legitimate remote administration software known to be abused by the TA450 hacking group

PoC code releases for a severe vulnerability (CVE-2023-48788) in the Fortinet FortiClient Enterprise Management Server (EMS)

Unsuspecting users who open these attachments unwittingly unleash the AceCryptor-packed Rescoms RAT onto their systems.

These flaws, tracked as CVE-2024-1147 and CVE-2024-1148, could allow attackers to upload and download sensitive files

The vulnerability, tracked as CVE-2024-2054, could allow unauthenticated attackers to execute malicious code on affected servers.

Security experts have sounded the alarm on a widespread malware campaign employing the notorious StealC Infostealer

A sophisticated new malware campaign dubbed "PhantomBlu" is on the prowl, preying on US-based organizations

A major security flaw (CVE-2024-1800) has been discovered in the Progress Telerik Report Server, a widely used business reporting solution