Skip to content
October 13, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CVE-2022-45047: Apache MINA SSHD unsafe deserialization vulnerability CVE-2022-45047
  • Vulnerability

CVE-2022-45047: Apache MINA SSHD unsafe deserialization vulnerability

Do Son November 15, 2022
Read More Read more about CVE-2022-45047: Apache MINA SSHD unsafe deserialization vulnerability
What Does It Mean To Sort Out Important Data? tech-mac
  • Technique

What Does It Mean To Sort Out Important Data?

Do Son November 15, 2022
Read More Read more about What Does It Mean To Sort Out Important Data?
How To Conduct A Study With A Very Large Amount Of Data tech-data
  • Technique

How To Conduct A Study With A Very Large Amount Of Data

Do Son November 15, 2022
Read More Read more about How To Conduct A Study With A Very Large Amount Of Data
CVE-2022-3977: Linux kernel Local Privilege Escalation Vulnerability CVE-2022-3977
  • Vulnerability

CVE-2022-3977: Linux kernel Local Privilege Escalation Vulnerability

Do Son November 13, 2022
Read More Read more about CVE-2022-3977: Linux kernel Local Privilege Escalation Vulnerability
Why is PIM essential for composable commerce? tech-security
  • Technique

Why is PIM essential for composable commerce?

Do Son November 12, 2022
Read More Read more about Why is PIM essential for composable commerce?
CVE-2022-40303 & CVE-2022-40304: RCE flaws in Apple iOS, macOS CVE-2022-40303
  • Vulnerability

CVE-2022-40303 & CVE-2022-40304: RCE flaws in Apple iOS, macOS

Do Son November 11, 2022
Read More Read more about CVE-2022-40303 & CVE-2022-40304: RCE flaws in Apple iOS, macOS
Different Classifications of Vulnerabilities and the Tools to Help You Find Them tech-security
  • Technique

Different Classifications of Vulnerabilities and the Tools to Help You Find Them

Do Son November 11, 2022
Read More Read more about Different Classifications of Vulnerabilities and the Tools to Help You Find Them
CVE-2022-20465: Google Pixel lock screen bypass might affect Android vendors CVE-2022-20465
  • Vulnerability

CVE-2022-20465: Google Pixel lock screen bypass might affect Android vendors

Do Son November 10, 2022
Read More Read more about CVE-2022-20465: Google Pixel lock screen bypass might affect Android vendors
How to Sweep Your Property for Bugging Devices tech-camera
  • Technique

How to Sweep Your Property for Bugging Devices

Do Son November 9, 2022
Read More Read more about How to Sweep Your Property for Bugging Devices
How to Access Netflix from Anywhere with a Proxy
  • Technique

How to Access Netflix from Anywhere with a Proxy

Do Son November 9, 2022
Read More Read more about How to Access Netflix from Anywhere with a Proxy
Intel rolls out BIOS updates to fix LPE (CVE-2022-26006 & CVE-2022-21198) flaws Intel graphics drivers Intel 14A, EUV lithography Intel CHIPS Act Intel Government Investment Intel Layoffs, Wafer Foundry CVE-2022-21198
  • Vulnerability

Intel rolls out BIOS updates to fix LPE (CVE-2022-26006 & CVE-2022-21198) flaws

Do Son November 9, 2022
Read More Read more about Intel rolls out BIOS updates to fix LPE (CVE-2022-26006 & CVE-2022-21198) flaws
CVE-2022-39328: Critical vulnerability affects open-source analytics Grafana CVE-2022-39328
  • Vulnerability

CVE-2022-39328: Critical vulnerability affects open-source analytics Grafana

Do Son November 9, 2022
Read More Read more about CVE-2022-39328: Critical vulnerability affects open-source analytics Grafana
How the Right Digital Banking Platform Can Help Your Bank Personalize Customer Engagement tech-proto
  • Technique

How the Right Digital Banking Platform Can Help Your Bank Personalize Customer Engagement

Do Son November 9, 2022
Read More Read more about How the Right Digital Banking Platform Can Help Your Bank Personalize Customer Engagement
Top 3 Free Tools for SQL Database Comparison tech-work
  • Technique

Top 3 Free Tools for SQL Database Comparison

Do Son November 9, 2022
Read More Read more about Top 3 Free Tools for SQL Database Comparison
Write My Essay Cheap Without Compromising on Quality tech-writing
  • Technique

Write My Essay Cheap Without Compromising on Quality

Do Son November 8, 2022
Read More Read more about Write My Essay Cheap Without Compromising on Quality
What Are IT Security OKRs And How Do They Work? tech-smart
  • Technique

What Are IT Security OKRs And How Do They Work?

Do Son November 8, 2022
Read More Read more about What Are IT Security OKRs And How Do They Work?
Play Store: What You Need To Consider Before Downloading Apps tech-Google
  • Technique

Play Store: What You Need To Consider Before Downloading Apps

Do Son November 8, 2022
Read More Read more about Play Store: What You Need To Consider Before Downloading Apps
Researcher releases PoC for macOS Ventura code execution bug (CVE-2022-26730) CVE-2022-26730 PoC
  • Vulnerability

Researcher releases PoC for macOS Ventura code execution bug (CVE-2022-26730)

Do Son November 8, 2022
Read More Read more about Researcher releases PoC for macOS Ventura code execution bug (CVE-2022-26730)
CVE-2022-33684: Apache Pulsar C++ Client man-in-the-middle attack CVE-2022-33684
  • Vulnerability

CVE-2022-33684: Apache Pulsar C++ Client man-in-the-middle attack

Do Son November 7, 2022
Read More Read more about CVE-2022-33684: Apache Pulsar C++ Client man-in-the-middle attack
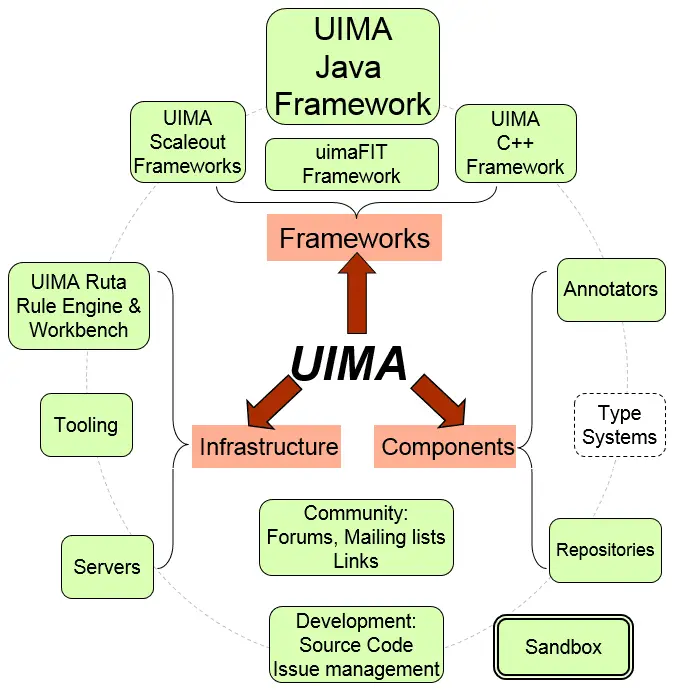
CVE-2022-32287: Apache UIMA directory traversal vulnerability CVE-2022-32287
  • Vulnerability

CVE-2022-32287: Apache UIMA directory traversal vulnerability

Do Son November 7, 2022
Read More Read more about CVE-2022-32287: Apache UIMA directory traversal vulnerability
How to become an Ethical Hacker? AdaptixC2 Abuse, Russian Cybercrime RondoDox Botnet, Exploit Shotgun China Cyber Power, Red Hackers Nvidia cyberattack
  • Technique

How to become an Ethical Hacker?

Do Son November 7, 2022
Read More Read more about How to become an Ethical Hacker?
The Complete Guide to Intralinks Data Rooms tech-proto
  • Technique

The Complete Guide to Intralinks Data Rooms

Do Son November 7, 2022
Read More Read more about The Complete Guide to Intralinks Data Rooms
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
πŸ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

πŸ›‘οΈ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

πŸ™

GitHub Issues
Auto-create alert tickets without duplication.

πŸ“¬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

πŸ”€

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days β†’

🚨 Active Exploits in the Wild

  • CVE-2026-104935CVSS 8.6
    Authentication bypass by spoofing in ICS before version 25.1.3.0 allows a remote unauthenticated attacker to execute arbitrary commands....
    CISA KEV📅 Added to KEV: Oct 13, 2026
  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2026-105133CVSS 6.9
    A vulnerability was detected in Ahsay AhsayCBS up to 10.3.2. This affects the function checkSysPwd of the file...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2023-22894CVSS 4.9
    Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2016-3081CVSS 8.1
    Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled,...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-3306CVSS 10.0
    The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-5477CVSS 7.5
    named in ISC BIND 9.x before 9.9.7-P2 and 9.10.x before 9.10.2-P3 allows remote attackers to cause a denial...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2021-3199CVSS 9.8
    Directory traversal with remote code execution can occur in /upload in ONLYOFFICE Document Server before 5.6.3, when JWT...
    CISA KEV📅 Added to KEV: Oct 8, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-86360CVSS 9.6
    Dell System Update, versions prior to 2.3.0.0, contains an Improper Limitation of a Pathname to a Restricted Directory...
    📅 Updated: Oct 13, 2026
  • CVE-2026-92892CVSS 9.0
    Potential arbitrary code execution, under specific configurations.
    📅 Updated: Oct 13, 2026
  • CVE-2026-55183CVSS 9.6
    RClone Manager is a cross-platform GUI application designed to help users manage Rclone remotes efficiently. Prior to 0.2.7,...
    📅 Updated: Oct 13, 2026
  • CVE-2026-106173CVSS 9.8
    A improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiSIEM 7.5.0 may...
    📅 Updated: Oct 13, 2026
  • CVE-2020-37279CVSS 9.2
    easy-pdf-merge 0.1.0 through 0.2.6 contains an OS command injection vulnerability that allows attackers to execute commands by injecting...
    📅 Updated: Oct 13, 2026
  • CVE-2026-105445CVSS 9.4
    An Incorrect Privilege Assignment vulnerability in Docker Hub's account-to-organization conversion feature allowed an authenticated attacker to reassign a...
    📅 Updated: Oct 13, 2026
  • CVE-2026-94603CVSS 10.0
    Podman is a tool for managing OCI containers and pods. From 4.4.0 until 5.8.8 and 6.1.3, podman run...
    📅 Updated: Oct 13, 2026
  • CVE-2026-77459CVSS 9.9
    Argo CD is a declarative, GitOps continuous delivery tool for Kubernetes. From 2.10.0 until 3.3.15, 3.4.10, 3.5.4, and...
    📅 Updated: Oct 13, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
Β© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.