
 Do Son
Rockwell Automation has issued a critical security advisory regarding a remote code execution (RCE) vulnerability affecting its...
Latest news

Pakistan has found itself in the crosshairs of a sophisticated ransomware campaign, as the country’s National Cyber...

Google recently announced that it has begun leveraging large language models (LLMs) to combat “invalid traffic” (IVT)—fraudulent...

Pirated games have long been a risky endeavor, but recent research from Trellix reveals just how dangerous...

Google has recently released Beta versions of its Contacts and Phone apps on Android, introducing a brand-new...

Microsoft has recently announced a new test version of the Xbox PC App for Windows 11 PCs...

Google has unveiled its most lightweight open-source Gemma model to date—Gemma 3 270M—with only 270 million parameters....

Security researchers at JFrog Security Research have uncovered two critical vulnerabilities in Flowise, an open-source generative AI...

A recent investigation by ReversingLabs has revealed how a targeted phishing attack led to the compromise of...

After nearly eighteen years of operation in Russia, Sony, the Japanese multinational conglomerate, has formally announced its...

VMware has issued a security notice to alert that many VMware products are affected by Log4j2 remote code execution vulnerability CVE-2021-44228

Online security has become a quintessential aspect of business management. With more cyber threats developing every day...

This version is an emergency update of Google Chrome to fix vulnerabilities, of which CVE-2021-4102 have been exploited by hackers in the wild

Startups are companies that are just starting out on the market with a unique idea but without...

the details of the vulnerability and the POC of the Microsoft Windows Active Directory domain service privilege escalation vulnerability have been disclosed

Fast and furious movies have been all a success. It’s filled with fancy cars, great dialogue, action...

Businesses today more and more use SEO tools to promote their products or services. Companies start advertising...

According to the FBI, there are more than 2 million burglaries in the U.S. each year, meaning...

the details of Apache Log4j2 remote code execution vulnerability were disclosed, and attackers could use the vulnerability to execute code

Firefox Monitor simply recorded this incident: the leaked Gravatar data only contained emails, names, and usernames.

If you run email marketing campaigns or send out daily mass emails on a regular basis, having...

Data breaches are becoming more and more common. In fact, the number of data breaches reported in...

On December 4, 2021, a security researcher revealed an arbitrary file reading vulnerability in Grafana on the Internet. This is an 0-day vulnerability.

In a report released by Reuters, the news said that nine U.S. State Department employees' iPhones were hacked by NSO spyware.

In today’s world, it is more important than ever to take precautions to ensure that your company...
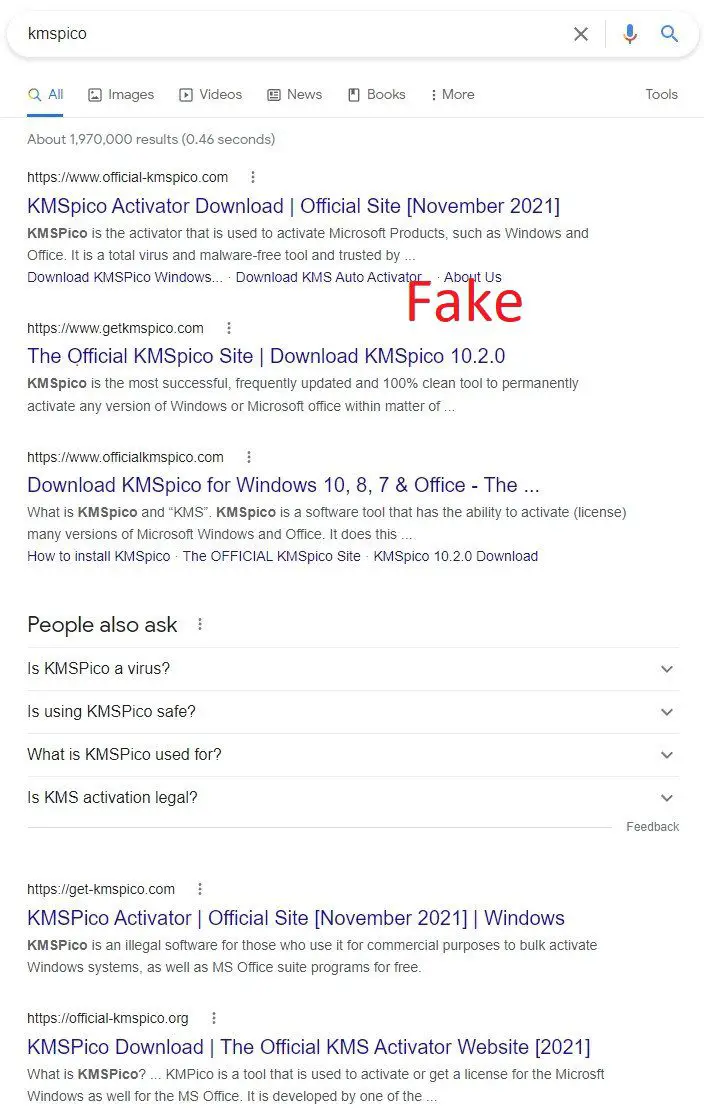
Malicious KMSPico installers mainly embeds malicious software in the activator and then distributes it through the Internet and software forums.

Zoho ManageEngine ServiceDesk Plus authentication bypass vulnerability was exploited in the wild, the vulnerability number is CVE-2021-44077

Do you have some money in your bank account or credit card? Let’s ask another question. How...

Mozilla had issued a risk notice for Mozilla Network Security Services buffer heap overflow, the vulnerability number is CVE-2021-43527

The high-risk security vulnerabilities discovered this time is CVE-2021-39237 and CVE-2021-39238, of which the CVSS score of the latter is as high as 9.3/10

For many looking to launch their tech startup, funding or finding a mortgage/loan is their first and...
People are becoming more interested in Bitcoin as more institutions and merchants worldwide adopt it as a...