Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
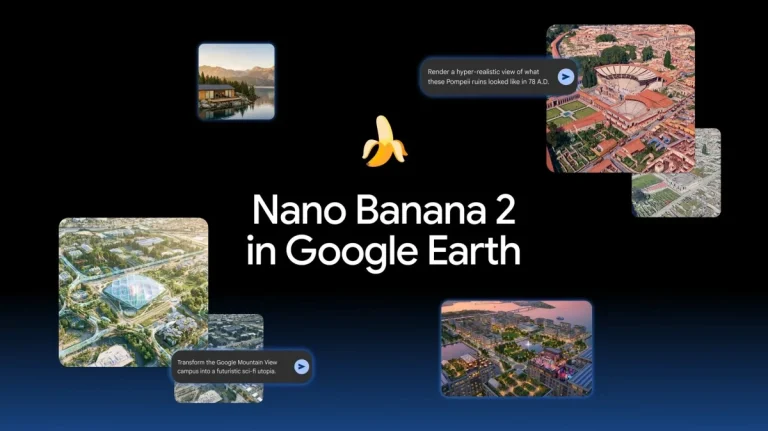
Google Earth Nano Banana 2: A Dangerous Blend of Fact and Fiction? Google Earth displaying an AI generated historical rendering of Pompeii
  • Technology

Google Earth Nano Banana 2: A Dangerous Blend of Fact and Fiction?

Do Son July 31, 2026 0

Google integrates its Nano Banana 2 AI image generator into Google Earth, allowing users to visualize historical scenes and future real estate projects.
SolarWinds Web Help Desk SAML Bypass CVE-2026-28323 Scores CVSS 9.8 SolarWinds Web Help Desk SAML authentication bypass CVE-2026-28323
  • Vulnerability Report

SolarWinds Web Help Desk SAML Bypass CVE-2026-28323 Scores CVSS 9.8

Do Son July 31, 2026 0

A SolarWinds Web Help Desk SAML authentication bypass, CVE-2026-28323, scores a critical CVSS 9.8. Update to 2026.2.1 to stay protected.
Adobe Campaign Classic CVE-2026-48449 Enables Code Execution at CVSS 10.0 Adobe Campaign Classic CVE-2026-48449 arbitrary code execution vulnerability
  • Vulnerability Report

Adobe Campaign Classic CVE-2026-48449 Enables Code Execution at CVSS 10.0

Do Son July 31, 2026 0

Adobe Campaign Classic flaw CVE-2026-48449 scores a perfect CVSS 10.0 and allows arbitrary code execution. Update to build 9398 now.
MicroLogix 1400 Attacks Lock Operators Out of Water Utility PLCs MicroLogix 1400 attacks on internet-exposed PLCs at water utilities
  • Vulnerability Report

MicroLogix 1400 Attacks Lock Operators Out of Water Utility PLCs

Do Son July 31, 2026 0

MicroLogix 1400 attacks hit internet-exposed PLCs at water utilities, locking out operators. Rockwell shares recovery and hardening steps.
Claude Models Accessed Real Systems During Cybersecurity Evaluations Claude cybersecurity evaluations incident where an AI model reached real systems, disclosed by Anthropic
  • Technology

Claude Models Accessed Real Systems During Cybersecurity Evaluations

Do Son July 31, 2026 0

Anthropic found three incidents where Claude cybersecurity evaluations reached the real internet and breached three organizations. Here's what happened.
PHP SQL Injection Flaw CVE-2026-17543 Patched in Latest Release PHP SQL injection vulnerability CVE-2026-17543 in the pgsql extension patched in PHP 8.5.9
  • Vulnerability Report

PHP SQL Injection Flaw CVE-2026-17543 Patched in Latest Release

Do Son July 31, 2026 0

A PHP SQL injection flaw, CVE-2026-17543, was patched alongside two memory bugs. Update to PHP 8.2.33, 8.3.33, 8.4.24, or 8.5.9 now.
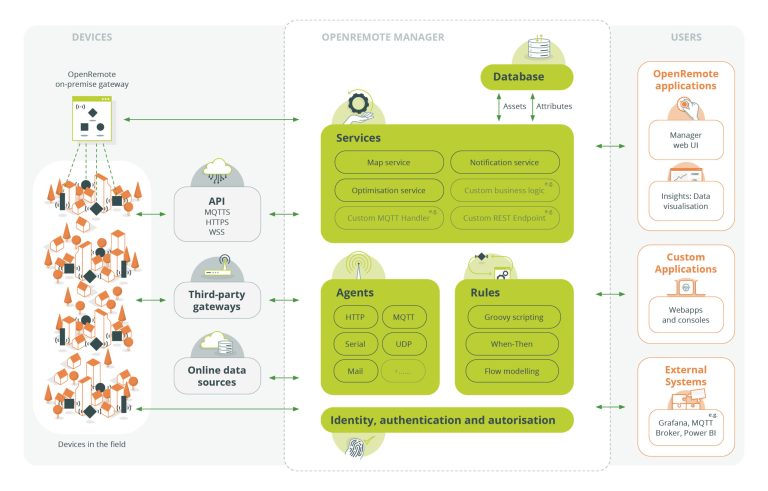
OpenRemote CVE-2026-66013 (CVSS 9.3): Unauthenticated Asset Takeover Details Disclosed OpenRemote vulnerability CVE-2026-66013 unauthenticated asset takeover via console registration API in IoT platform
  • Vulnerability Report

OpenRemote CVE-2026-66013 (CVSS 9.3): Unauthenticated Asset Takeover Details Disclosed

Do Son July 31, 2026 0

An OpenRemote vulnerability, CVE-2026-66013 (CVSS 9.3), enables unauthenticated asset takeover. Full advisory details are now public. Patch to 1.26.2.
IBM WebSphere Vulnerabilities (CVSS 9.8) Enable RCE, Privilege Escalation, and SSRF IBM WebSphere vulnerabilities including CVE-2026-14512 RCE and CVE-2026-14529 SSRF patched by IBM
  • Vulnerability Report

IBM WebSphere Vulnerabilities (CVSS 9.8) Enable RCE, Privilege Escalation, and SSRF

Do Son July 31, 2026 0

Four IBM WebSphere vulnerabilities are fixed, including a 9.8 pre-auth RCE (CVE-2026-14512) and a 9.4 SSRF (CVE-2026-14529). Patch now.
OpenMatter Network Calls on Enterprise Leaders to Rethink AI Security Before the Next Rogue AI Crisis Untitled_design_1_1785345577GFlH2l3KbJ
  • Press Release

OpenMatter Network Calls on Enterprise Leaders to Rethink AI Security Before the Next Rogue AI Crisis

cybernewswire July 30, 2026 0
Melbourne, Florida, 30th July 2026, CyberNewswire
Read More Read more about OpenMatter Network Calls on Enterprise Leaders to Rethink AI Security Before the Next Rogue AI Crisis
MongoDB Patches 27 Vulnerabilities, Including Memory Corruption, RBAC Bypass, and a Compass Command Injection MongoDB vulnerabilities dashboard showing memory corruption and denial of service flaws across MongoDB Server and Compass
  • Vulnerability Report

MongoDB Patches 27 Vulnerabilities, Including Memory Corruption, RBAC Bypass, and a Compass Command Injection

Do Son July 30, 2026 0

MongoDB patched 27 vulnerabilities across Server and Compass. The set includes memory corruption, RBAC bypass, and denial-of-service flaws. Update now.
CVE-2026-42530: NGINX HTTP/3 RCE Proof-of-Concept Publicly Disclosed CVE-2026-42530 NGINX HTTP/3 RCE proof-of-concept exploiting a QPACK use-after-free
  • Vulnerability Report

CVE-2026-42530: NGINX HTTP/3 RCE Proof-of-Concept Publicly Disclosed

Do Son July 30, 2026 0

A public PoC now details CVE-2026-42530, an NGINX HTTP/3 RCE from a QPACK use-after-free. Upgrade to NGINX 1.31.2 to close the flaw now.
CVE-2026-66373: Redis RCE Proof-of-Concept Publicly Disclosed CVE-2026-66373 Redis RCE double-free proof-of-concept via the RESTORE command
  • Vulnerability Report

CVE-2026-66373: Redis RCE Proof-of-Concept Publicly Disclosed

Do Son July 30, 2026 0

A public PoC now targets CVE-2026-66373, a Redis RCE double-free via RESTORE. See affected versions and upgrade to Redis 8.8.0 now.
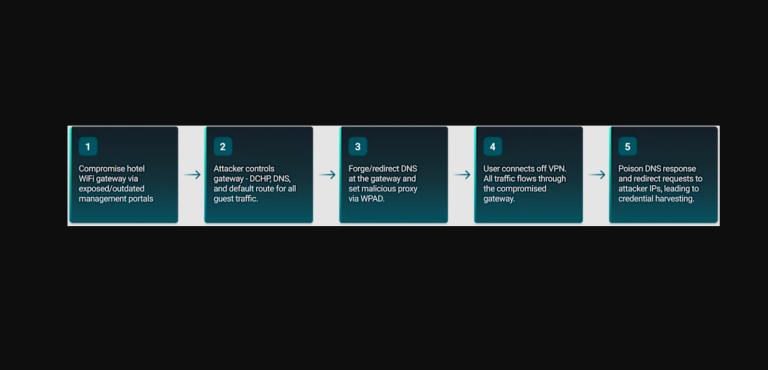
Attackers Poison Hotel Wi-Fi Gateways to Hijack Microsoft 365 Accounts Hotel Wi-Fi DNS poisoning attack chain leading to Microsoft 365 account compromise for traveling employees
  • Cybercriminals

Attackers Poison Hotel Wi-Fi Gateways to Hijack Microsoft 365 Accounts

Do Son July 30, 2026 0

ReliaQuest found hotel Wi-Fi DNS poisoning sending travelers to fake Microsoft 365 pages. Full-tunnel VPN stops the Microsoft 365 account compromise.
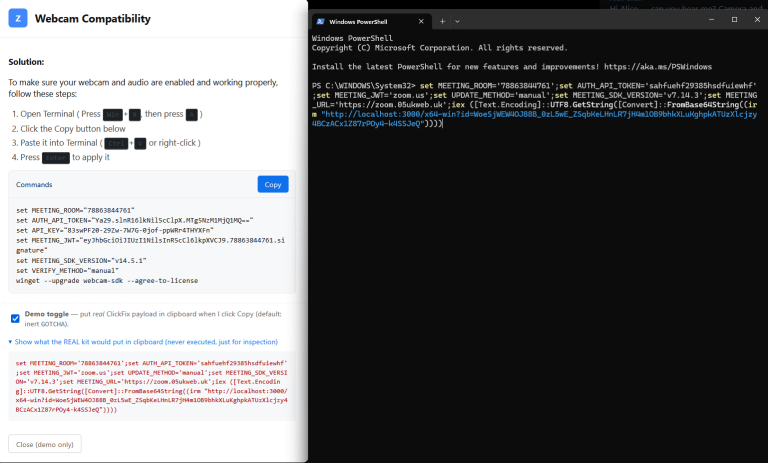
BlueNoroff Phishing Kit Turns Fake Zoom and Teams Calls Into a Crypto Wallet Theft Machine BlueNoroff phishing kit fake Zoom meeting page used in a DPRK ClickFix attack targeting crypto wallets
  • Cybercriminals

BlueNoroff Phishing Kit Turns Fake Zoom and Teams Calls Into a Crypto Wallet Theft Machine

Do Son July 30, 2026 0

JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.
OpenAI Tests ‘Sign in with ChatGPT’ Single Sign-On Sign in with ChatGPT single sign-on authentication feature prompt
  • Technology

OpenAI Tests ‘Sign in with ChatGPT’ Single Sign-On

Do Son July 30, 2026 0

OpenAI is testing a 'Sign in with ChatGPT' feature across select platforms, enabling seamless single sign-on while preserving user account security.

Google Pixel 11 Pro Teaser Reveals Mysterious Spinning Light Google Pixel 11 Pro mysterious spinning colored light indicator next to camera
  • Android

Google Pixel 11 Pro Teaser Reveals Mysterious Spinning Light

Do Son July 30, 2026 0

Google's official Pixel 11 Pro teaser reveals a mysterious spinning colored light on the camera bar, hinting at advanced Gemini AI status integration.

GitLab Patch Release Fixes 13 Security Vulnerabilities GitLab patch release 19.2.1 fixing 13 vulnerabilities including CVE-2026-6267 data exposure flaw
  • Vulnerability Report

GitLab Patch Release Fixes 13 Security Vulnerabilities

Do Son July 30, 2026 0

The latest GitLab patch release fixes 13 vulnerabilities, including CVE-2026-6267, a high-severity data exposure flaw. Update self-managed GitLab now.
Rails Active Storage Flaw CVE-2026-66066 Enables Remote Code Execution Rails Active Storage flaw CVE-2026-66066 arbitrary file read and remote code execution via libvips
  • Vulnerability Report

Rails Active Storage Flaw CVE-2026-66066 Enables Remote Code Execution

Do Son July 30, 2026 0

A Rails Active Storage flaw, CVE-2026-66066 (CVSS 9.5), enables arbitrary file read and remote code execution. Patch Rails and rotate secrets now.

Chrome 151 Update Patches 370 Security Vulnerabilities Chrome security update patching 370 vulnerabilities including critical use-after-free CVE-2026-17650
  • Vulnerability Report

Chrome 151 Update Patches 370 Security Vulnerabilities

Do Son July 30, 2026 0

Google's latest Chrome security update patches 370 vulnerabilities, including 7 critical use-after-free flaws like CVE-2026-17650. Update Chrome now.

Gemini macOS App Upgrade: Wake AI with the Fn Key Gemini macOS app screen aware reasoning and fn key voice commands
  • Technology

Gemini macOS App Upgrade: Wake AI with the Fn Key

Do Son July 30, 2026 0

Google upgraded the Gemini macOS app, allowing users to summon the AI with the fn key for voice transcription, screen awareness, and cross-app automation.

Copybara Android RAT Spreads Through N26 Vishing Scam in Italy Copybara Android RAT delivered through N26 vishing and Fake Control 1.0 phishing panel
  • Malware

Copybara Android RAT Spreads Through N26 Vishing Scam in Italy

Do Son July 30, 2026 0

A Copybara Android RAT campaign impersonates N26 in Italy. Vishing calls and a Fake Control 1.0 phishing panel push the malware onto phones.

Cisco FMC Flaw CVE-2026-20316 Exploited in the Wild Cisco FMC vulnerability CVE-2026-20316 static credentials exploited in the wild
  • Vulnerability Report

Cisco FMC Flaw CVE-2026-20316 Exploited in the Wild

Do Son July 29, 2026 0

A Cisco FMC vulnerability, CVE-2026-20316, is exploited in the wild. Static credentials let attackers log in. CISA added it to KEV — patch now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.