 Do Son
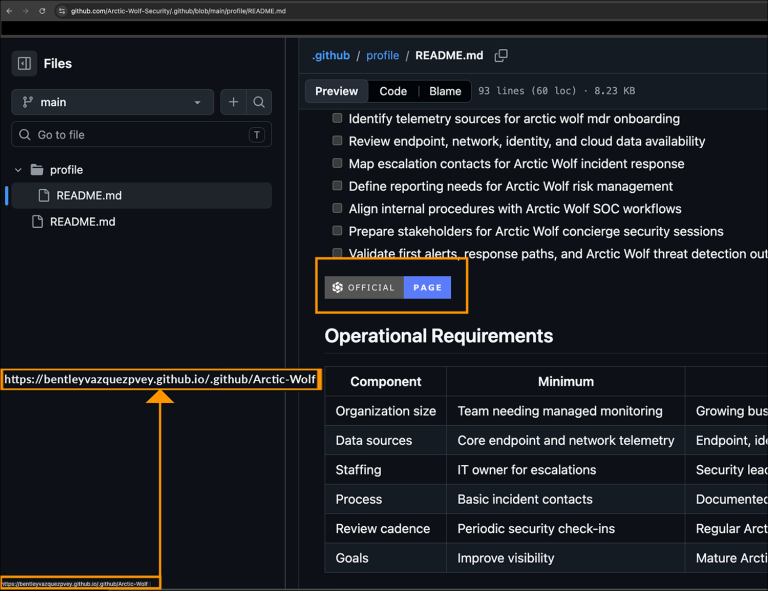
Arctic Wolf found 292 fake GitHub repositories impersonating software vendors to deliver a BoryptGrab-lineage infostealer via DLL side-loading.
DLL side-loading
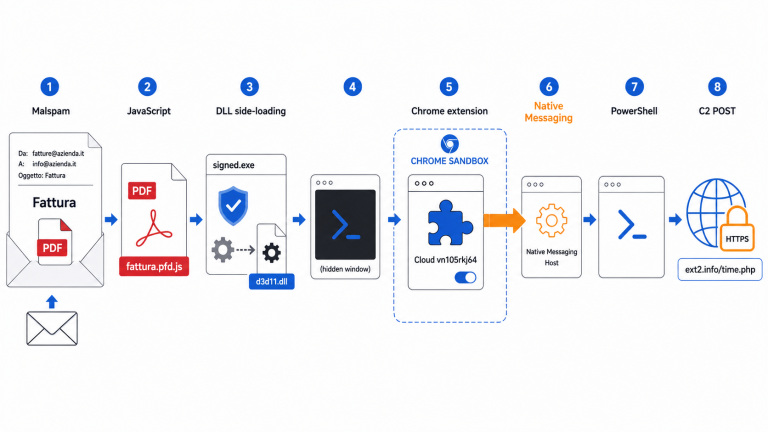
A Native Messaging backdoor pairs a malicious Chrome extension with a local host to run PowerShell, escaping the browser sandbox, says D3Lab.

The dangerous Grandoreiro banking trojan returns. Discover how it utilizes an advanced DLL side loading technique to bypass corporate defenses.
The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia

The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia
Unit 42 uncovers a massive 3-cluster cyberespionage campaign by China-aligned actors in SE Asia using USBFect, Hypnosis loaders, and stealthy RATs.

Elastic Security Labs uncovers BRUSHWORM and BRUSHLOGGER: AI-aided malware using USB drives to steal data from air-gapped financial networks. Update your defenses!

Check Point reveals "TrueChaos," an espionage campaign exploiting a TrueConf zero-day (CVE-2026-3502) to drop malware via fake updates. Patch to 8.5.3 now.
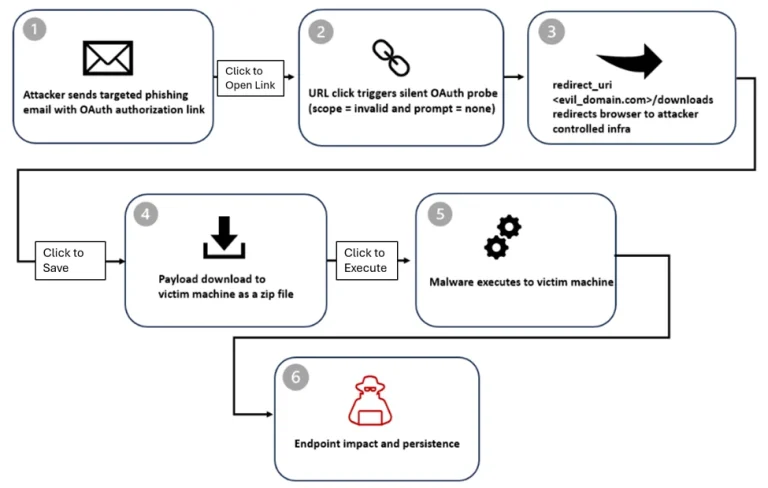
Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.
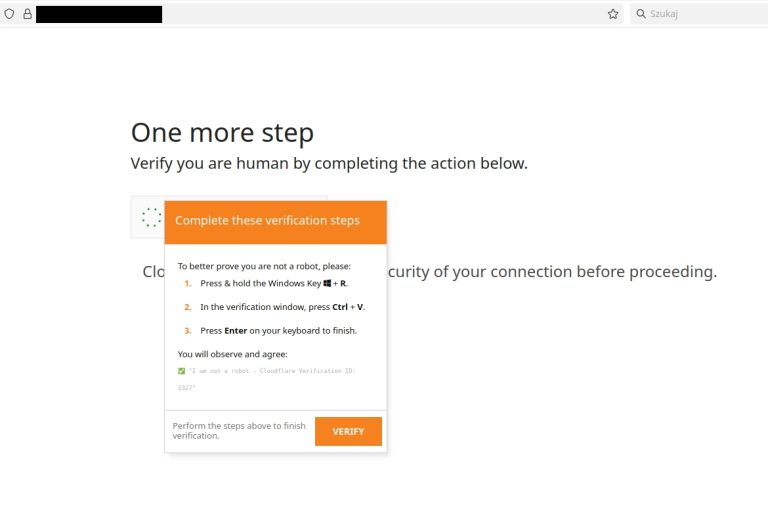
CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.

Lotus Blossom hijacked Notepad++ updates to target admins. The supply chain attack deployed Chrysalis backdoor. Update to v8.9.1 immediately.

Darktrace dissects SnappyBee (Deed RAT), a stealthy Salt Typhoon backdoor. Learn how it uses DLL side-loading & memory hooking to evade modern AV.

Lotus Blossom compromises Notepad++ infrastructure to deploy "Chrysalis" malware. Rapid7 reveals the group using Microsoft Warbird to evade detection.
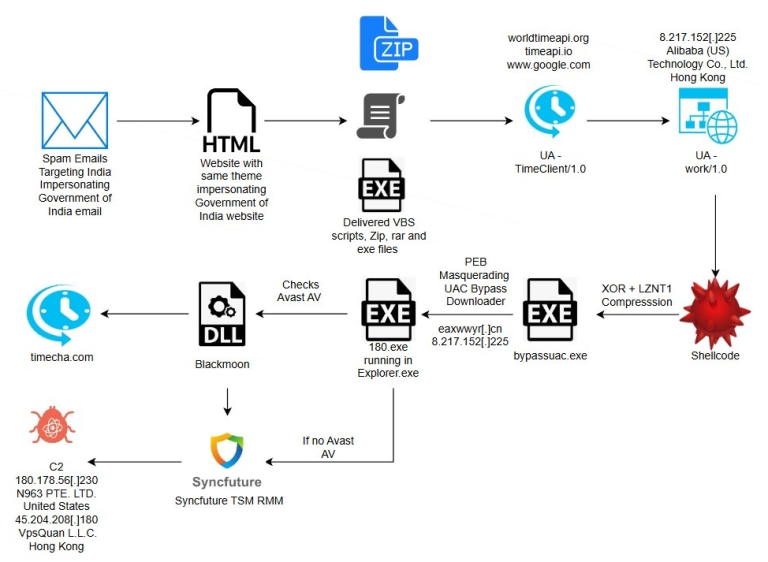
"SyncFuture" spies on Indian users via fake Income Tax emails. This advanced campaign bypasses antivirus & installs Chinese IT tools for total surveillance.

ASEC warns of Larva-25012 using fake Notepad++ installers for Proxyjacking. The malware disables Defender and sells your bandwidth. Check your tasks.

Resecurity finds PDFSIDER, a new APT malware using DLL side-loading and AES-256-GCM encryption to bypass EDR and open covert backdoors.

ASEC exposed PrintMiner, a Monero cryptominer spreading via USB LNK files. It uses DLL Side-Loading (printui.exe) and "Smart Mining" to suspend activity when games or Task Manager are opened.

A new report reveals GONEPOSTAL, a backdoor by Russia's APT28 that hides in Outlook macros and uses email itself as a covert command-and-control channel for espionage.

A new report reveals NotDoor, a backdoor by Russia's APT28 that hides in Microsoft Outlook macros and uses specific email triggers to exfiltrate data and execute commands.

IBM X-Force has exposed QuirkyLoader, a new malware loader that uses DLL side-loading and .NET AOT compilation to deliver Agent Tesla and other threats.
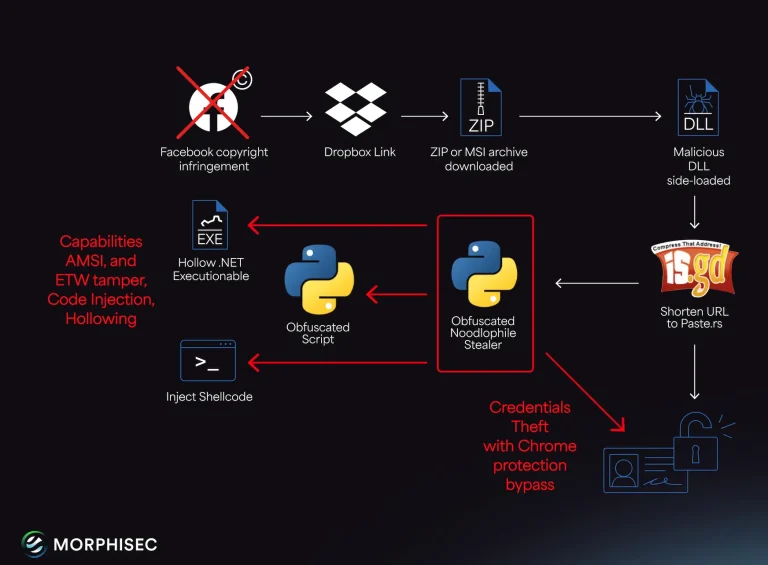
The Noodlophile infostealer has evolved from fake AI platforms to spear phishing, using fake copyright notices and DLL side-loading to target companies.
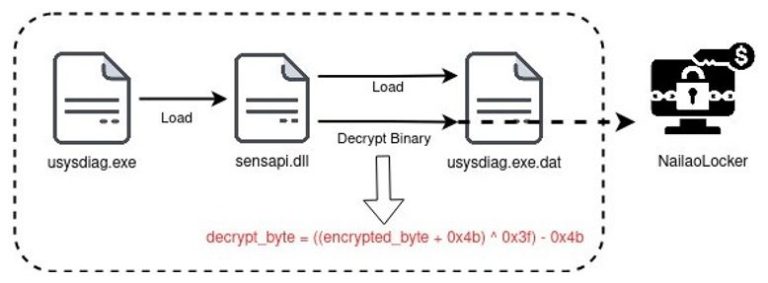
FortiGuard Labs unveils NailaoLocker, a new ransomware using Chinese SM2 encryption and a built-in, non-functional decryptor, suggesting a prototype or decoy.

Unit 42 exposes SLOW#TEMPEST, a new malware variant using advanced CFG obfuscation and indirect function calls to evade static analysis, making it nearly impossible to detect.