 Do Son
A stealthy Twill Typhoon RAT campaign targets APJ organizations. Discover how this threat exploits DLL side loading tradecraft to evade security.
DLL Sideloading
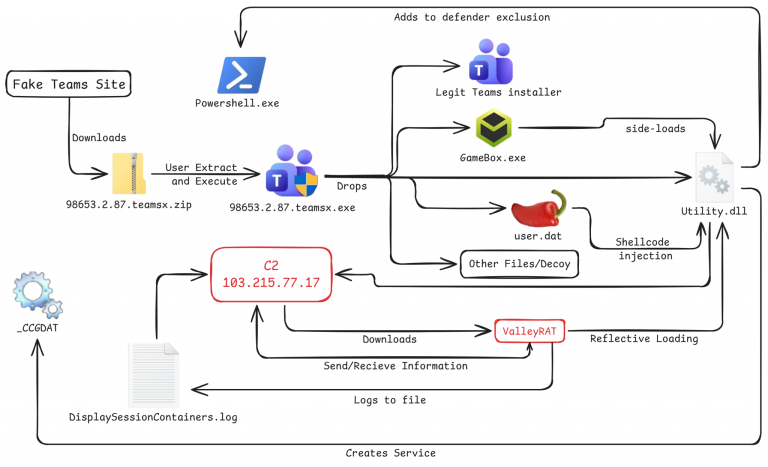
A sophisticated ValleyRAT malware campaign uses fake Microsoft Teams installers and DLL sideloading to evade Windows Defender detection.
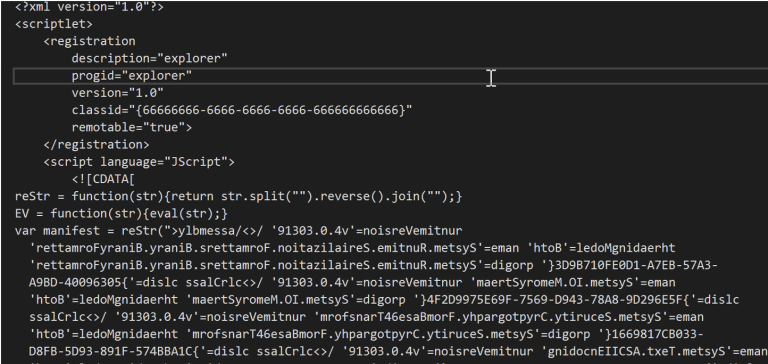
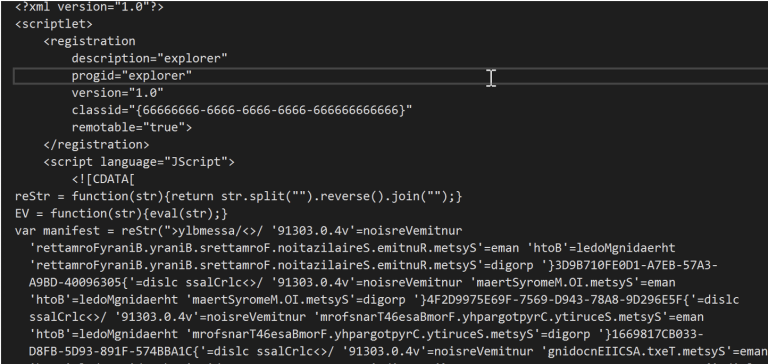
Darktrace exposes Chinese APT Twill Typhoon’s latest campaign using DLL sideloading and Yahoo/Apple CDN lookalikes to deploy a modular .NET RAT.
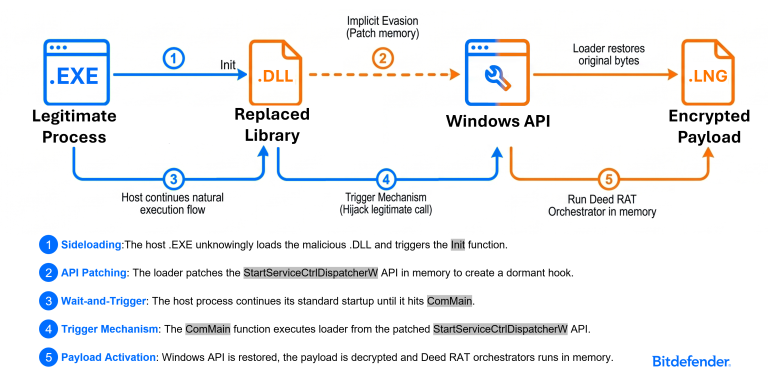
Bitdefender exposes a persistent FamousSparrow campaign using advanced DLL sideloading and Deed RAT to compromise energy infrastructure. Patch now!

Iranian group Seedworm infiltrates global firms using automated Node.js scripts and DLL sideloading via trusted binaries. Protect your credentials now!
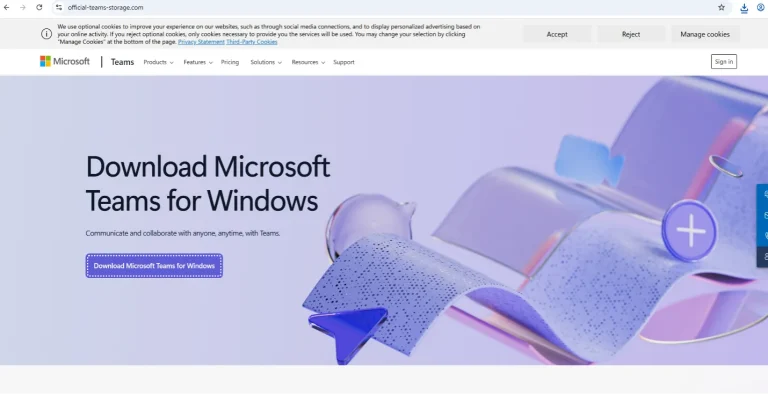
BlueVoyant unmasks "Lorem Ipsum": a well-funded campaign using SEO poisoning and signed MS Teams installers to deploy stealthy backdoors via image files.
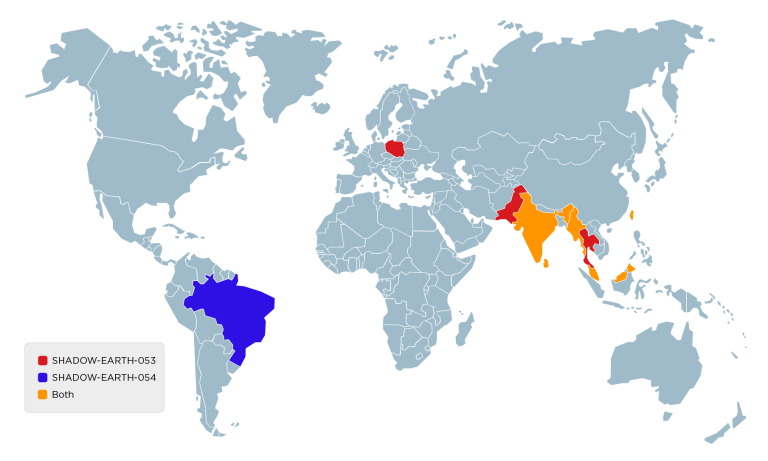
SHADOW-EARTH-053 is breaching governments and NATO using old ProxyLogon flaws and ShadowPad. Learn how this China-aligned group stays hidden via registry loading.
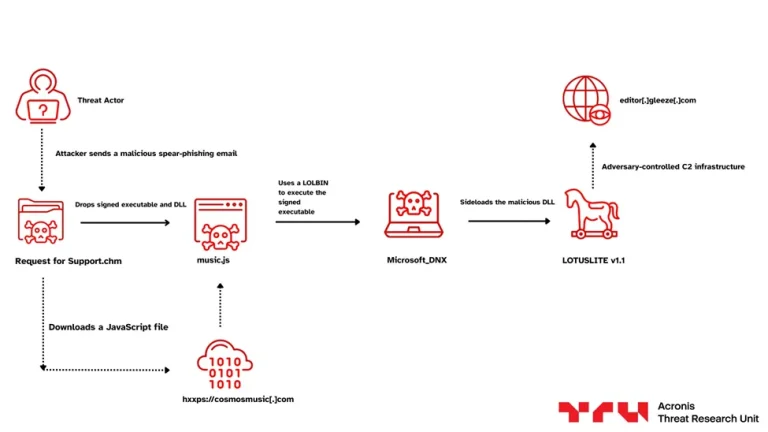
Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.
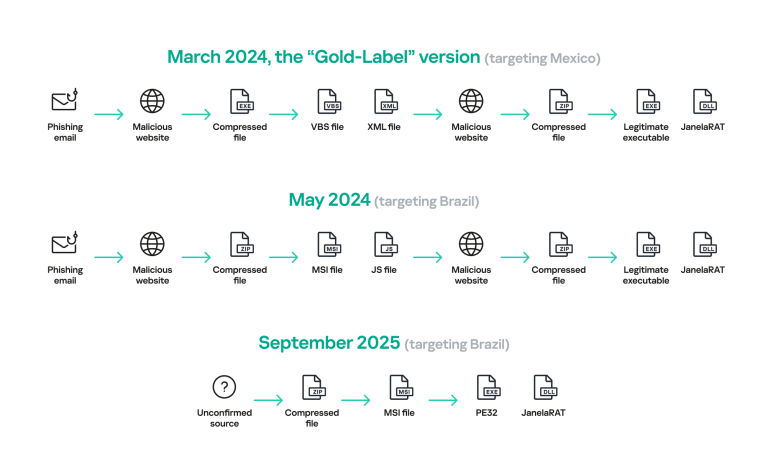
JanelaRAT targets banking users in Brazil and Mexico using window monitoring and fake updates. Learn how this 2026 threat bypasses MFA to hijack sessions.

April 2026 Alert: CPUID downloads for CPU-Z and HWMonitor were poisoned with STX RAT via DLL sideloading. Check your systems for CRYPTBASE.dll now!
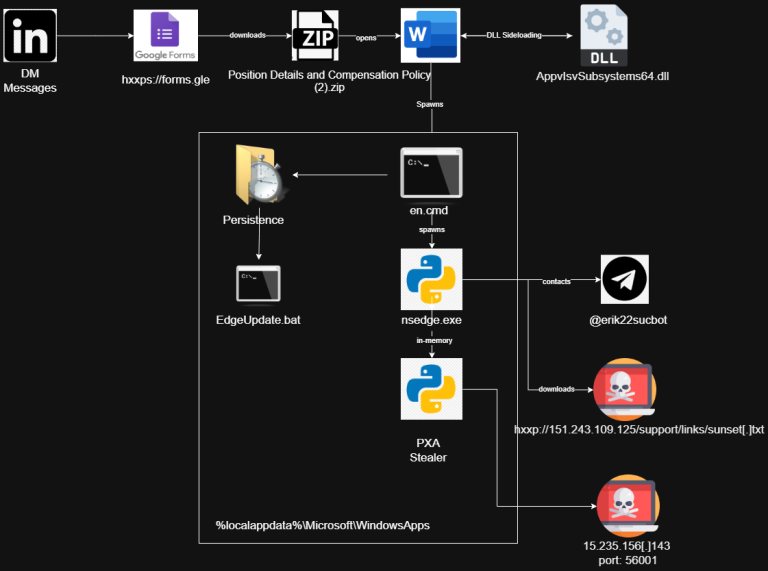
LinkedIn job seekers are being targeted by a sophisticated Vietnam-based group using PXA Stealer. This 100MB malware bypasses MFA and drains crypto wallets.

BlueVoyant exposes Blitz Brigantine's new tactics: using email bombing, Microsoft Teams lures, and covert DNS MX tunneling to deploy AOBackdoor.

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.
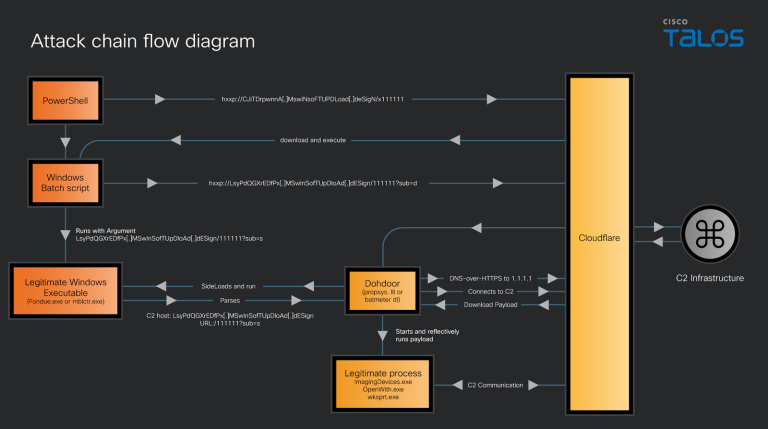
Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.

Microsoft finds hackers using SolarWinds WHD to run hidden QEMU VMs. The attack uses DLL sideloading for full domain compromise. Patch immediately.

Attackers use fake DHL invoices to sideload Phantom Stealer v3.5.0 via a signed Java utility. Malware hides in AddInProcess32.exe. Watch out.

New malware campaign impersonates Malwarebytes installers. Hackers use DLL sideloading to deploy infostealers targeting crypto & MFA. Verify downloads now.

Mustang Panda targets US gov with new LOTUSLITE backdoor. Campaign uses Venezuela lures and DLL sideloading to evade detection.

Attackers exploit legitimate ahost.exe via DLL sideloading to deploy RATs & stealers. Trusted dev utility bypasses security scanners. Watch out.

Kaspersky exposes Evasive Panda’s AitM campaign, hijacking DNS to deliver MgBot through fake updates for SohuVA and Tencent QQ.

Storm-0249 IAB abuses the SentinelOne EDR process via DLL sideloading to evade detection. The group uses LoLBin tools for fileless execution and sells access to ransomware groups like LockBit.