 Do Son
Russian-speaking Lunar Spider group is using the sophisticated Latrodectus V2 loader and a FakeCaptcha lure to gain initial access for ransomware operations.
DLL Sideloading

Patchwork APT has launched a new campaign in South Asia, exploiting DLL sideloading and obfuscation to deliver malware that masquerades as VLC media player for deep espionage.

Huntress details a multi-stage attack that uses DLL sideloading and obfuscated Python to deliver PureRAT, a commercial-grade remote access trojan linked to PXA Stealer.
A new report reveals Subtle Snail, an Iran-nexus group, is using fake LinkedIn jobs to deliver a custom backdoor for espionage against European telecom and defense firms.

A new report reveals a Chinese APT group compromised a Philippine military company with a fileless malware framework called EggStreme, which uses DLL sideloading for stealth.

A new ransomware strain called Cephalus is using compromised RDP, DLL sideloading, and abused security tools to bypass defenses and intimidate victims.
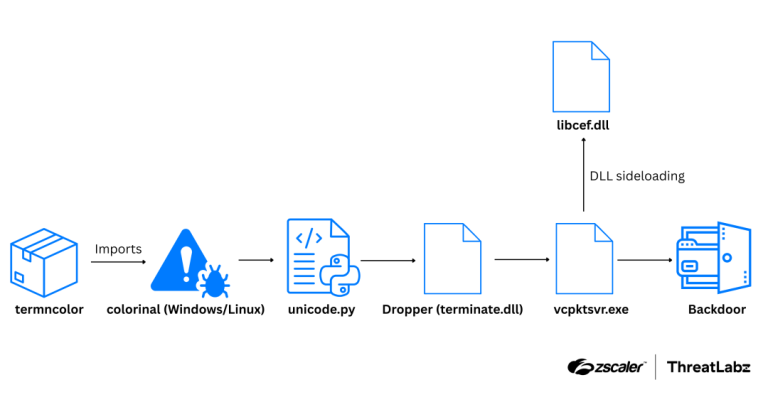
A new report reveals a malicious Python package on PyPI that uses a stealthy dependency and DLL sideloading to deliver a multi-stage malware.

A new Charon ransomware campaign is targeting the Middle East's public sector and aviation with APT-level tactics, including DLL sideloading and anti-EDR.

Mustang Panda, a China-aligned APT, is using the ToneShell backdoor to target government and military sectors with phishing and DLL sideloading, masquerading as a legitimate Chrome component.

SentinelLABS and Beazley expose PXA Stealer, a Python-based infostealer campaign targeting 62 countries with stealthy DLL sideloading, decoy files, and Telegram-based data exfiltration.

Symantec's report reveals LockBit is using evolved tactics, including DLL sideloading and process masquerading with legitimate executables, to evade detection and deploy payloads.

Sophos uncovers a new infection chain for GOLD BLADE's RedLoader malware, combining LNK files, WebDAV, and DLL sideloading to bypass defenses and deploy payloads stealthily.

Zscaler uncovers two China-linked APT campaigns, "GhostChat" and "PhantomPrayers," targeting the Tibetan community with sophisticated spyware via fake apps and DLL sideloading.

Dropping Elephant is targeting Türkiye's defense industry, particularly missile manufacturers, with weaponized conference lures, VLC DLL sideloading, and custom shellcode for intelligence exfiltration.

LAB52 uncovers a sophisticated phishing campaign delivering DeedRAT, a modular backdoor by Chinese APTs, targeting Southeast Asian governments via vulnerable AV software.

Unit 42 uncovers HazyBeacon, a novel backdoor using AWS Lambda URLs for stealthy C2. It's deployed via DLL sideloading, targeting Southeast Asian govts for trade documents.

A new Snake Keylogger campaign exploits an undocumented DLL sideloading technique via jsadebugd.exe to target energy and logistics sectors with fake oil deals.

Netskope uncovers Sainbox RAT (Gh0stRAT variant) and Hidden rootkit delivered via fake software installers to Chinese users, leveraging DLL sideloading and sRDI for stealth.

China-aligned Hive0154 is using phishing lures themed around Tibetan issues to deploy the Pubload backdoor. Campaigns target the Tibetan community, US military

APT36 is targeting Indian defense personnel with sophisticated phishing, using fake NIC documents and multi-layered malware to steal sensitive data and evade analysis.

Seqrite Labs uncovers Operation DRAGONCLONE, a sophisticated APT campaign targeting China Mobile Tietong with VELETRIX and VShell malware.

In-depth analysis of Skitnet malware: Rust, Nim, and DNS abuse. Discover how this sophisticated threat evades detection.