 Do Son
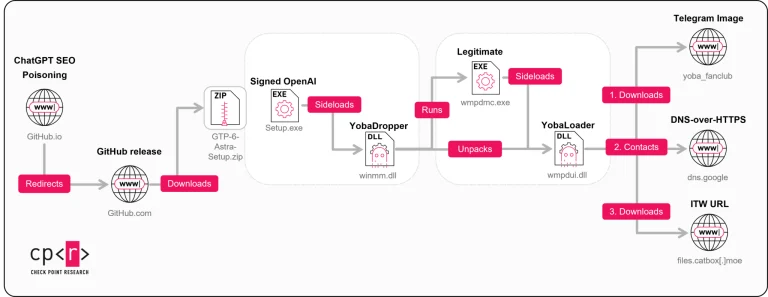
Check Point reveals the Yoba malware campaign. This GitHub Yoba malware campaign uses signed OpenAI and Anthropic binaries to sideload YobaLoader.
DLL Sideloading
BRONZE SANDCASTLE uses Sandboxie DLL sideloading to run a modified Meterpreter backdoor in memory against targets in Asia and Africa.
Siemens Software Center vulnerability CVE-2026-110936 is exploited in the wild by ClickFix attackers via DLL sideloading. Update to 4.0.9.8.
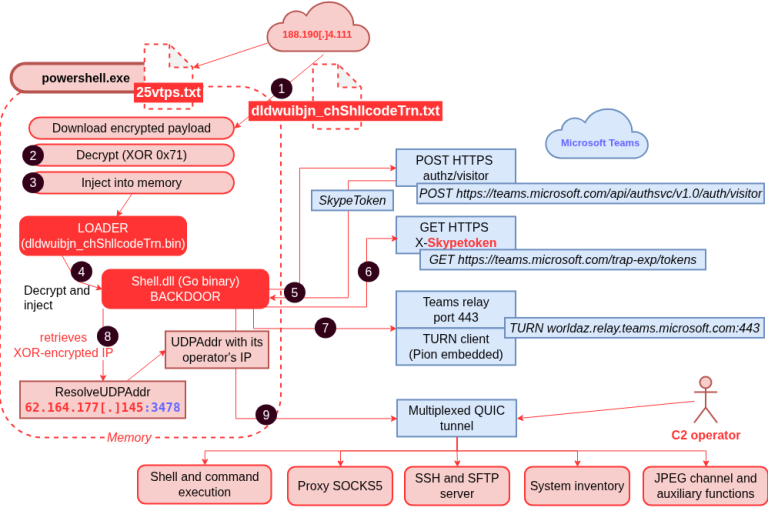
A new DragonForce backdoor hides in Microsoft Teams TURN relays and falls back to MQTT. See how it works and how defenders can spot it.
Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks.
Security researchers uncovered the new PAPERMILL cybercrime cluster. Learn how the PAPERMILL cybercrime cluster uses tax lures to deploy VenomRAT.
SilkParasite APT ran China-nexus cyberespionage across Central Asia, using 7 custom RATs, DLL sideloading, and AI-assisted malware.

Grandoreiro banking trojan resurfaces in a DLL sideloading campaign that abuses Duplicate Files Finder to hit Mexico and Latin America.

Zscaler details the C2Looper backdoor, a Rust backdoor tied to ransomware that uses GitHub for C2 and likely spreads through ClickFix lures.
Trellix details a DCRat campaign using SVG HTML smuggling and process hollowing to deploy DarkCrystal RAT via a Colombian judicial lure.
QuickFox supply chain attack trojanizes a VPN app to deploy the FDMTP implant on Windows users. FortiGuard Labs ties it to Twill Typhoon.

Kaspersky GReAT uncovered OctLurk and SilkLurk, two new memory-resident backdoors targeting Central Asian governments since January 2025.

Cato CTRL details a new SilverFox ValleyRAT campaign in Japan using three BYOVD drivers and DLL sideloading to kill security tools.
Group-IB found an exposed server that revealed JadeProx, a China-nexus cluster running TriBack Loader against targets in Vietnam, Malaysia and Hong Kong.

TELESHIM malware hits Middle East governments and abuses Telegram C2 to hide traffic. Zscaler ThreatLabz found the new backdoor and its tooling.
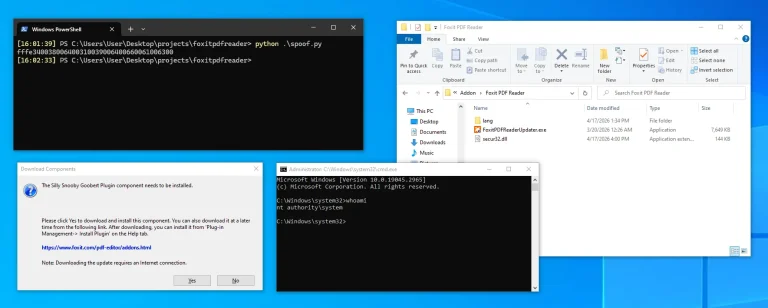
A public proof-of-concept for CVE-2026-57239 turns a Foxit PDF Reader vulnerability into full SYSTEM privileges via local privilege escalation.
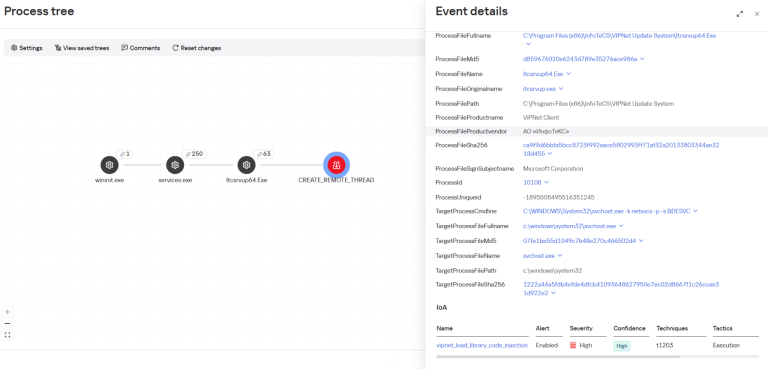
The HelloNet campaign spreads malware through the ViPNet update system, hitting Russian government and energy firms. Kaspersky suspects a China link.
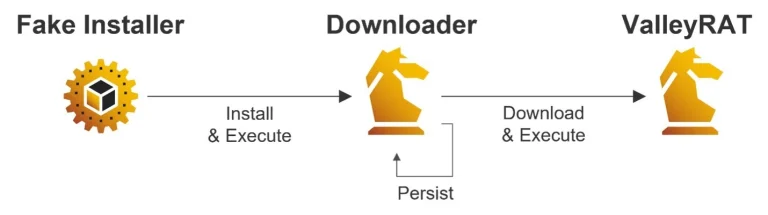
LevelBlue tracks a ValleyRAT malware email campaign using DLL sideloading and fileless execution to hit Japanese and Chinese users.

Mustang Panda targets India's government and hydropower sectors, abusing Zoho WorkDrive for C2. Acronis found new ZOHOMURK and MINIRECON implants.
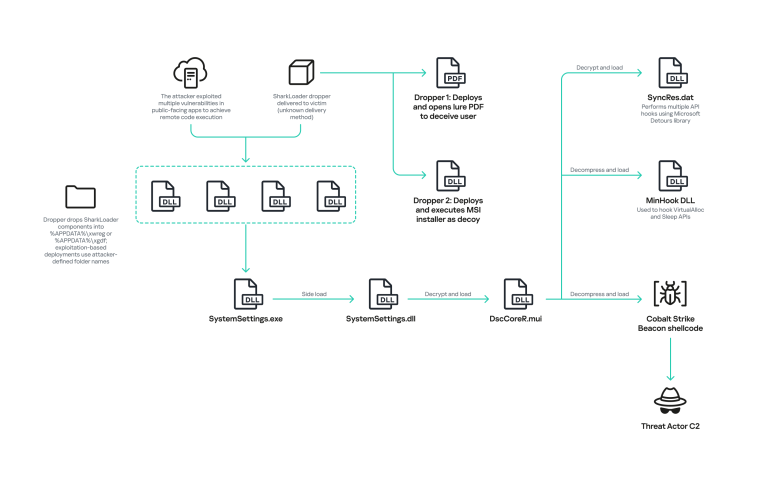
Kaspersky details SharkLoader malware, which deploys Cobalt Strike Beacon in the global StrikeShark campaign via DLL sideloading and exploited apps.
Acronis reveals Khmer Shadow, a new espionage campaign using NIGHTFORGE loader and DLL sideloading to target Cambodian government entities with Havoc Demon.

Discover how the Havoc stager campaign exploits fake invoices. Read the LevelBlue SpiderLabs report detailing this stealthy threat.