
 Do Son
Swan Vector cyber-espionage campaign uses sophisticated malware to target institutions in Japan and Taiwan. Learn how they evade detection and steal data
DLL Sideloading

Sophos researchers detail a complex campaign using Cobalt Strike, DLL sideloading, and clever techniques like expired certificates
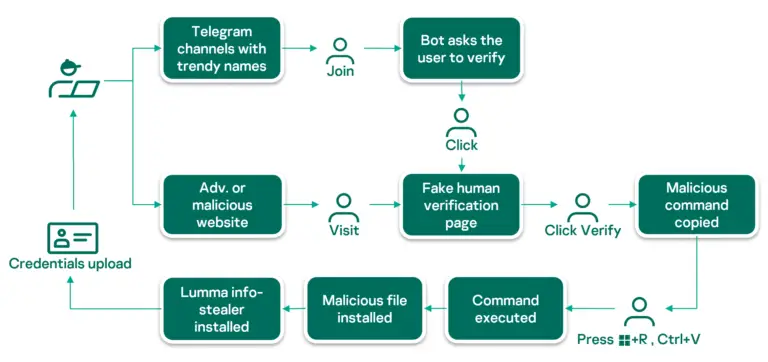
A deep dive into Lumma Stealer's sophisticated techniques: from fake CAPTCHAs to complex infection chains designed to evade detection and steal sensitive data.

The Billbug group targeted Southeast Asian organizations using advanced tools & DLL sideloading. This report details their sophisticated espionage campaign.

Learn about CVE-2025-21420, a critical vulnerability in the Windows Disk Cleanup Tool that could allow SYSTEM privilege escalation.

Beware of cracked software and fake installers. Discover how cybercriminals exploit user trust and spread malicious payloads.

UAC-0184, leverages sophisticated techniques like DLL sideloading and the use of Python-related files to deliver the notorious XWorm RAT
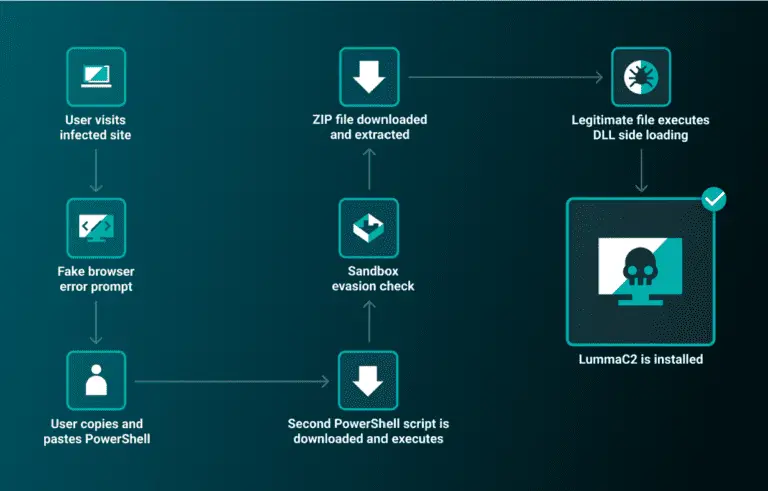
The ReliaQuest Threat Research Team has unveiled a new execution technique used in the ongoing ClearFake campaign

Once WarzoneRAT has infiltrated a system, it employs a sophisticated arsenal of tools to gain a foothold and evade detection

The attackers hid malicious code in packages designed to mimic legitimate ones, using a technique called DLL sideloading to slip past security defenses

DLL Sideloading is used to run a malicious DLL library, while the genuine WinSCP installer serves as a smokescreen for the deceit.

The open-source RAT, Quasar RAT, employs the DLL Sideloading technique to discreetly extract data from infected Windows-based devices