 Do Son
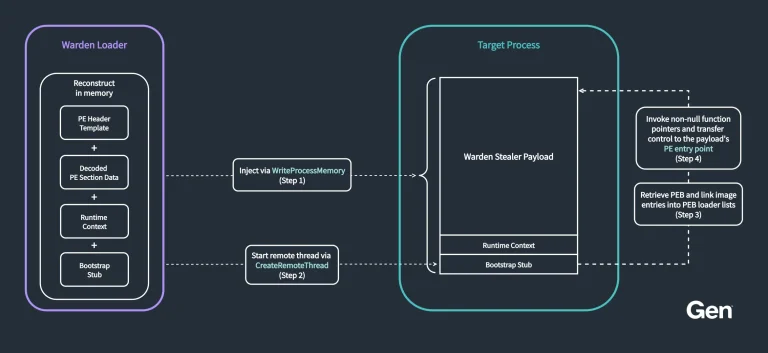
Warden Stealer, a fast-growing Rust infostealer, steals AI agent tokens, browser data, and crypto while bundling its own loader and clipper.
Malware-as-a-Service
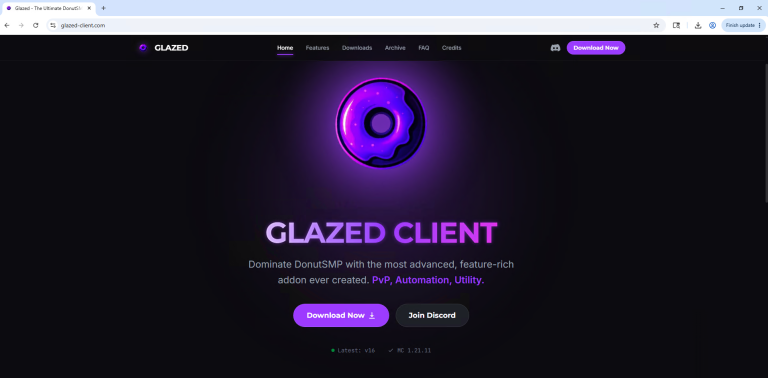
WeedHack malware still targets Minecraft gamers through fake client sites and Minecraft SEO poisoning, McAfee Labs warns.

Insikt Group found four new Golden Chickens malware families, including ChonkyChicken malware, TinyEgg, and a modular plugin variant with ClickFix lures.

Malwarebytes finds fake games spreading Amatera Stealer through RenPy Loader, MSBuild abuse, and EtherHiding C2. See the infection chain and defenses.

Proofpoint details the Cruciferra crypter service that cloaks RATs and infostealers using BYOVD EDR tampering and 90+ custom encryption routines.
Microsoft warns of rising ACR Stealer attacks using ClickFix lures to steal browser credentials and tokens from enterprises. Two chains detailed.
Varonis Threat Labs analyzed Dolphin X stealer, a forum-sold RAT with 300+ credential targets and an AI Profiler that ranks victims for operators.
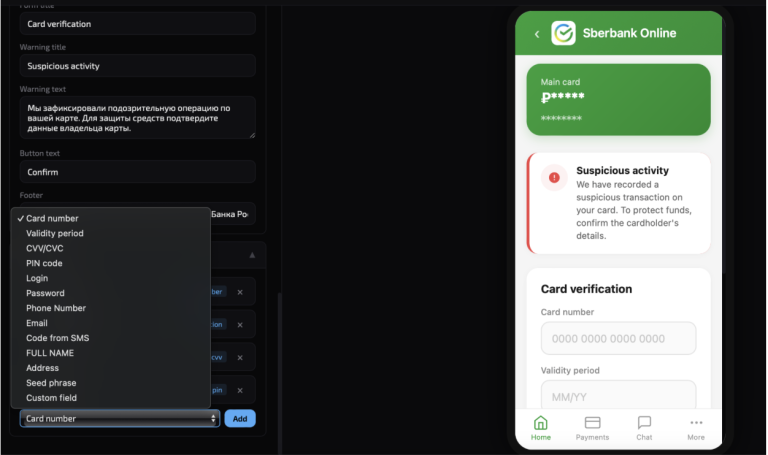
RedWing Android malware is a rental spyware sold as malware-as-a-service on Telegram. It steals banking logins, intercepts 2FA, and hijacks phones.

ErrTraffic malware powers ClickFix attacks on hacked WordPress sites, using EtherHiding on the blockchain to hide its C2 and spread infostealers.
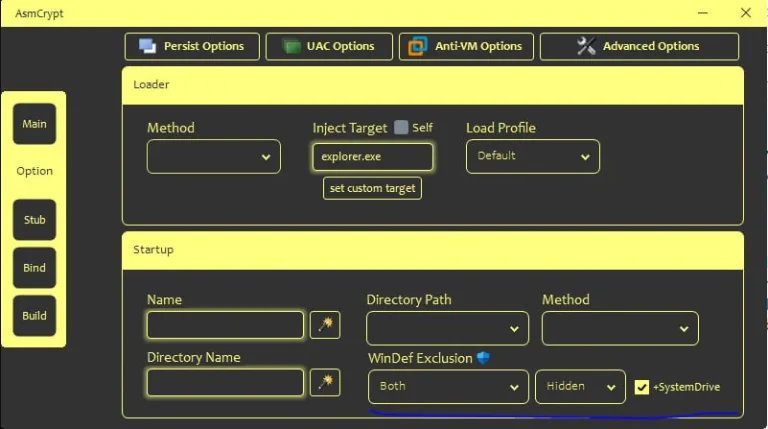
SilabRAT malware, aka SnappyClient, is a $5K/month MaaS RAT flagged as HijackLoader. It uses HVNC and cracks crypto wallets, per Group-IB.

TrendAI exposes Banana RAT, a fileless banking trojan by SHADOW-WATER-063 that uses in-memory execution and fake UI overlays to hijack Pix-QR transfers.
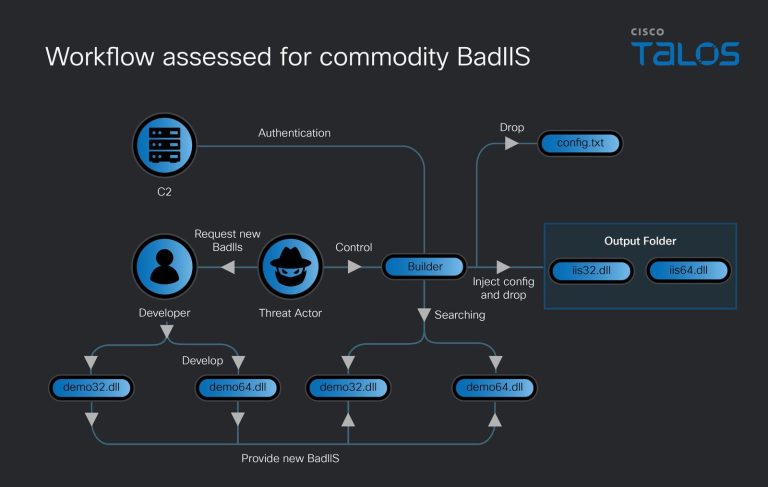
Cisco Talos exposes a commodity BadIIS variant sold as a service by dev "lwxat," featuring automated builders for traffic hijacking and reverse proxying.
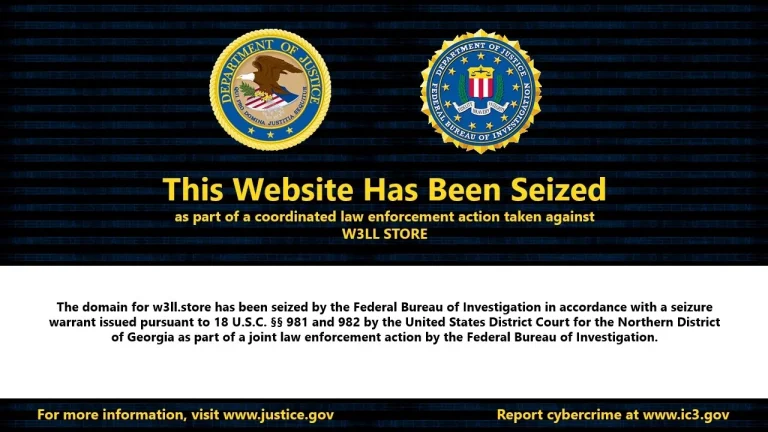
The FBI and Indonesia dismantle W3LL, a $20M phishing kit that bypassed MFA and hijacked live sessions. Learn about the takedown of this MaaS powerhouse.
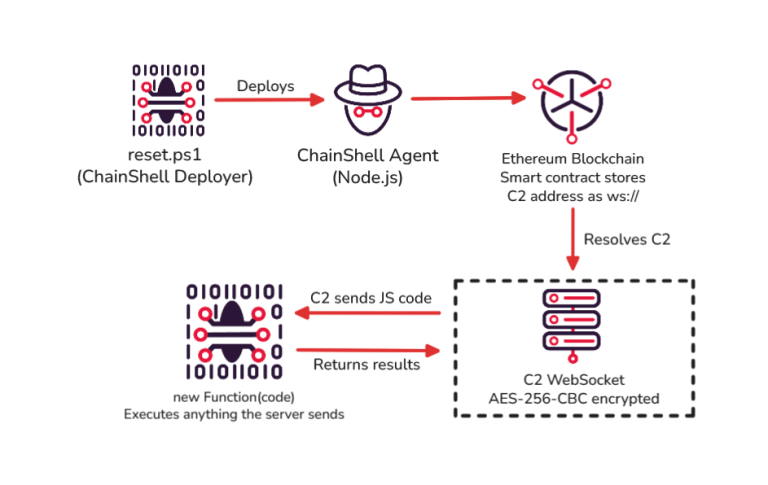
Iranian state actor Muddy Water adopts CastleRAT and ChainShell to hijack browsers and bypass MFA invisibly. A professional-grade shift in APT strategy.
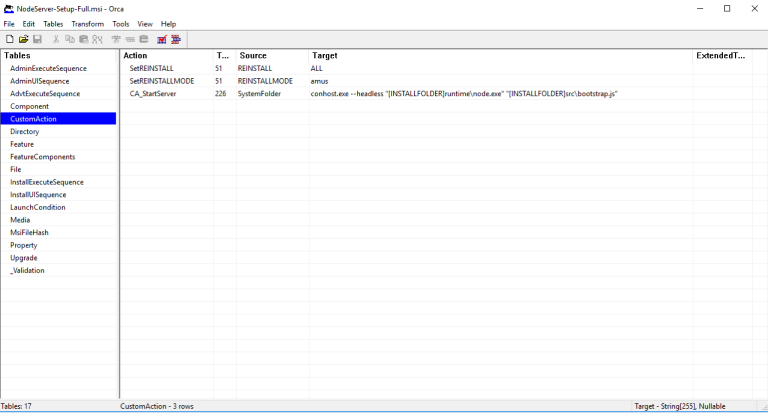
Netskope uncovers a Node.js-based ClickFix campaign using gRPC over Tor for stealthy crypto theft. A leaked file exposed their entire MaaS backend.
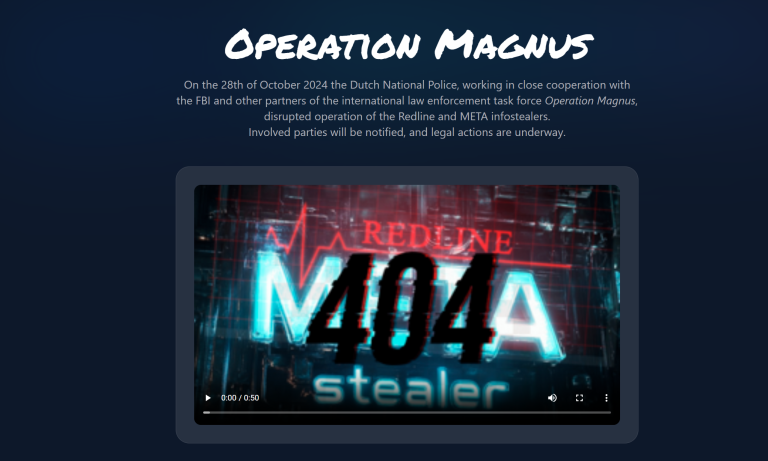
RedLine architect Hambardzum Minasyan is extradited to the U.S. to face 50 years in prison for his role in the global malware empire and Operation Magnus.

LevelBlue uncovers MioLab (Nova), a premium macOS MaaS targeting crypto wallets, Keychains, and Apple Notes. Protect your BIP39 seeds and Mac today.
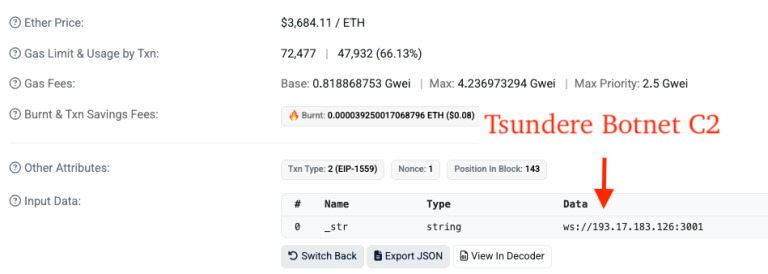
eSentire TRU reveals Iranian group Muddy Water deploying the Russian-linked Tsundere botnet, utilizing Ethereum smart contracts for stealthy C2 communication.

Cyfirma reveals how Telegram has replaced the dark web as the ultimate digital black market, making tools like malware and data theft available to anyone.
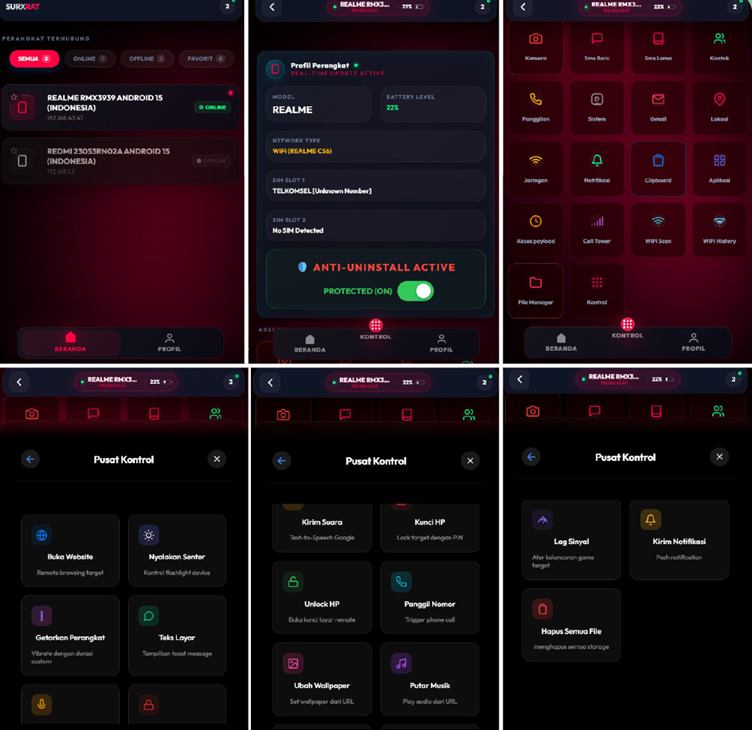
Cyble Research unmasks SURXRAT V5, a professionalized Android RAT experimenting with AI-assisted modules and hybrid monetization via Firebase infrastructure.
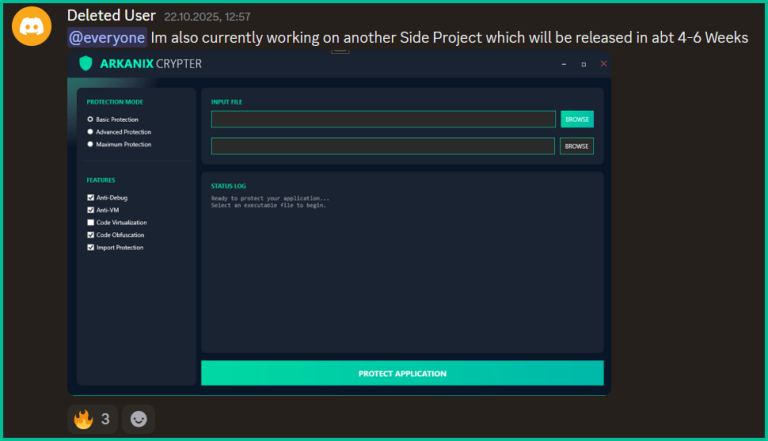
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
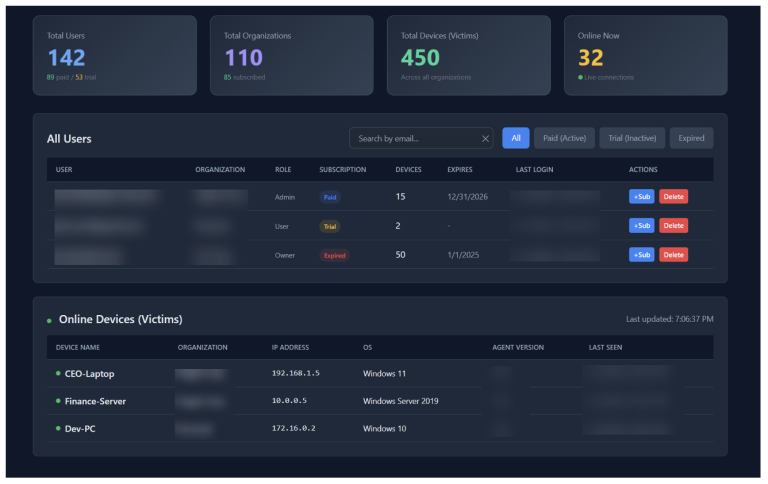
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.