 Do Son
Discover how to permanently resolve the Microsoft Defender false alarm on Windows. Update your system now to stop inaccurate antivirus notifications.
Microsoft Defender
Microsoft Defender for Office 365 incorrectly flags Google search links as malicious, causing false alarms. Microsoft is fixing the classification error.
A Microsoft Defender false alarm wrongly warns that antivirus is turned off after the latest update. Defender still works, and a fix is coming.

Microsoft released a patch for the Microsoft Defender scan failure issue. Learn how a flawed update stopped threat services and how to fix this severe error.

Microsoft Defender incorrectly isolates VLC plugin caches on Windows 11. Discover how to fix this annoying Microsoft Defender VLC bug and restore playback.
Microsoft warns of rising ACR Stealer attacks using ClickFix lures to steal browser credentials and tokens from enterprises. Two chains detailed.

A new Microsoft Defender zero day exploit leaks online, exposing a severe race condition vulnerability affecting fully patched Windows installations.

A stealthy GPU cryptojacking campaign leverages AI search poisoning and process hollowing injection to hijack high-end rigs. Read the Microsoft report.
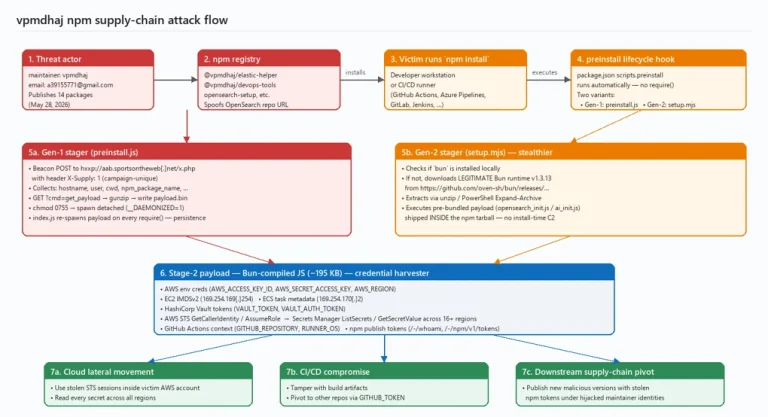
A critical npm supply chain attack exploits lookalike packages to distribute credential harvesting malware. Learn how to protect your cloud assets.
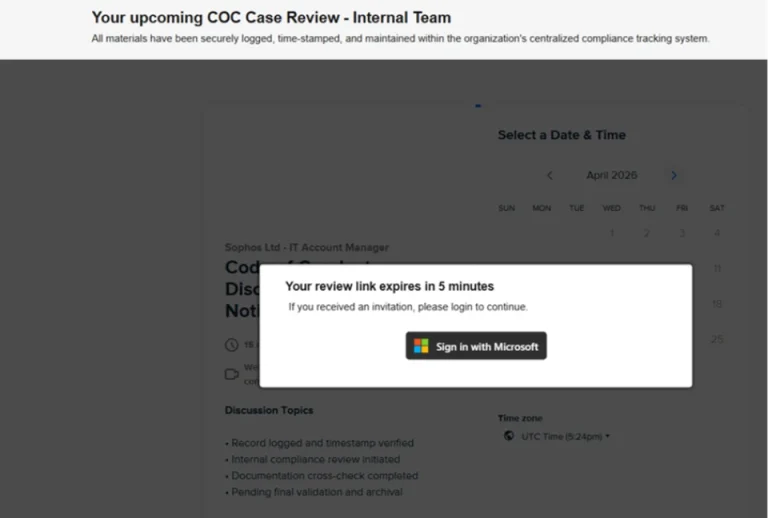
Microsoft warns of a massive AiTM phishing campaign targeting 13,000+ orgs. Using fake disciplinary lures, attackers bypass MFA to hijack active sessions.

Microsoft Defender erroneously flagged DigiCert root certificates as "Cerdigicert" malware. Discover the fix and how to restore your system's trusted root store.

CISA adds BlueHammer (CVE-2026-33825) to the KEV catalog. This Microsoft Defender LPE exploit uses TOCTOU to hijack SAM databases. Patch by May 6, 2026.

Microsoft warns of a Teams campaign using fake IT support to hijack workstations via Quick Assist, move laterally with WinRM, and steal data using Rclone.

Microsoft Defender faces a critical "Red Sun" vulnerability. Learn how this zero-day exploit bypasses security to grant hackers full administrative control.

Microsoft warns of a 50M-user flaw in EngageSDK affecting crypto wallets. An intent redirection bug could leak private data. Update to v5.2.1 now!
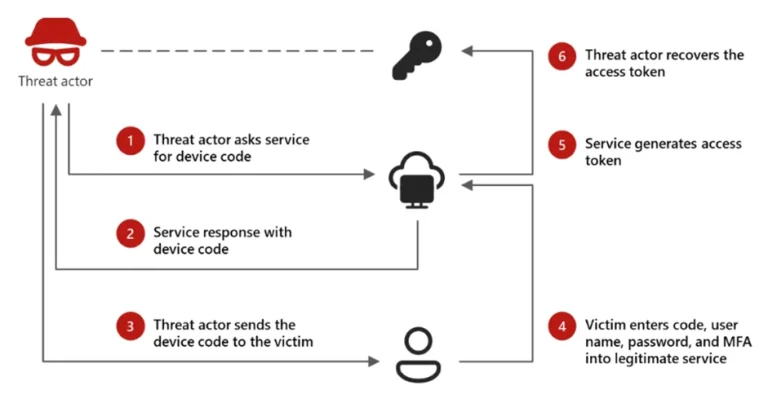
Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!
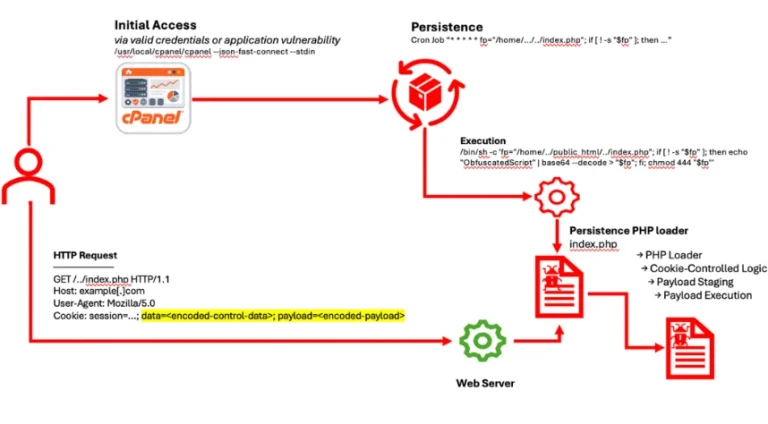
Microsoft Defender unmasks a stealthy PHP web shell hiding C2 logic in HTTP cookies. Learn how "cookie-gating" bypasses logs to maintain persistent RCE.

Microsoft Defender warns of a 2026 WhatsApp malware campaign using VBS and renamed system tools to hijack PCs via AWS and Tencent Cloud. Stay alert!
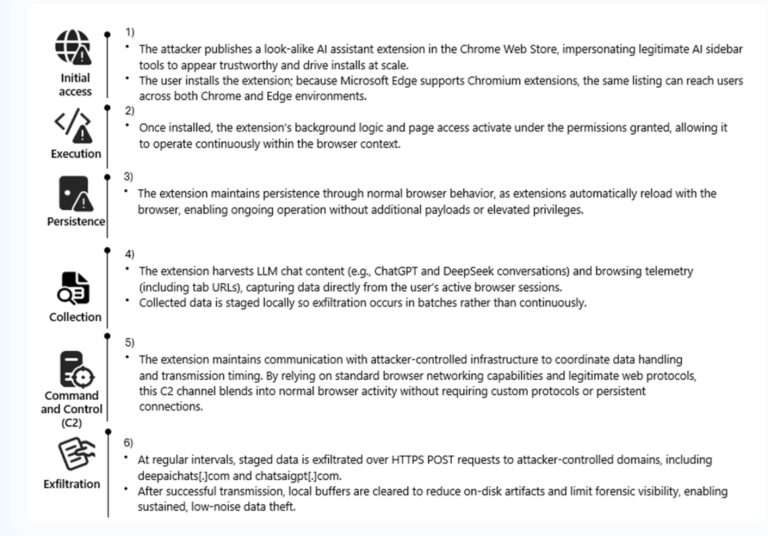
Microsoft Defender uncovers a massive campaign of malicious Chromium extensions impersonating AI tools to steal data from 900,000 users. Audit browsers now.

Microsoft Defender exposes a new phishing campaign using EV certificates and fake Teams invites to silently deploy RMM backdoors on corporate networks.
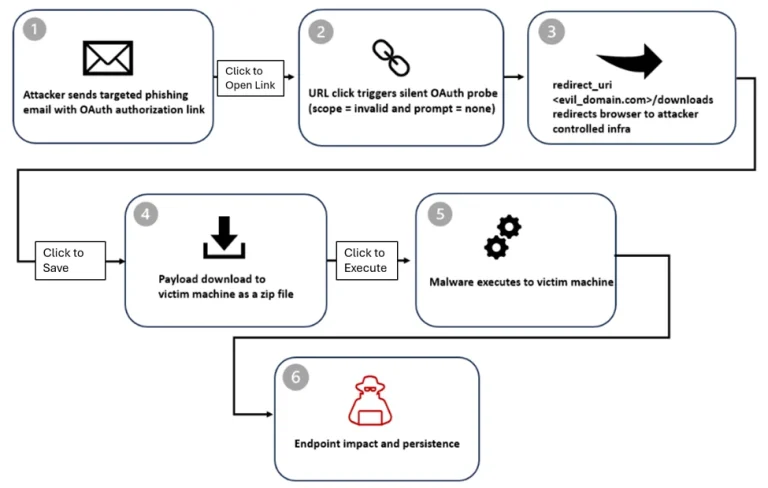
Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.
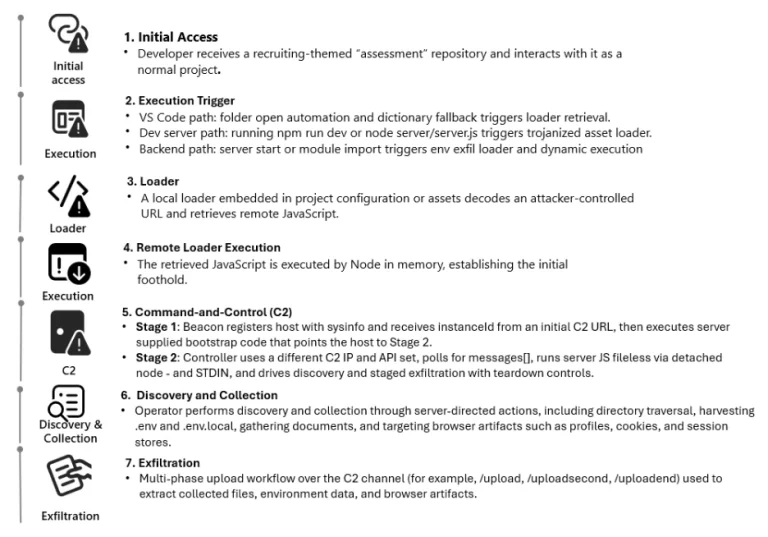
Microsoft warns of a new campaign targeting engineers via fake Next.js technical assessments. Malware hides in VS Code tasks and npm scripts to steal secrets.