 Do Son
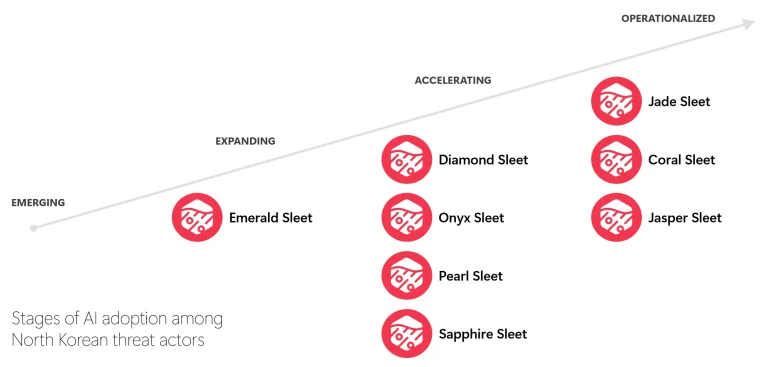
Microsoft reveals how North Korean threat actors use tools like ARTEX. See how AI-enabled North Korean threat actors speed up cyber operations.
Microsoft Threat Intelligence
Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks.
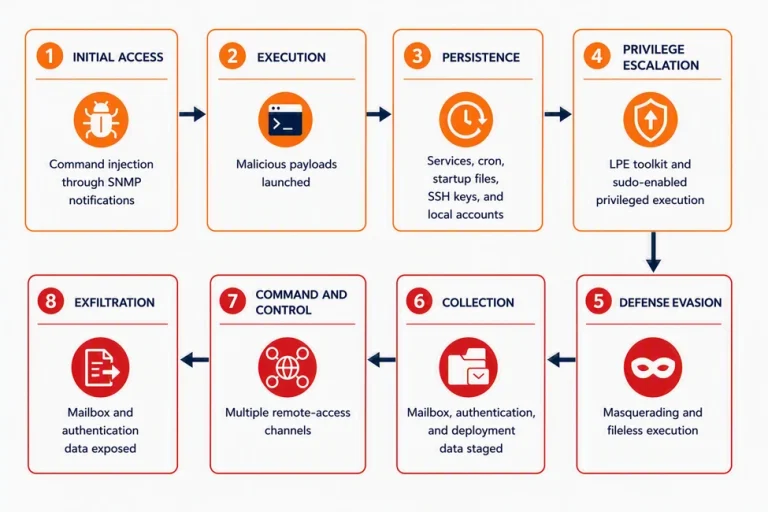
Zimbra CVE-2026-73570 lets one crafted email run code. Microsoft details the Zimbra command injection attacks: web shells, root access, and key theft.
Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.
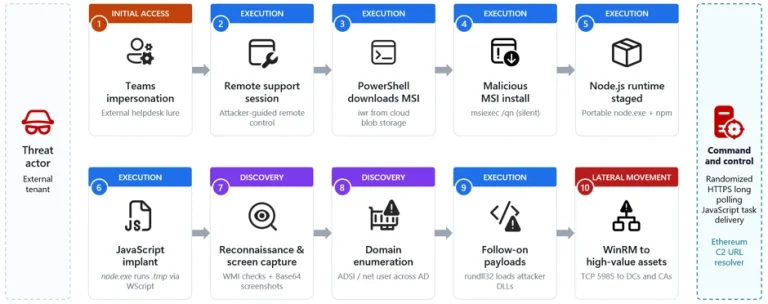
Microsoft Teams IT support impersonation lets attackers plant a Node.js implant and pivot to domain controllers over WinRM. See how to defend.

Microsoft exposes the GigaWiper backdoor, a destructive tool that bundles disk wiping malware, fake ransomware, and remote control in one implant.

Microsoft found a fake Perplexity AI extension that hijacks browser search and logs keystrokes. Google pulled the malicious Chrome extension.
Microsoft discovered a new Windows crypto clipper malware. This Tor routed cryptocurrency stealer uses USB drives to spread and steal wallet addresses.

Microsoft uncovers a massive npm dependency confusion attack targeting enterprise infrastructure. Learn how these malicious packages discovered run code.

Microsoft exposes Storm-2949, a cloud-native threat group abusing Azure management features and SSPR to hijack Key Vaults, App Services, and SQL databases.

Microsoft Threat Intelligence exposes a massive overhaul of the Kazuar backdoor. Secret Blizzard weaponizes a modular, multi-tiered P2P botnet.
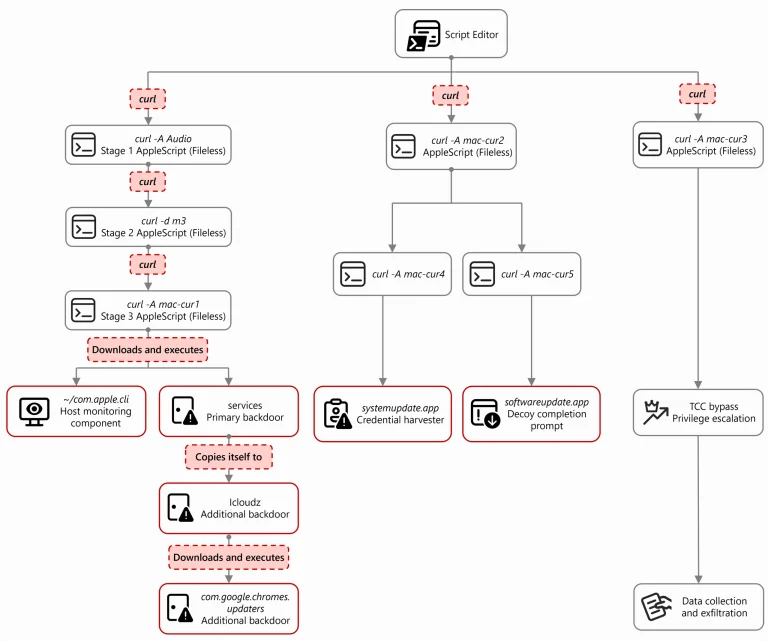
Microsoft uncovers Sapphire Sleet's macOS campaign. Using fake recruiters and AppleScript, they bypass TCC to steal crypto wallets, Telegram, and SSH keys.
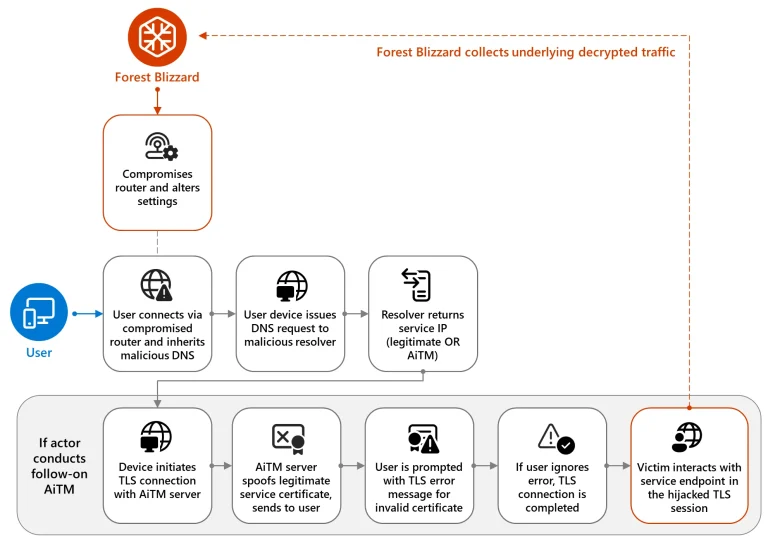
Microsoft exposes Forest Blizzard’s hijacking of 5,000+ SOHO routers for DNS spying and AiTM attacks on Microsoft 365 and governments. Patch your router now!
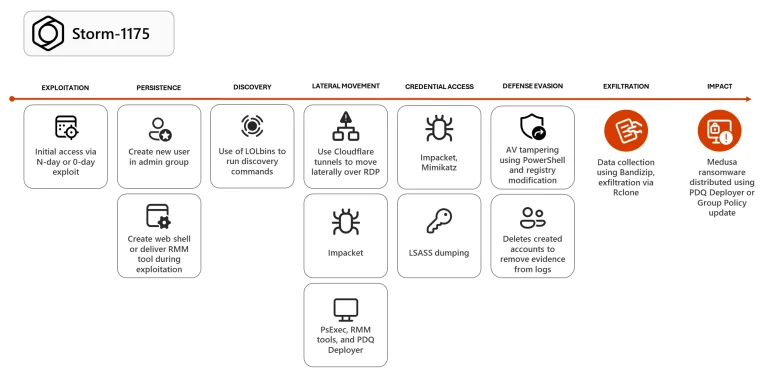
Microsoft exposes Storm-1175: a high-speed threat actor deploying Medusa ransomware in under 24 hours via zero-day exploits. Learn how to stop the blitz.
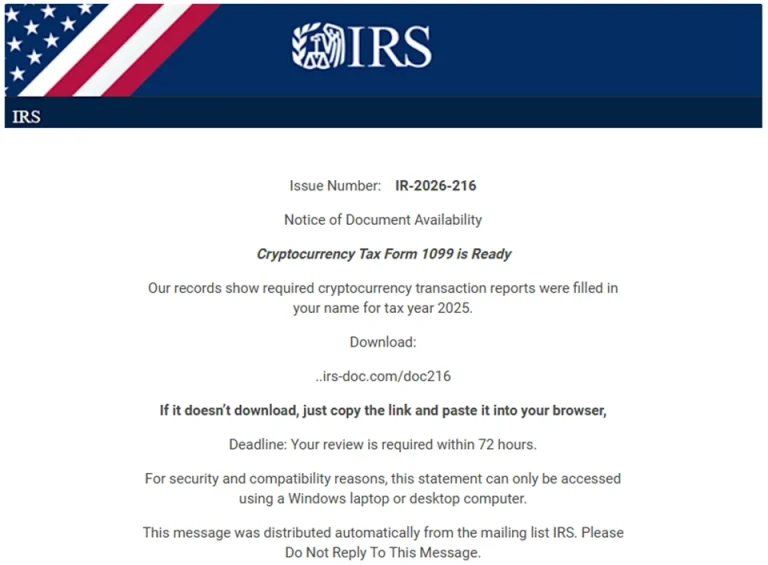
Microsoft warns of a surge in tax-themed phishing using PhaaS and ScreenConnect RATs to bypass MFA and hijack systems. Protect your W-2 data this season.
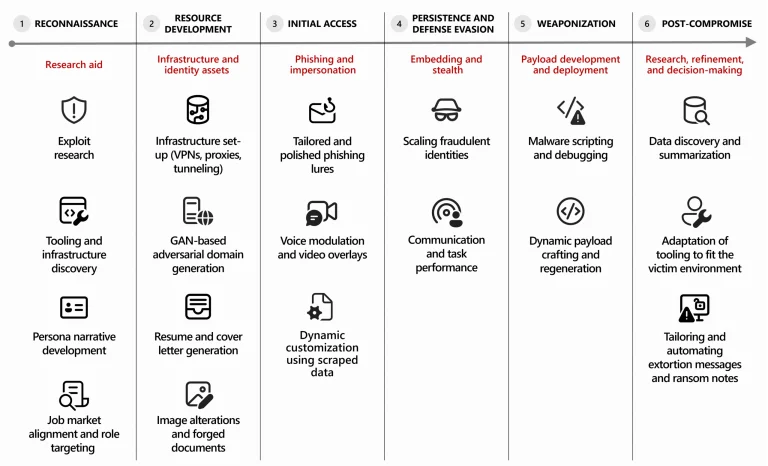
Microsoft Threat Intelligence reveals how cybercriminals and North Korean APTs are weaponizing generative AI to scale attacks and poison AI assistants.

Microsoft warns of Storm-2657, a financial crime group exploiting MFA flaws to hijack university employee accounts, rerouting salary payments through third-party HR platforms like Workday.

Microsoft Threat Intelligence details how APTs abuse Teams and Entra ID integration for recon, vishing, and C2. Attackers use RMM tools and spoofed accounts to breach enterprise environments.

A new Microsoft report reveals that the Storm-0501 threat actor is pivoting to cloud-native ransomware, using cloud tools to exfiltrate and destroy data without malware.

Microsoft has exposed PipeMagic, a new backdoor disguised as a ChatGPT app. It was used with a zero-day exploit to gain SYSTEM privileges and deploy ransomware.

Microsoft exposes North Korea’s Jasper Sleet (Storm-0287) using AI-enhanced deepfakes and fake personas to secure remote IT jobs at 300+ US firms, funding the DPRK regime and stealing data.

Microsoft uncovers CVE-2025-31191, a macOS sandbox escape exploiting security-scoped bookmarks. Apple patched it in March 2025.