
 Do Son
A Microsoft Teams vishing campaign tracked as STAC4749 hit dozens of North American firms and deployed Chaos ransomware in under 17 hours.
ransomware

A new GoGRPC backdoor spreads through Microsoft Teams vishing and Quick Assist. Zscaler links the campaign to a likely ransomware access broker.
Spirals ransomware hit a South Asian IT firm in a double extortion attack, going from IIS breach to network-wide encryption in under 24 hours.
Sysdig documented JADEPUFFER, the first agentic ransomware run end-to-end by an AI agent. It breached Langflow via CVE-2025-3248 and extorted a database.
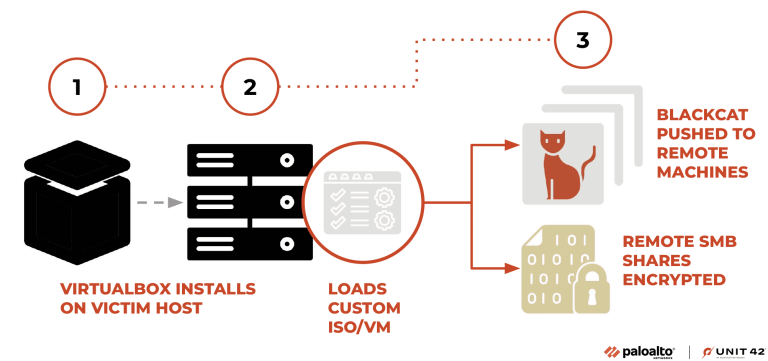
A Florida ransomware negotiator got 70 months for feeding clients' secrets to BlackCat ransomware actors. The DOJ seized over $10 million in proceeds.
Discover how AI generated malware from DeepSeek turns hallucinated ideas into real browser native ransomware using the File System Access API.

Kaspersky details The Gentlemen ransomware, a fast-growing RaaS group with new Go and C lockers, EDR killers, and worldwide victims. Here's how it works.
Following a Scattered Spider arrest, Peter Stokes faces extradition to the US for his alleged role in a $100M cyber extortion and hacking scheme.
An iPhone 18 Pro leak from the Tata Electronics breach exposes supplier lists, component details, and device photos on the dark web.
A Tata Electronics data breach exposed 630GB of files. Hackers claim Apple and Tesla design documents are in the stolen 200,000-file haul.

DragonForce ransomware deployed Backdoor.Turn, a Microsoft Teams backdoor that hides C2 in Teams TURN relays. Symantec details the novel technique.
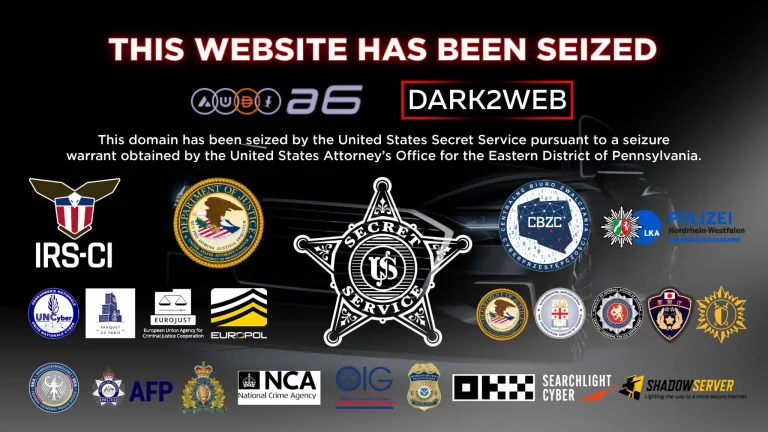
Authorities dismantled a major crypto laundering service used by ransomware gangs to wash millions. Read about the global AudiA6 dark web takedown.

CISA expands its active exploit catalog with critical gateway flaws in BerriAI LiteLLM and Check Point configurations. Patch immediately.

Europol completely dismantles 'First VPN,' seizing 33 servers and uncovering an underground database used by thousands of global ransomware operators.
Two US cybersecurity professionals get 4 years in prison for acting as ALPHV BlackCat ransomware affiliates, extorting victims and leaking patient data.
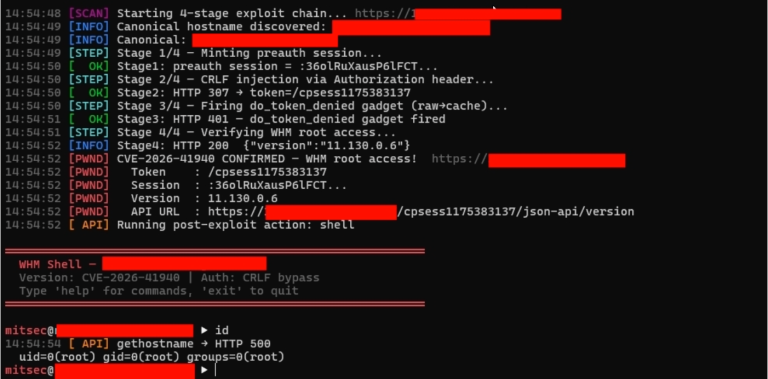
CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!
Check Point Research reveals VECT 2.0 ransomware is a broken wiper. A critical flaw makes file recovery impossible for files over 128KB. Read the analysis.
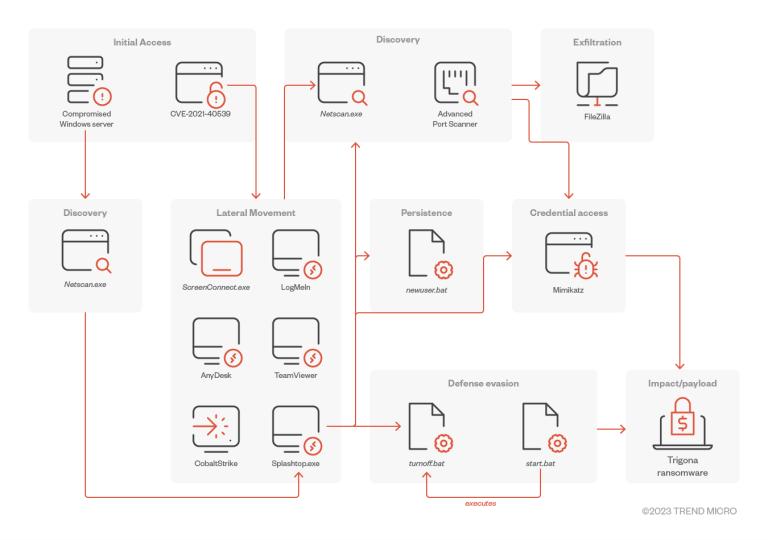
Trigona ransomware swaps Rclone for a custom tool that rotates connections to evade monitoring. Learn how uploader_client.exe powers their data theft.
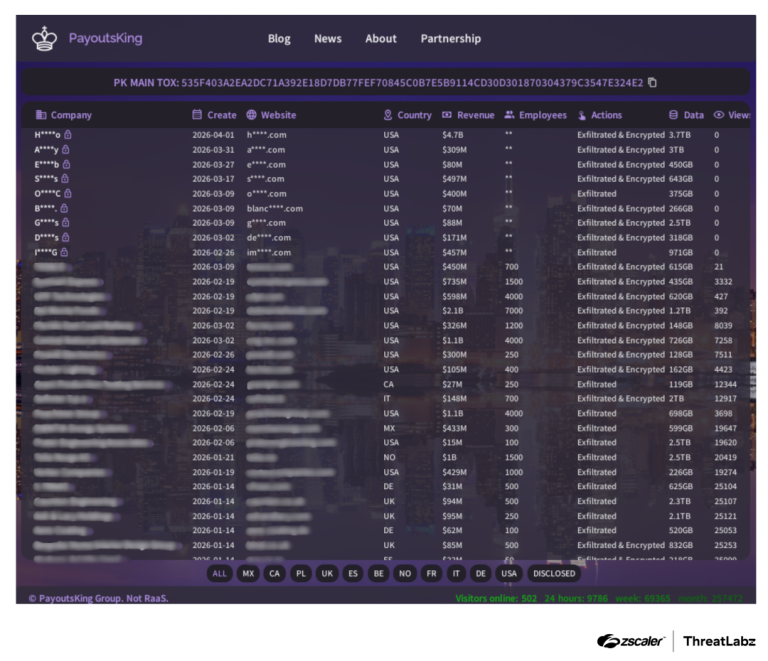
Payouts King, the successor to BlackBasta, uses vishing and direct syscalls to bypass EDR and strike global targets. Learn how to defend your enterprise.

Former ransomware negotiator Angelo Martino pleaded guilty to working with BlackCat to extort his own clients. $10M in luxury assets seized. Facing 20 years.
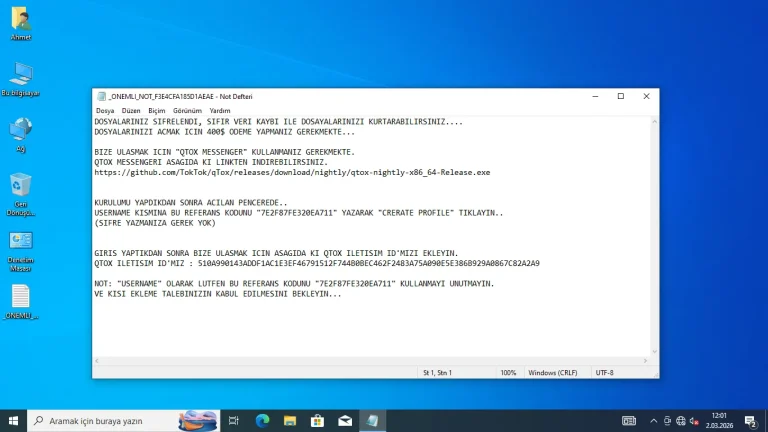
Acronis uncovers JanaWare, a persistent ransomware targeting Turkey since 2020. Discover how geofencing and polymorphism keep this threat in the shadows.

Hackers target Rockstar Games via Snowflake. While Rockstar calls the data "non-substantial," could internal budgets and future launch dates be at risk?