 Do Son
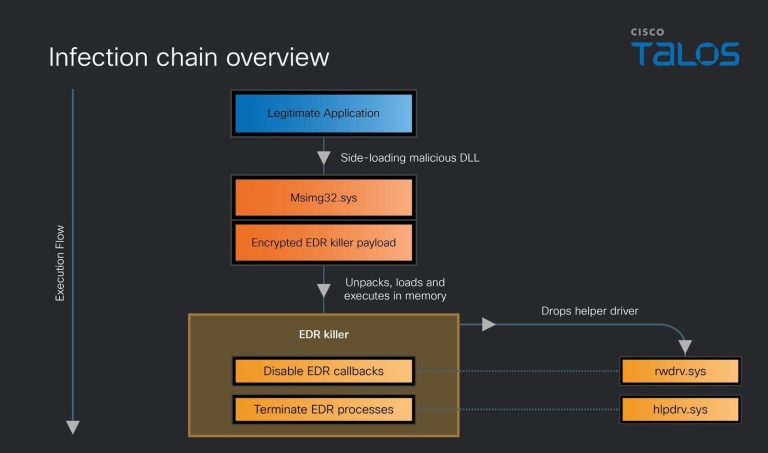
Cisco Talos unmasks a Qilin ransomware payload that terminates 300+ EDR drivers and manipulates the Windows kernel. See how this "EDR Killer" stays invisible.
ransomware
Russian national Aleksei Volkov was sentenced to 81 months in prison and ordered to pay $9.1M for his role as an access broker in major U.S. ransomware attacks.

Malefactors claim a massive breach of OVHcloud, allegedly stealing 1.6M customer dossiers and 5.9M domain records. Discover the risks to Europe’s cloud giant.

Trend Micro reveals Warlock ransomware is using kernel-level BYOVD attacks and abused IT tools to bypass security and hijack Active Directory.

Amazon threat intel reveals Interlock ransomware is actively exploiting a critical 10.0 CVSS Cisco zero-day (CVE-2026-20131) to hijack firewall networks.

A joint advisory warns of INC Ransom's devastating pivot to the Pacific. Discover how this RaaS group uses double extortion to target healthcare sectors.

Cyfirma reveals how Telegram has replaced the dark web as the ultimate digital black market, making tools like malware and data theft available to anyone.

The DFIR Report reveals how a persistent attacker exploited CVE-2023-46604 twice in 18 days to deploy LockBit ransomware. Patch your ActiveMQ servers now!
Black Basta ransomware now embeds a vulnerable NsecSoft driver (BYOVD) to silently kill antivirus processes like Sophos & CrowdStrike.

Silent Push reveals a massive SystemBC botnet with 10,000+ infected IPs. The SOCKS5 proxy malware hit government domains and uses bulletproof hosting.

Critical ASUSTOR ADM flaw CVE-2026-24936 (CVSS 9.5) allows remote file overwrite. Unauthenticated attackers can seize NAS control. Update to v5.1.2 now.

Interlock ransomware exploits a zero-day in gaming anti-cheat drivers to blind defenses. "Hotta Killer" tool targets education sector. Read the analysis.

TA584 triples activity with new "Tsundere Bot" malware. Attackers use invisible Registry keys to hide persistence. Read the Proofpoint analysis.

Attackers abuse GitHub, Dropbox, and the "Defendnot" research tool to disable Windows Defender and deploy Amnesia RAT & ransomware in Russia.

Seqrite exposes "Operation Covert Access": A Rust RAT targeting Argentina's legal system via fake court rulings. Includes anti-analysis & encryption tools.
S2W reveals DragonForce is a "cartel" hacking rivals like BlackLock. Built on LockBit 3.0 code, they offer "Ransombay" services. A decryptor was found.

Group-IB uncovers DeadLock ransomware using Polygon smart contracts for resilient C2. This "EtherHiding" tactic signals a new era of blockchain abuse.

New deVixor Android malware combines banking fraud with ransomware. Targeting Iranian users, it steals credentials and locks devices. Avoid APKs.

LockBit 5.0 emerges with new "premium" criminal services. AhnLab analysis reveals how the top RaaS gang targets IT firms and churches alike.

New CrazyHunter ransomware targets healthcare with BYOVD tactics and rapid encryption. Trellix reveals how this "greedy" threat cripples hospitals.

Two US cybersecurity pros, Ryan Goldberg and Kevin Martin, plead guilty to moonlighting as ALPHV/BlackCat affiliates, extorting $1.2M from victims.

Yarix exposes the new Qilin-LockBit-DragonForce cartel. Is it a powerful merger or a desperate PR stunt for a "dead" LockBit? Find out.