
 Do Son
A new Go-based ransomware, Obscura, is abusing domain controllers by placing its executable in the NETLOGON folder, ensuring it gets replicated across the network.
ransomware

A new ransomware group, DireWolf, has rapidly emerged to target global businesses with a powerful new strain of malware and a double extortion model.

A new report reveals a network of Ukrainian and offshore hosting providers are fueling large-scale brute-force and password-spraying campaigns to enable global ransomware attacks.

A loophole in the VS Code Marketplace allows attackers to reuse names of removed extensions to spread malware, a flaw that creates a new supply chain attack vector.

A new report from AhnLab reveals the Interlock ransomware group is actively attacking businesses and critical infrastructure in North America and Europe with a sophisticated encryption model.
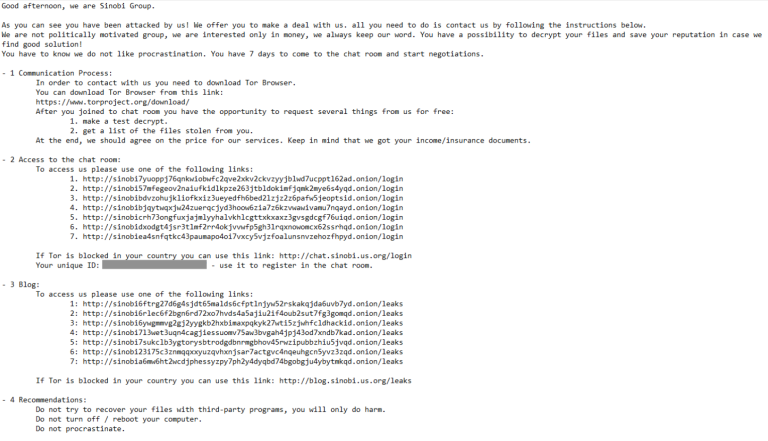
A new report links Sinobi Group ransomware to Lynx, a potential rebrand. The group is using strong encryption and targeting compromised SonicWall VPN credentials to gain access.
A new Anthropic report reveals how criminals are weaponizing AI systems to automate attacks, create AI-generated ransomware, and secure fraudulent employment.

A new Microsoft report reveals that the Storm-0501 threat actor is pivoting to cloud-native ransomware, using cloud tools to exfiltrate and destroy data without malware.

A new report from ESET reveals PromptLock, a ransomware strain that uses AI to dynamically generate malicious scripts, making it uniquely difficult for security software to detect.

A new report reveals a persistent phishing campaign targeting ScreenConnect super admins. The stolen credentials are being sold to ransomware affiliates for future attacks.

A new report reveals the Hook Android trojan has evolved into a hybrid threat with ransomware-style overlays, lockscreen bypasses, and stealthy screen-streaming.

A new ransomware strain called Cephalus is using compromised RDP, DLL sideloading, and abused security tools to bypass defenses and intimidate victims.

A new report from AhnLab reveals the Underground ransomware gang is back with a global campaign that uses sophisticated multi-layered encryption and customized malware.
A new report reveals how attackers are using invisible text and "prompt overdose" to trick AI summarizers into delivering ransomware instructions to users.

A new RaaS operation called BQTLock is targeting victims with sophisticated malware, aggressive ransom demands, and a tiered subscription model for affiliates.

A new report from Trend Micro details how the Warlock ransomware group is exploiting a vulnerability in unpatched Microsoft SharePoint servers to attack organizations.

Microsoft has exposed PipeMagic, a new backdoor disguised as a ChatGPT app. It was used with a zero-day exploit to gain SYSTEM privileges and deploy ransomware.

A new analysis details how the RansomEXX gang exploited a use-after-free zero-day (CVE-2025-29824) in the Windows Common Log File System to gain SYSTEM privileges.

Pakistan's critical sectors have been hit by the Blue Locker ransomware. This sophisticated campaign is linked to the Proton malware family and exploits a recent holiday.

Trend Micro research exposes Crypto24, a coordinated ransomware operation that uses legitimate tools, custom malware, and advanced evasion tactics to breach and extort victims.

A new Charon ransomware campaign is targeting the Middle East's public sector and aviation with APT-level tactics, including DLL sideloading and anti-EDR.

IBM X-Force exposes CastleBot, a new MaaS framework that deploys infostealers and backdoors like NetSupport and WarmCookie via trojanized installers and phishing.