
 Do Son
A coordinated campaign by GreedyBear used 150+ malicious Firefox extensions and fake sites to steal over $1M in crypto. They are now using a new technique called Extension Hollowing to evade detection.
ransomware

Silent Push exposes SocGholish as a MaaS platform for Initial Access Brokers. The malware, disguised as fake updates, fuels top-tier Russian ransomware groups like Evil Corp.

Google confirms a June Salesforce breach by UNC6040 (ShinyHunters). The attack used social engineering to steal credentials, a tactic also used against Chanel and Allianz.

Kaspersky exposes a new AV killer leveraging the legitimate ThrottleStop.sys driver to disable antivirus software and deploy MedusaLocker ransomware in a BYOVD attack.

Unit 42 reveals Project AK47, a toolkit used by Storm-2603 to exploit SharePoint. It includes a custom AK47C2 framework and links to both LockBit and Warlock ransomware.

The DFIR Report details a destructive attack: Bumblebee malware, delivered via SEO poisoning in Bing search results, led to a full Akira ransomware deployment in under 44 hours.

A critical server-side template injection flaw (CVE-2024-23692) in Rejetto HFS 2.x is actively exploited to deploy ransomware and trojans at scale. Update or retire the service immediately.

Huntress and other firms warn of a likely zero-day vulnerability in SonicWall VPNs. Attackers are bypassing MFA and deploying Akira ransomware within hours of initial access.
ShadowSyndicate’s Global Ransomware Empire Blurs Lines Between Cybercrime and Geopolitical Espionage

ShadowSyndicate’s Global Ransomware Empire Blurs Lines Between Cybercrime and Geopolitical Espionage
A new report exposes ShadowSyndicate, a sophisticated cybercrime group tied to top-tier RaaS affiliates, bulletproof hosting, and suspected geopolitical influence operations, blurring lines between cybercrime and espionage.

Check Point Research uncovers Storm-2603, a China-linked APT using a custom AK47C2 framework and BYOVD tactics to deploy multiple ransomware strains simultaneously.

eSentire exposes Interlock, a new ransomware group using multi-stage payloads and the ClickFix social engineering technique to deploy ransomware and backdoors via compromised websites.

Cisco Talos' Q2 2025 report reveals phishing is the top access method. Ransomware, including Qilin, dominated, with a surprising trend of attackers abusing PowerShell 1.0 to evade security.

Symantec's report reveals LockBit is using evolved tactics, including DLL sideloading and process masquerading with legitimate executables, to evade detection and deploy payloads.

Gen Digital has released a free decryptor for FunkSec ransomware, allowing victims to recover files. The group appears dormant, with no new victims since March 2025.

A joint advisory from US, UK, Canada, and Australia warns of Scattered Spider's evolving tactics, now using DragonForce ransomware, spearphishing, SIM swapping, and MFA fatigue to compromise systems.

Trend Micro reports Gunra ransomware has expanded to Linux, employing 100 parallel encryption threads, partial encryption, and stealthy keystore methods to target global enterprises.

The UK government is drafting new legislation to criminalize ransomware payments by public sector bodies (NHS, schools, councils) to deter attacks and cut off funding to cybercriminals.

The suspected administrator of xss.is, a notorious Russian-speaking cybercrime forum, has been arrested in Ukraine after a joint operation by French police and Europol.

CISA, FBI, and HHS issue a joint advisory on Interlock ransomware, active since Sep 2024, targeting businesses and critical infrastructure with double extortion tactics.
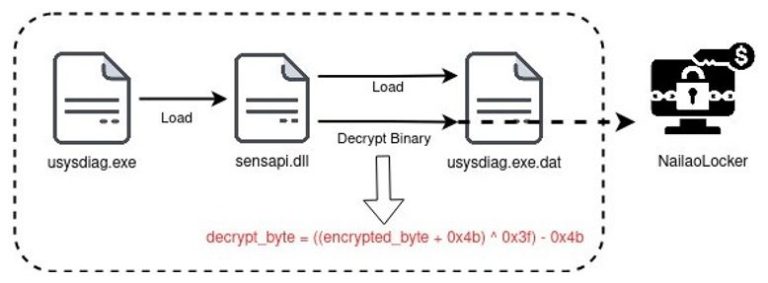
FortiGuard Labs unveils NailaoLocker, a new ransomware using Chinese SM2 encryption and a built-in, non-functional decryptor, suggesting a prototype or decoy.

A new ransomware, KAWA4096, combines features from Qilin and Akira, targeting organizations in the US and Japan with multi-threaded encryption and anti-recovery measures.

FortiCNAPP uncovers Lcrypt0rx, an AI-generated ransomware linked to the H2Miner botnet. Despite its flaws, it achieves near-zero detection, targeting systems for crypto-mining and disruption.