
 Do Son
GLOBAL GROUP, a rebranded RaaS operation, is aggressively targeting critical infrastructure worldwide, leveraging AI chatbots for automated, high-pressure ransom negotiations.
ransomware

BlackSuit, a rebranded Royal/Conti ransomware, unleashes destructive multi-stage attacks. It uses Cobalt Strike, rclone for data exfil, and deletes shadow copies for stealth and speed.

Russian basketball player Daniil Kasatkin was arrested in France on a US warrant for allegedly acting as a ransomware negotiator in attacks on 900+ organizations.

SafePay, a new centralized ransomware group linked to LockBit 3.0, has hit 200+ MSPs/SMBs via RDP. It bypasses Defender, encrypts files, and exfiltrates data using WinRAR and FileZilla.

Iranian-backed "Pay2Key.I2P" ransomware resurfaced on I2P, offering 80% profit for attacks on Western targets. Linked to Fox Kitten & Mimic, it merges cybercrime with geopolitical motives.

Trend Micro uncovers BERT ransomware (Water Pombero) deploying multi-threaded variants against Windows, Linux, and ESXi systems, showing code similarities to REvil's Linux variant.

Splunk uncovers XWorm's evolution: a modular RAT now delivering LockBit ransomware. It uses flexible delivery, AMSI/ETW bypasses, and process injection to evade detection.

The DOJ is criminally investigating a former DigitalMint ransomware negotiator for allegedly colluding with hackers and taking a cut of ransom payments, a betrayal of client trust.

SCATTERED SPIDER targets U.S. airlines with ransomware, vishing, and VMware exploits—CrowdStrike warns of a rising threat across cloud identities.

OFAC sanctioned Russia's Aeza Group, a bulletproof hosting provider, and its executives for enabling ransomware, infostealers (Meduza, Lumma), and darknet drug trafficking operations globally.
A six-day RansomHub attack exploited RDP, used Atera/Splashtop RMM, Mimikatz, and Rclone to breach an enterprise, exfiltrate data, and deploy ransomware.

Dire Wolf, a new Golang ransomware, is targeting manufacturing/tech in 11 countries. It uses double extortion, deletes backups, and has a "wipe mode" that permanently destroys files.

Red Canary uncovers Mocha Manakin, a new threat group using "paste and run" social engineering to deploy NodeInitRAT, a custom NodeJS RAT with potential ransomware links.

Qilin ransomware is rapidly dominating the RaaS landscape, as rivals like RansomHub and LockBit face collapse, internal chaos, and public defacements by "XOXO from Prague."

Hackers leaked 7.4 million Paraguayan citizen records on the dark web, demanding a $7.4M ransom. The breach likely stems from infostealer malware, sparking national security concerns.
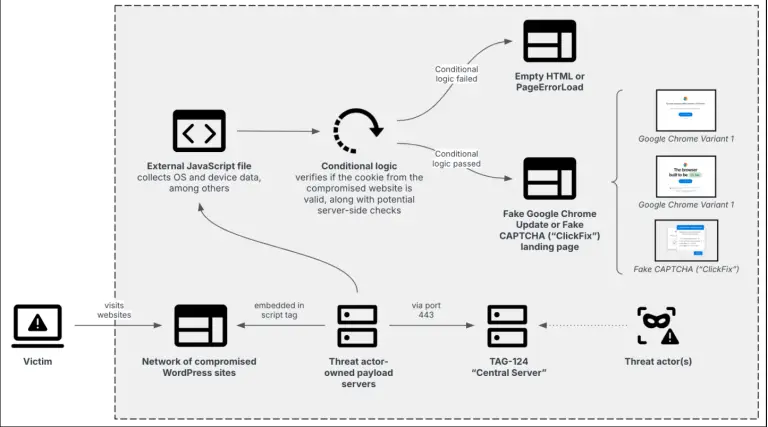
GrayAlpha, linked to FIN7, escalates tactics with fake browser/7-Zip updates and TAG-124 TDS, spreading NetSupport RAT in a multi-pronged infection campaign.

Anubis, a new RaaS, combines ECIES encryption with a "wipe mode" that permanently destroys files. It's actively targeting healthcare, construction, and engineering sectors.

HijackLoader and DeerStealer are surging, using ClickFix social engineering and sophisticated evasion to bypass defenses and exfiltrate sensitive data.

Spectra Ransomware, an evolution of Chaos, encrypts Windows files with AES-RSA, demands $5,000 in Bitcoin, and uses double extortion tactics with system evasion

Symantec reports a Fog ransomware attack on an Asian bank that used unusual tools like employee monitoring software and an APT-linked backdoor, suggesting possible espionage.

CISA warns of active exploitation of a SimpleHelp RMM flaw (CVE-2024-57727) by ransomware actors, impacting utility billing software providers and their customers.

Rapid7 reveals BlackSuit ransomware affiliates are adopting Black Basta tactics, using email bombing, fake Quick Assist scams, and evolving Java RATs.