 Do Son
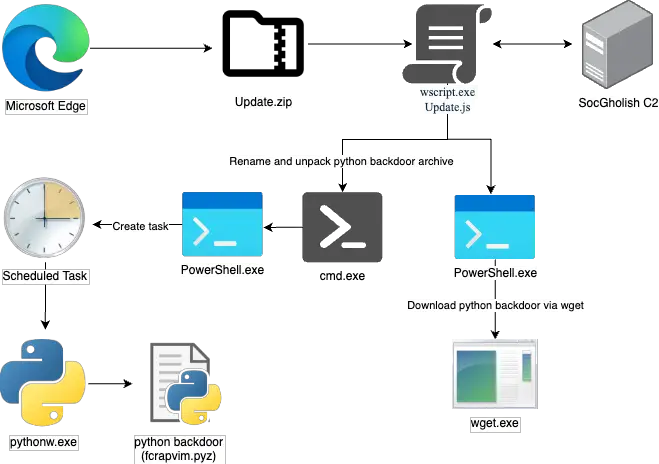
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.
ransomware

Cisco Talos uncovers ToyMaker's IAB activity, paving the way for Cactus ransomware. Learn how LAGTOY backdoor & credential theft led to a major breach.

The Verizon 2025 DBIR reveals a surge in vulnerability exploitation and a doubling of third-party breaches. Learn key findings on ransomware, BYOD risks, and more.

WormLocker ransomware is evolving! Discover how version 2.0 abuses system utilities to take over systems, as revealed by ANY.RUN analysis.

Sekoia TDR reveals Interlock ransomware's evolving tactics, including ClickFix social engineering, to evade detection and steal data.

Cyberattacks are surging against the energy sector, driven by geopolitical tensions. Ransomware, espionage, and supply chain attacks pose major threats.

CrazyHunter ransomware group targets Taiwan's critical infrastructure with sophisticated attacks, using BYOVD techniques and open-source tools.

Week of April 7-13 saw critical Ivanti, WordPress, & Windows vulnerabilities exploited, plus major data breaches impacting millions.

A Trend Micro report explores the evolving tactics of the Russian-speaking cybercriminal underground, including phishing innovations, Web3 scams, the role of ransomware, and the convergence of cyber and physical crime

Microsoft reports active exploitation of a Windows CLFS zero-day (CVE-2025-29824) to escalate privileges and deploy ransomware. Learn about the attacks, the threat actors involved, and how to mitigate the risk.
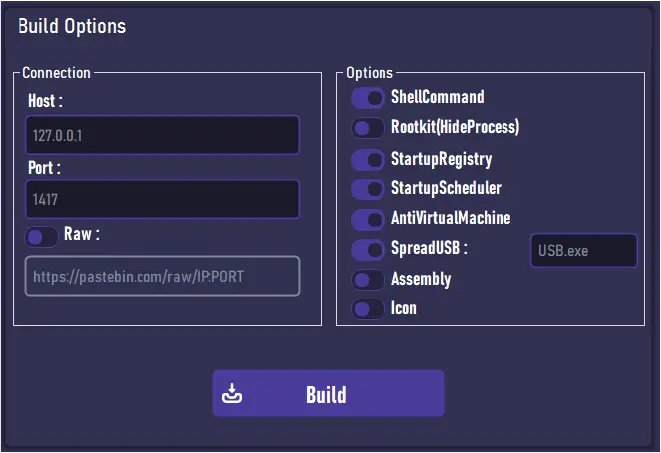
CYFIRMA researchers discovered Neptune RAT, an advanced Remote Access Trojan targeting Windows. Learn about its destructive features, evasion techniques, and distribution methods.

Learn about LARVA-208, the new threat actor using sophisticated social engineering tactics like smishing and vishing.

Explore the evolving threat of ShadowPad malware, now facilitating ransomware attacks linked to Chinese threat actors.

Discover the results of Operation Serengeti, a major joint cybercrime crackdown in Africa. Over 1,000 suspects arrested and millions in financial losses uncovered.

Learn about the International Counter Ransomware Initiative and its global efforts to combat ransomware attacks.

Uncover the shocking truth behind the largest ransom payment in history. Cencora paid a staggering $75 million in Bitcoin to cybercriminals.

Stay informed about the worsening ransomware situation: victims paid $459 million to attackers in the first half of 2024.

Stay informed about the evolving tactics of ransomware operators and how they intensify pressure on their victims.

Advanced failed to adequately protect the information of thousands of individuals, leading to a data breach resulting from a ransomware attack.

Get the latest insights on the increasing prevalence of business email compromise attacks. Learn how to safeguard your organization against this pervasive threat.

Halcyon's research team has identified a new ransomware group dubbed "Volcano Demon," responsible for a series of recent attacks

RansomHub attackers gained initial access by exploiting the Zerologon vulnerability (CVE-2020-1472), which grants domain administrator privileges