 Do Son
A LiteLLM supply chain attack shipped a PyPI credential stealer in version 1.107.0 that grabs cloud, AI tool, and SSH secrets. Act now.
Software Supply Chain
An OVHcloud CLI attack swapped GitHub release files with a secret-stealing binary. Learn which versions are hit in this supply chain attack.
PyPI file hosting errors caused weeks of 502s. See how a Fastly CDN 502 error was traced to one cache node and fixed by August 28.

A new npm supply chain attack hijacked keyv and dozens of packages, spreading Shai-Hulud malware that steals cloud and CI/CD secrets. Rotate keys now.

Doctor Web found a supply chain trojan targeting software developers. This developer-targeting malware steals data, crypto wallets, and mines coins.
A malicious Go module exposed a GitHub lure network of 222 repositories, dubbed Operation Muck and Load, staging RATs and infostealers.
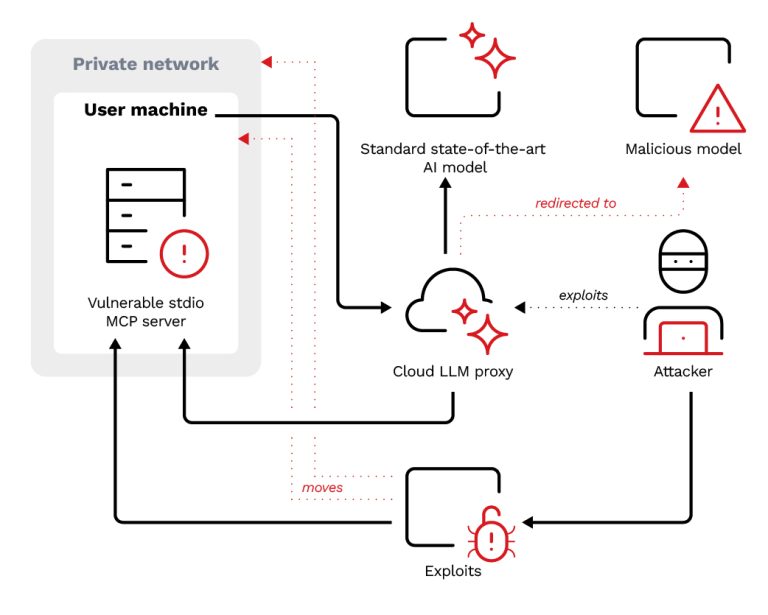
New research explores AI generated code vulnerabilities within MCP server repositories. Learn why expert domain verification remains critical.

The newly uncovered SymJack AI attack technique highlights critical gaps in AI coding agent security. Learn how symlink hijacks exploit developers.
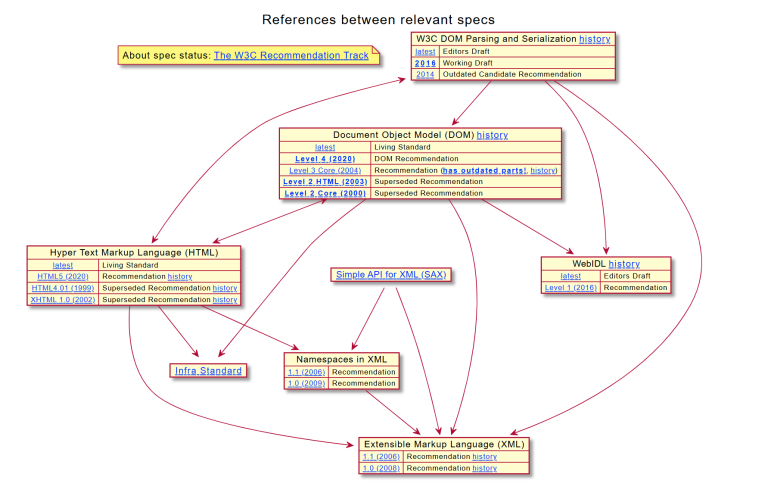
Fix CVE-2026-34601 in @xmldom/xmldom (CVSS 7.5). A CDATA injection flaw allows attackers to bypass "safe zones" and manipulate business logic. Update now!

OpenSSF and other foundations warn that they can no longer be the unpaid gatekeepers of the software supply chain and that enterprises must contribute financially.

A year after its discovery, the XZ backdoor remains in multiple Docker Hub images, posing a risk to developers and the software supply chain.

North Korea's Lazarus Group is waging a covert cyberespionage campaign, poisoning 234+ open-source packages on npm/PyPI to steal secrets from CI/CD pipelines and developer environments.

Banana Squad has compromised over 60 GitHub repos with malicious Python files, using UI quirks to hide malware and steal data from developers via a sophisticated supply chain attack.

A critical CI/CD flaw in remote caches allows undetectable code injection and privilege escalation via cache poisoning, bypassing all security controls.
Sysdig uncovers a campaign exploiting misconfigured Open WebUI instances to deploy AI-assisted cryptominers and infostealers, showcasing new threat vectors.
Research reveals the widely used open source library 'easyjson' is controlled by developers linked to Russia's VK Group, raising security concerns.
JPMorgan Chase CISO urges software providers to prioritize security in SaaS delivery, warning of rising risks to global infrastructure and supply chains.
Malicious open-source packages are stealing crypto wallet credentials! Learn about the threat and how to protect your seed phrases and private keys.