 Do Son
Microsoft links Exchange Server instability to October 2026 Windows updates. See the OWA and mail queue symptoms, plus the registry fix.
Windows Server
Microsoft now audits ReFS removable storage in Windows 11 and will block mounting external ReFS volumes by default starting in January 2027.
Chrome 158 drops XSLT on November 17, which can break RD Web Access on Windows Server. See the timeline and Microsoft's interim fixes.
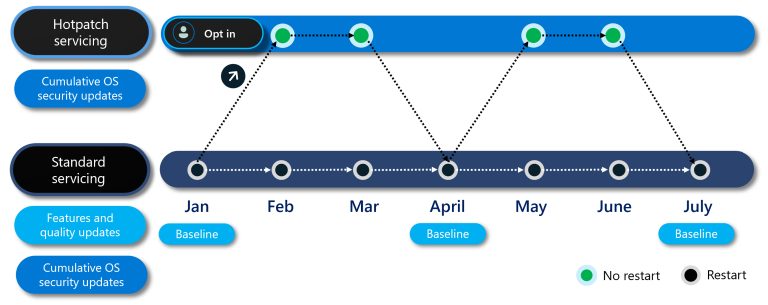
Microsoft alerts IT admins that hotpatch-enrolled systems will require unexpected mandatory reboots in September and October. Prepare for potential downtime.

Discover how Microsoft is strengthening KMS activation by introducing hardware-based trust and TPM verification to combat forged licensing servers.

WSUS sync timeouts and failed Windows Update scans stem from mis-published test detectoids. Microsoft has mitigated it and published a cleanup.

A critical Netlogon RCE vulnerability is actively exploited in the wild. Learn how to secure your Windows domain controllers immediately.

Microsoft has retired its legacy telephone activation system. Learn how to use the new Web Activation Portal to license Windows and Office without an internet connection.

Microsoft will fully retire the WINS name-resolution service after Windows Server 2025. Support for existing deployments ends in 2034, urging migration to DNS now.

Threat actors are actively exploiting a new WSUS RCE flaw (CVE-2025-59287) to gain SYSTEM shells and deploy the dangerous ShadowPad backdoor. Patch immediately!

Microsoft has released an update to fix a bug in Windows Server 2019 that caused cluster disruptions and virtual machine reboots with BitLocker and CSV.

Microsoft has permanently removed the outdated and insecure PowerShell 2.0 from Windows 11, a move that enhances security but may affect some enterprise scripts.
Microsoft's 2011 Secure Boot certificates expire in 2026, impacting all supported Windows versions. Update now via Windows Update to avoid boot failures, especially on isolated systems.

Two Windows Kernel vulnerabilities allow SYSTEM-level privilege escalation. PoC exploit code is publicly available.
Uncover the hidden Windows Server vulnerability that allows attackers to bypass crucial security measures. Find out how to secure your servers against this zero-day exploit.
Microsoft is enhancing VPN security in Windows Server. Learn about the deprecation of PPTP and L2TP protocols and the recommended alternatives.

Security researcher Ynwarcs has published an in-depth analysis and PoC exploit code for a critical zero-click CVE-2024-38063

Discover the details of CVE-2024-38202 and CVE-2024-21302 in Windows and how attackers can exploit them to undermine system integrity

Wei aims to minimize the risk of threat actors reverse-engineering the CVE-2024-38063 exploit, buying time for organizations to secure systems