
 Do Son
North Korea's LABYRINTH CHOLLIMA splits into 3 units: GOLDEN, PRESSURE, & Core. CrowdStrike reveals new strategy targeting crypto & defense.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

APT28 launches "Operation Neusploit" targeting Europe. Hackers exploit CVE-2026-21509 to deploy MiniDoor malware via RTF files. Patch Office now.
Hikvision patches high-severity command injection (CVE-2026-0709) in DS-3WAP access points. Authenticated attackers can execute code. Update now.

Critical KiloView flaw CVE-2026-1453 (CVSS 9.8) allows unauthenticated admin takeover. Broadcast feeds at risk. Check affected E1/E2 versions immediately.

"RedKitten" spies on Iranian protesters using AI-written malware. Attackers use fake death lists to deploy SloppyMIO surveillance tools.

IClickFix malware hijacks 3,800+ WordPress sites with fake Cloudflare CAPTCHAs. This watering hole attack tricks users into running malicious PowerShell.

Apache patches XSS (CVE-2026-23794) & XXE flaws in Syncope. Vulnerability allows session hijacking via login page. Update to v3.0.16 or v4.0.4 now.
A high-severity flaw in OpenClaw (formerly Clawdbot) allows 1-click Remote Code Execution. Update to v2026.1.29 immediately to prevent total account takeover.

NVIDIA’s $100B infrastructure pact with OpenAI has reached a "deep freeze." CEO Jensen Huang cited business discipline concerns and rising rivals like Gemini.

Google’s latest data reveals Android 16 has reached only 7.5% adoption. See how it stacks up against Android 15 and why fragmentation still haunts the platform.

Apple is exploring a "square" clamshell-style iPhone to rival the Galaxy Z Flip. Discover the latest leaks on the 2026 foldable roadmap and the "iPhone Flip."

Jensen Huang dismisses custom AI chips as "illogical," announcing a $45B R&D surge to ensure NVIDIA’s programmable GPUs outpace static ASIC competitors.

Apple’s online store goes "linear," ditching pre-sets for a build-from-scratch Mac experience. Discover how the M5 and RDMA are turning Macs into AI clusters.

Notepad++ confirms update infrastructure was compromised by state-sponsored actors targeting specific users. Update to version 8.8.9 immediately.

Cisco Talos warns of UAT-8099 targeting Asian IIS servers with region-locked BadIIS malware. New variants now attack Linux systems.

"ConsentFix" phishing tricks users into pasting OAuth codes from Azure CLI, bypassing MFA and Conditional Access. Detect this "fix" scam now.

Attackers use fake DHL invoices to sideload Phantom Stealer v3.5.0 via a signed Java utility. Malware hides in AddInProcess32.exe. Watch out.

New "APT IRAN" framework targets energy grids & military networks. Lab52 links the tool to the IRGC. See the threat to critical infrastructure.

INJ3CTOR3 hackers target FreePBX with EncystPHP web shell via CVE-2025-64328. Malware uses cron jobs for persistence. Patch immediately.

New "Exfil Out&Look" attack uses OWA add-ins to steal emails without leaving logs. Microsoft has no immediate fix for this blind spot.

TA584 triples activity with new "Tsundere Bot" malware. Attackers use invisible Registry keys to hide persistence. Read the Proofpoint analysis.
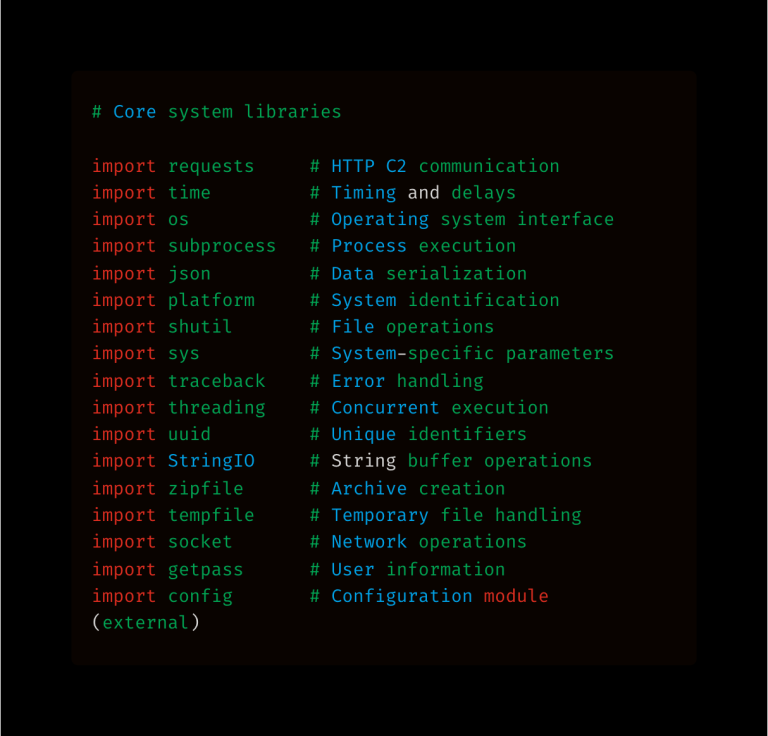
K7 Labs uncovers a stealthy Python-based RAT disguised as an ELF binary. Features adaptive beaconing and anti-forensics to stay hidden. Read the analysis.