
 Do Son
Google’s bulletin sheds light on two bugs, specifically CVE-2023-4863 and CVE-2023-4211, believed to be under limited targeted exploitation
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
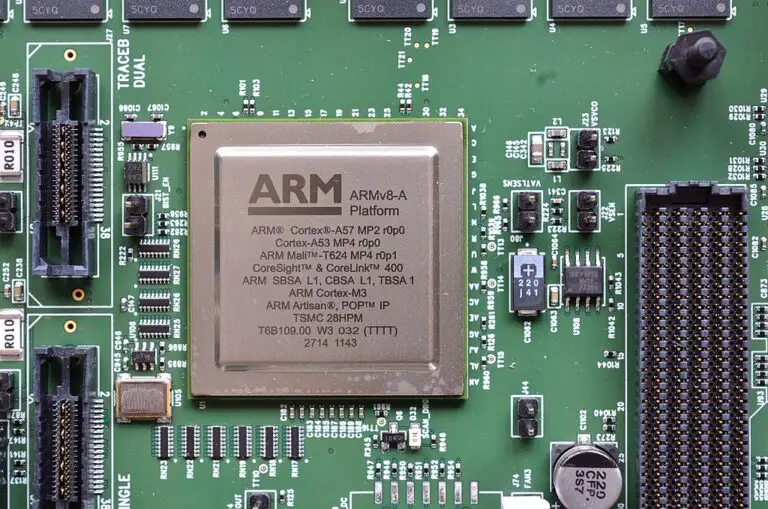
Arm's fix for CVE-2023-4211 has been incorporated into Android and Pixel devices. Google reacted, releasing the patch for its Pixel devices

The CVE-2023-43654 vulnerability in question is a server-side request forgery (SSRF) in PyTorch TorchServe.

Cyber security attacks are at an all-time high. Businesses are often targets or fall victim to attacks. Click here for the risks to keep an eye on.

Currently, Encrypted Client Hello has been embraced by major browsers: Google Chrome and Mozilla Firefox. For Safari: Support is forthcoming.

Menorah malware was spotted playing a crucial role in a recent targeted phishing attack demonstrating the group's undiminished proclivity

the ransomware group RansomedVC has ostentatiously claimed to have successfully infiltrated Sony's systems

The Cl0p ransomware group exploited a popular SQL injection vulnerability (CVE-2023-34362) within the MOVEit file transfer solution

This newfound vulnerability (CVE-2023-41081), graded as "important" in severity, is of particular concern.

The digital realm experienced a wave of unease as Mozilla revealed a critical zero-day vulnerability in its flagship Firefox web browser

Tracked as CVE-2018-14667, this vulnerability has received an alarming severity score of 9.8/10 from Red Hat
The diversity of dietary supplements is increasing every day, but omega-3 continues to remain one of the...

With a towering CVSS score of 9.8, the CVE-2023-42115 vulnerability unveils a gateway for remote attackers to embed arbitrary codes

CVE-2023-42121 allows remote attackers unbridled access to execute arbitrary code on affected installations of the Control Web Panel

A PoC code for a macOS CVE-2023-32364 vulnerability could be exploited to escape a sandbox and execute code within the Terminal

CVE-2023-20109 could allow an authenticated, remote attacker to execute arbitrary code on an affected device or cause the device to crash

The CVE-2023-20252 vulnerability resides in the Security Assertion Markup Language (SAML) APIs of Cisco Catalyst SD-WAN Manager

Google recently revealed in a security advisory that a zero-day vulnerability, designated as CVE-2023-5217, is being actively exploited.

CVE-2023-40044 (CVSS: 10) is a pre-authenticated remote command execution vulnerability that affects versions prior to 8.7.4 and 8.8.2

An attacker could exploit CVE-2023-3767 to execute arbitrary commands on the affected system by sending a specially crafted HTTP request.

CVE-2023-5002 vulnerability has been discovered in pgAdmin, a popular graphical user interface (GUI) management tool for PostgreSQL databases

PoC exploit code has been released for a critical CVE-2023-29357 allowing the elevation of privilege in Microsoft SharePoint Server products