
 Do Son
CISA has added five security flaws to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation in the wild
Vulnerability

PoC exploit code for CVE-2023-22515 was released, which facilitates unauthorized access to Confluence Server and Data Center instances
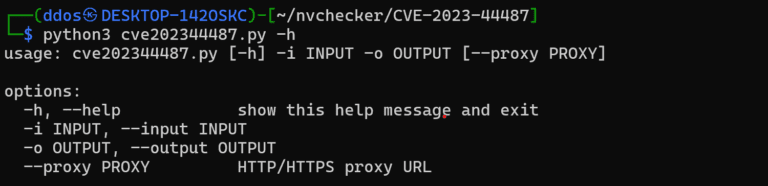
Basic vulnerability scanning to see if web servers may be vulnerable to CVE-2023-44487. The tool checks if a web server accepts HTTP/2 requests
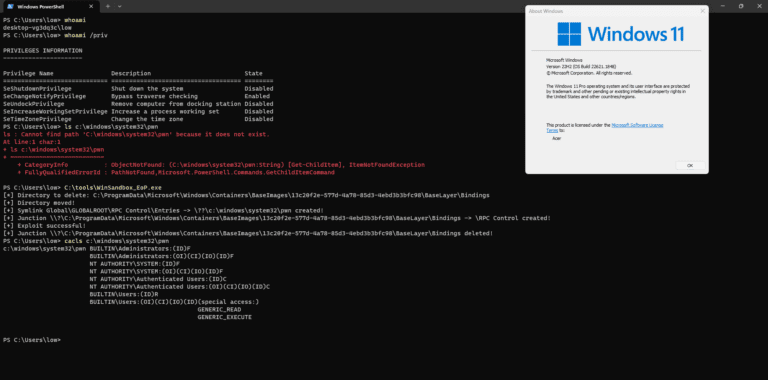
Dragović released a PoC exploit code for the CVE-2023-36723 vulnerability. The exploit code abuses a bug in the Container Manager Service

In one audacious instance, an attacker dispatched an astonishing 398 million requests within a singular second
These patches have now been extended to iOS/iPadOS 16, with the latest iteration being iOS/iPadOS 16.7.1 (20H30).

CVE-2023-45648 vulnerability turns particularly sinister behind a reverse proxy, paving the way for request smuggling.

FortiWLM counterpart, the CVE-2023-34992 vulnerability allows for remote unauthenticated OS command injections

The CVE-2023-21709 vulnerability (CVSS score of 9.8) exposes Exchange servers to privilege escalation attacks.

One of the Message Queuing vulnerabilities that was patched in October Patch Tuesday (CVE-2023-35349) has a CVSS severity score of 9.8/10

The vulnerability, designated as CVE-2023-4966, has been assigned a CVSS score of 9.4, indicating its high severity.

Leading internet giants, Cloudflare, Google, and Amazon AWS, have announced the discovery of a zero-day flaw, the "HTTP/2 Rapid Reset" attack

VLC media player contains two security vulnerabilities that could be exploited by attackers to take control of users' computers.
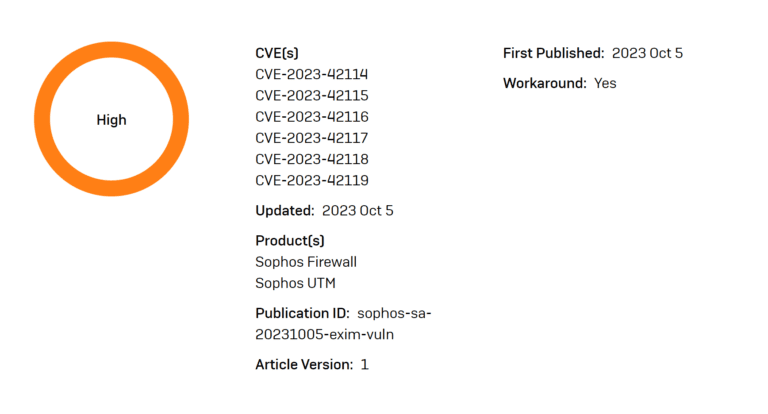
A critical vulnerability has been discovered in the Exim mailer software, which is widely used in Sophos Firewall and SG UTM products

CISA unveiled a comprehensive report elucidating the most common cybersecurity misconfigurations within vast organizational frameworks

By adding an indirect layer to the attack, Meltdown shifts from being a transient execution attack to a stealthier side-channel attack
two critical vulnerabilities have been discovered in Microsoft PC Manager, which could allow a remote attacker to execute arbitrary code

A recently security flaw tracked as CVE-2023-32188, has sent ripples across the cybersecurity community due to its critical severity

CISA has added three new security vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog due to active exploitation
CVE-2023-38545 is a severity-high vulnerability that affects both libcurl and the curl tool. This is a serious problem
A new and dangerous XSS vulnerability has been discovered in Microsoft Office, affecting hundreds of millions of users worldwide
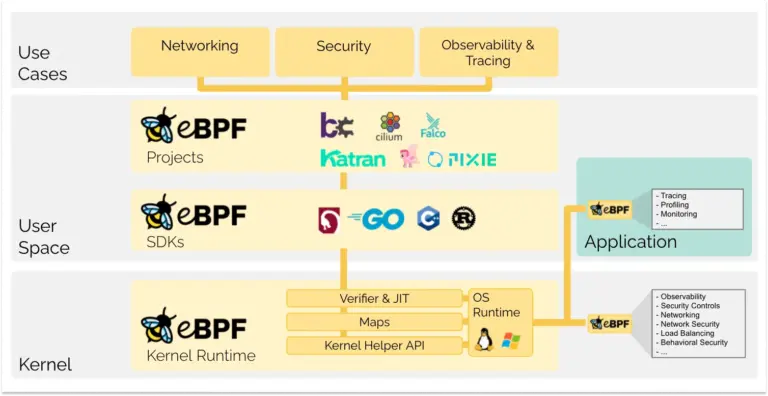
CVE-2023-39191 is a critical security vulnerability that could allow attackers to gain root access to affected systems.