
 Do Son
If exploited, the CVE-2023-23368 vulnerability could allow an attacker to execute arbitrary commands on the affected device.
Vulnerability


Security researchers have discovered four high-severity command injection vulnerabilities in the ASUS RT-AX55 router

CVE-2023-31102 is a serious vulnerability that can allow attackers to execute arbitrary code on the victim's computer.
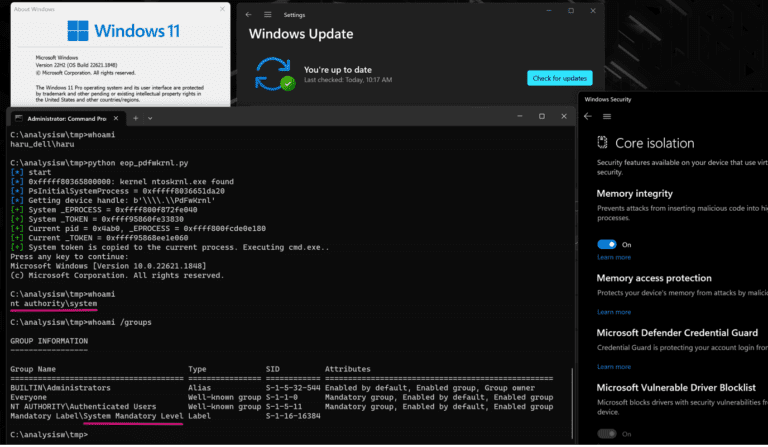
VMware's Threat Analysis Unit has disclosed 34 kernel drivers susceptible to exploitation for firmware modification and privilege escalation by attackers

Mandiant have discerned an active exploitation of a vulnerability within Citrix's NetScaler ADC and Gateway systems
The complete list of all changes introduced in the CVSS v4.0 standard, including more precise differentiation through new base metrics/values
Security researchers at Rapid7 have observed hackers exploiting the vulnerability to deploy the HelloKitty ransomware on target systems

The vulnerability, CVE-2023-20048, has a CVSS score of 9.9, making it one of the most severe security vulnerabilities ever discovered

F5 has issued an urgent warning to organizations about the active exploitation of two critical security vulnerabilities in BIG-IP

The most critical among them is CVE-2023-31027, which boasts a CVSS score of 8.2 out of a potential 10, indicating a high level of danger

CVE-2023-5043 and CVE-2023-5044, stem from insufficient input validation and could lead to arbitrary code execution

Cl0p gained access to the email addresses of approximately 632,000 employees from the U.S. Department of Defense and Justice

Cybersecurity experts have uncovered an attack technique targeting corporate Slack users, aptly termed 'Wiki-Slack.'

CVE-2023-3959 allows attackers to execute arbitrary code on the devices, which could allow them to take complete control of the devices

An attacker could exploit CVE-2023-20886 to redirect a victim to a malicious website that is designed to steal their SAML response
CVE-2023-47174 is a critical bug in Thorn SFTP Gateway that could allow an attacker to execute arbitrary code on SFTP Gateway server

Atlassian has rated the CVE-2023-22518 vulnerability as 9.1/10 severity on the Common Vulnerability Scoring System (CVSS)

In summation, the HackerOne report underscores the profound influence of ethical hackers on the cybersecurity domain

CVE-2023-47090 could allow an attacker to gain access to a NATS.io server and send or receive messages without authorization

Not only does it address CVE-2023-36563, but it also patches up two more zero-day vulnerabilities that hackers have been exploiting

CVE-2023-46748 allows attackers with remote access to the configuration utility to view, add, modify, or delete information in a database