
 Do Son
APT28 has been assailing governmental entities, businesses, universities, research institutions, and analytical centers in France
Vulnerability

To gauge the potential impact of CVE-2023-46604, Qi Anxin CERT replicated the Apache ActiveMQ remote code execution vulnerability

A local privilege escalation (CVE-2023-34057) bug has been discovered in VMware Tools, specifically targeting the macOS operating system
CVE-2023-5815 has been discovered in the plugin that could allow unauthenticated attackers to execute arbitrary code on vulnerable websites

CloudFlare had mitigated thousands of volumetric HTTP Distributed DDoS attacks that exploited the disclosed vulnerability known as HTTP/2 Rapid Reset

The vulnerability, CVE-2023-46747, has a CVSS score of 9.8, making it one of the most severe vulnerabilities ever discovered in F5 BIG-IP

Termed 'iLeakage', this side-channel attack is not only practical but requires minimal resources for execution.

In the ever-evolving landscape of cybersecurity, Apple has taken swift action against a zero-day security vulnerability
The new vulnerability, as revealed by ESET specialists, is identified as CVE-2023-5631 and has a CVSS score of 5.4.

On the competition's inaugural day, security researchers successfully breached the Samsung Galaxy S23 phone twice
CVE-2023-5746 is a critical vulnerability, as it could allow attackers to take complete control of affected devices.

CVE-2023-5363 is caused by an incorrect cipher key and IV length processing during the initialization of some symmetric ciphers

CVE-2023-34048 vulnerability has been discovered in the vCenter Server, specifically in its implementation of the DCERPC protocol

With a PoC exploit for CVE-2023-4966 now available on Github and this vulnerability being actively exploited
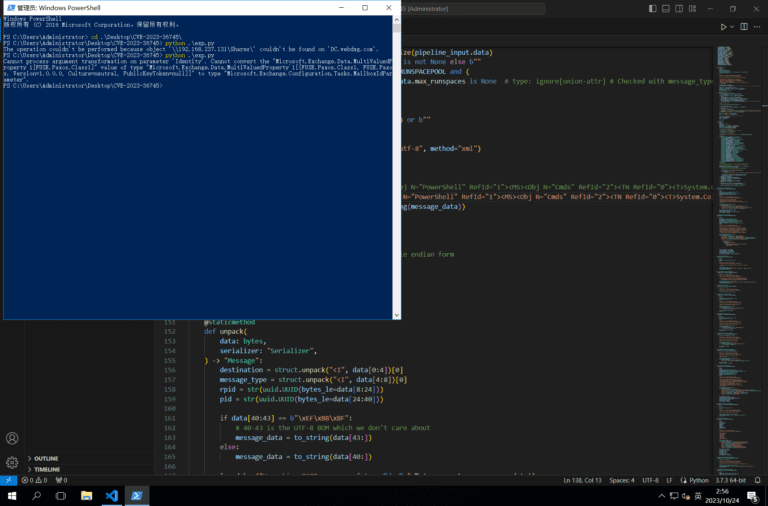
Proof-of-concept (PoC) exploit code has been published for a Microsoft Exchange Server vulnerability tracked as CVE-2023-36745

The CVE-2023-4372 bug is a critical stored Cross-Site Scripting (XSS) vulnerability in the LiteSpeed Cache plugin

This vulnerability stems from a discrepancy in chunked decoder lenience, making Squid susceptible to Request/Response smuggling attacks
iTerm2 existed a CVE-2023-46300 flaw pertaining to how iTerm2 managed certain escape sequences linked to tmux integration

CVE-2023-20273 allows an attacker who has already compromised the device to gain root access and take complete control.

CVE-2023-41895 vulnerability permits users to employ their local credentials and sign in to an external website

CVE-2021-1435 provides attackers a door into the system, permitting them to inject arbitrary commands, all executable as the all-powerful root user
An attacker could exploit CVE-2023-45802 to exhaust the server's memory. This bug affects Apache HTTP Server versions 2.4.55 through 2.4.57