Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Apache MINA Patches Critical Framework Vulnerabilities Apache MINA flaws critical deserialization bypass Apache MINA Deserialization CVE-2026-42778 RCE Apache MINA RCE CVE-2026-41635
  • Vulnerability Report

Apache MINA Patches Critical Framework Vulnerabilities

Do Son June 9, 2026 0

Fix dangerous Apache MINA flaws immediately. Learn how a critical deserialization bypass and a DoS vulnerability leave Java applications exposed.

New Chrome Security Update Addresses Critical V8 Exploit in the Wild Chrome security update exploit in the wild Chrome Zero-Day CVE-2026-3909 Chrome Zero-Day PoC CVE-2026-2441 Chrome Zero-Day CVE-2026-2441 Chrome Zero-Day, Active Exploitation CVE-2025-10585 Chrome vulnerability, zero-day exploit CVE-2025-6558 Chrome Zero-Day, V8 Vulnerability Chrome Zero-Day, Security Update
  • Vulnerability Report

New Chrome Security Update Addresses Critical V8 Exploit in the Wild

Do Son June 9, 2026 0

Apply the new Chrome security update immediately. Google warns that a critical exploit in the wild targets a high-severity V8 engine flaw.

Deep Integration: Apple Intelligence Anchors iOS 27 and macOS 27 Default Application Suites Apple Intelligence WWDC 2026
  • Technology

Deep Integration: Apple Intelligence Anchors iOS 27 and macOS 27 Default Application Suites

Do Son June 9, 2026 0

Discover the new Apple Intelligence WWDC 2026 features. Learn how deep Siri upgrades, Safari tab automation, and iOS 27 tools change your daily workflow.

Sovereign Intelligence: Apple Reimagines Siri with Gemini Core Integration at WWDC 2026 Siri AI standalone app
  • Technology

Sovereign Intelligence: Apple Reimagines Siri with Gemini Core Integration at WWDC 2026

Do Son June 9, 2026 0

Discover the new Siri AI standalone app from WWDC 2026. Learn how the Google Gemini integration brings multimodal vision features to your devices.
Malicious PyPI Package Wave Spreads Evolving Supply Chain Attacks malicious PyPI package wave supply chain attacks
  • Malware

Malicious PyPI Package Wave Spreads Evolving Supply Chain Attacks

Do Son June 9, 2026 0

A new malicious PyPI package wave highlights evolving supply chain attacks. Learn how to protect your CI/CD pipelines from credential theft.

CISA Active Exploit Catalog Expands with Critical Gateway Flaws CISA active exploit catalog critical gateway flaws CVE-2023-27532 & CVE-2024-37383
  • Vulnerability Report

CISA Active Exploit Catalog Expands with Critical Gateway Flaws

Do Son June 9, 2026 0

CISA expands its active exploit catalog with critical gateway flaws in BerriAI LiteLLM and Check Point configurations. Patch immediately.

Accelerating Business Growth: 8 Tips and Considerations Andariel APT
  • Technique

Accelerating Business Growth: 8 Tips and Considerations

Do Son June 8, 2026 0
Growing your business is an exciting phase, but it needs to be approached strategically. Before you dive...
Read More Read more about Accelerating Business Growth: 8 Tips and Considerations
Check Point VPN Vulnerability Exploited in the Wild with Ransomware Links Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Vulnerability Report

Check Point VPN Vulnerability Exploited in the Wild with Ransomware Links

Do Son June 8, 2026 0

A critical Check Point VPN vulnerability is actively exploited in the wild, allowing unauthenticated attackers to bypass user login requirements.

Best B2B Tech Marketing Agencies tech
  • Technique

Best B2B Tech Marketing Agencies

Do Son June 8, 2026 0
Complex B2B technology companies do not fail because they lack content. They fail because their go-to-market systems...
Read More Read more about Best B2B Tech Marketing Agencies
Cyber Espionage Campaign Targets Global Stock Exchange Executive AdaptixC2 Abuse, Russian Cybercrime RondoDox Botnet, Exploit Shotgun China Cyber Power, Red Hackers Nvidia cyberattack
  • Cybercriminals

Cyber Espionage Campaign Targets Global Stock Exchange Executive

Do Son June 8, 2026 0

Discover how stealthy Outlook mailbox theft fueled a 5-month executive espionage campaign at a global stock exchange using trusted cloud tools.

Massive Smishing Error524 Campaign Evades Traditional Security Filters Worldwide Smishing Error524 campaign Group-IB phishing report
  • Cybercriminals

Massive Smishing Error524 Campaign Evades Traditional Security Filters Worldwide

Do Son June 8, 2026 0

Read the Group-IB phishing report detailing the massive Smishing Error524 campaign targeting millions across 72 countries with advanced evasion tactics.

Instagram Account Recovery Flaw Exploited via AI Support Tool Instagram account recovery flaw Meta incident notification Meta AI data center Louisiana Meta AI news partnerships Meta AI Shopping Assistant Meta Vibes standalone app Meta Oversight Board account ban, Instagram permanent suspension review Meta Compute initiative 2026, personal superintelligence nuclear power Meta AI News Licensing Publisher Content Deal Meta Project Mercury Omnilingual ASR 1600 Languages Meta $600B Investment, AI Data Centers Meta AI strategy, Llama models Meta AI Glasses, Smart Glasses
  • Data Leak

Instagram Account Recovery Flaw Exploited via AI Support Tool

Do Son June 8, 2026 0

A serious Instagram account recovery flaw has been exposed. Read this Meta incident notification detailing how AI-assisted bugs bypass security.
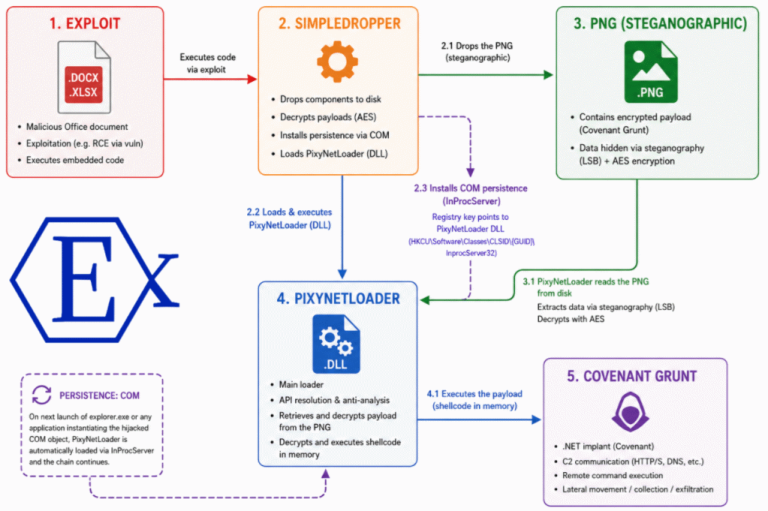
PixyNetLoader Malware Analysis: How APT28 Hides Payloads Inside PNG Files PixyNetLoader malware analysis APT28 steganography attack
  • Malware

PixyNetLoader Malware Analysis: How APT28 Hides Payloads Inside PNG Files

Do Son June 8, 2026 0

Researchers expose PixyNetLoader malware analysis revealing APT28's steganography APT28 attack, hiding Covenant Grunt payloads inside PNG pixels since 2024.

Redis DarkReplica Exploit: Full PoC Code and Technical Details Released CVE-2022-35951 Redis DarkReplica exploit CVE-2026-23631 public disclosure
  • Vulnerability

Redis DarkReplica Exploit: Full PoC Code and Technical Details Released

Do Son June 8, 2026 0

Full technical details and functional PoC code for the Redis DarkReplica exploit are out. Read our breakdown of this CVE-2026-23631 public disclosure.

Broadcom Fixes Critical VMware Stored XSS Bugs VMware stored XSS bugs Broadcom security updates CVE-2023-34039 VMware RCE, virtualization security
  • Vulnerability Report

Broadcom Fixes Critical VMware Stored XSS Bugs

Do Son June 8, 2026 0

New Broadcom security updates fix critical VMware stored XSS bugs. Learn how these vulnerabilities affect Cloud Foundation and how to patch now.

Infrastructure Anomaly: GitHub Suffers Unidentified Global Outage GitHub outage today
  • Technology

Infrastructure Anomaly: GitHub Suffers Unidentified Global Outage

Do Son June 8, 2026 0

Discover the latest updates on the GitHub outage today. Learn about the infrastructure disruption, status page changes, and engineering fixes.
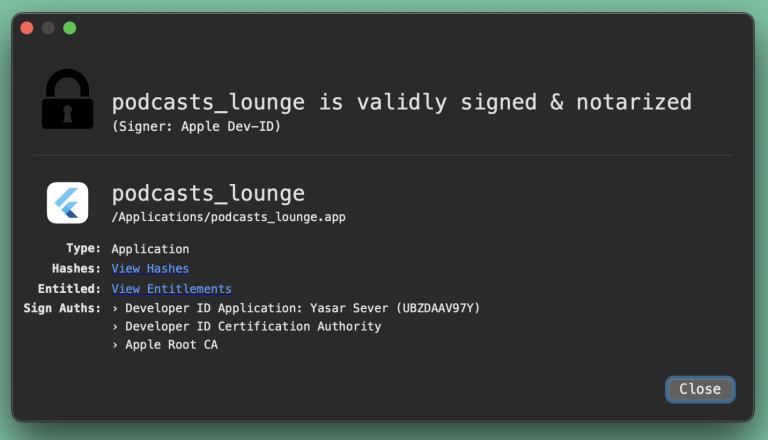
Operation FlutterBridge Malware Targets macOS Platforms with Backdoor Capabilities Operation FlutterBridge malware WebView-based architecture
  • Malware

Operation FlutterBridge Malware Targets macOS Platforms with Backdoor Capabilities

Do Son June 8, 2026 0

New details on the Operation FlutterBridge malware reveal a sneaky WebView-based architecture designed to hijack Chrome browsers on macOS.

Financial Exposure in the Cloud: Persistent Gemini API Caching Flaw Incurs Severe Billing Anomalies Gemini API billing bug
  • Technology

Financial Exposure in the Cloud: Persistent Gemini API Caching Flaw Incurs Severe Billing Anomalies

Do Son June 8, 2026 0

Discover the new Gemini API billing bug. Learn how a phantom caching error costs developers $200 per hour and causes major Google Cloud glitches.

Sovereign Portability: Google Password Manager Embraces Credential Exchange Protocols Google passkey import export
  • Technology

Sovereign Portability: Google Password Manager Embraces Credential Exchange Protocols

Do Son June 8, 2026 0

Discover the new Google passkey import export feature. Learn how the Google Play Services update allows secure passkey migration.
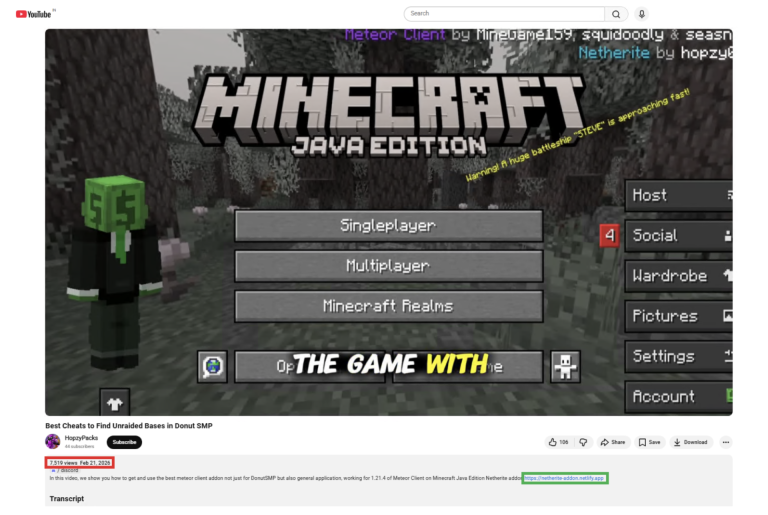
Deceptive WeedHack Malware Campaign Infects Thousands of Minecraft Players WeedHack malware campaign free Minecraft mods
  • Malware

Deceptive WeedHack Malware Campaign Infects Thousands of Minecraft Players

Do Son June 8, 2026 0

The active WeedHack malware campaign spreads via fake videos offering free Minecraft mods, leading to account hijacking and stealthy cyberbullying.

The Fractured Evolution of Wireless Connectivity: Stagnant Wi-Fi 7 Adoption and the Emergence of Wi-Fi 8 Wi-Fi 8 standard features
  • Technology

The Fractured Evolution of Wireless Connectivity: Stagnant Wi-Fi 7 Adoption and the Emergence of Wi-Fi 8

Do Son June 8, 2026 0

Discover the upcoming Wi-Fi 8 standard features. Learn why the 802.11bn upgrade prioritizes network reliability over raw speed for 50G PON.
Shopper Laravel Flaw Exploit Sparks Urgent E-Commerce Security Warning Shopper Laravel flaw Shopper Laravel flaw exploit
  • Vulnerability Report

Shopper Laravel Flaw Exploit Sparks Urgent E-Commerce Security Warning

Do Son June 8, 2026 0

A critical Shopper Laravel flaw has emerged. This Shopper Laravel flaw exploit allows complete admin takeover, so update your store immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.