Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Cisco Patches High-Severity Remote Code Execution in UCS Central Alongside ISE and Unified CM Flaws Cisco UCS Central security updates for CVE-2026-76506, CVE-2026-20241, and CVE-2026-76419
  • Vulnerability Report

Cisco Patches High-Severity Remote Code Execution in UCS Central Alongside ISE and Unified CM Flaws

Do Son November 5, 2026 0

Update Cisco UCS Central, ISE, and Unified CM now to patch CVE-2026-76506, CVE-2026-20241, and CVE-2026-76419 against remote code execution.
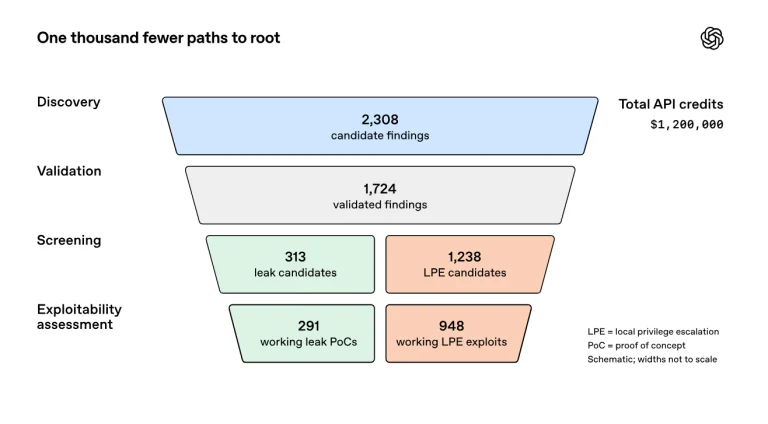
OpenAI Cyber Model Uncovers 1,724 Linux Kernel Vulnerabilities and Builds 948 Root Exploits OpenAI cyber model pipeline discovering Linux kernel vulnerabilities and generating patches
  • Linux

OpenAI Cyber Model Uncovers 1,724 Linux Kernel Vulnerabilities and Builds 948 Root Exploits

Do Son November 5, 2026 0

An upcoming OpenAI cyber model found 1,724 Linux kernel vulnerabilities and built 948 local root exploits to help maintainers patch critical bugs.
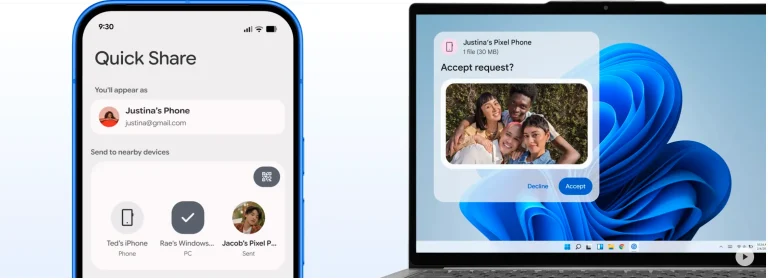
Android Quick Share Backup to Windows PC Rolls Out Android Quick Share backup diagram illustrating automatic media sync between Android and Windows PC
  • Android

Android Quick Share Backup to Windows PC Rolls Out

Do Son November 5, 2026 0

Google Play services now enables automated Android Quick Share backup to Windows PC, syncing photos and videos silently over local networks.
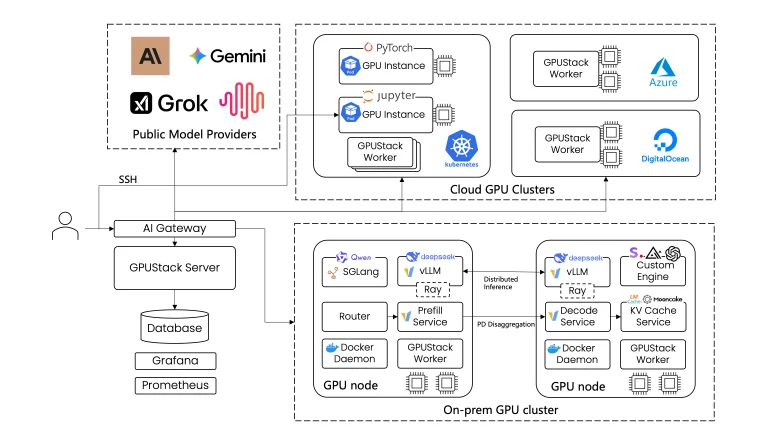
Attackers Exploit Critical GPUStack Authentication Bypass in the Wild to Run Reverse Shells GPUStack authentication bypass advisory for CVE-2026-102895 and CVE-2026-102894 exploited in the wild
  • Vulnerability Report

Attackers Exploit Critical GPUStack Authentication Bypass in the Wild to Run Reverse Shells

Do Son November 5, 2026 0

Attackers exploit the GPUStack authentication bypass CVE-2026-102895 in the wild. Update to 2.2.2 now to fix this flaw and CVE-2026-102894.
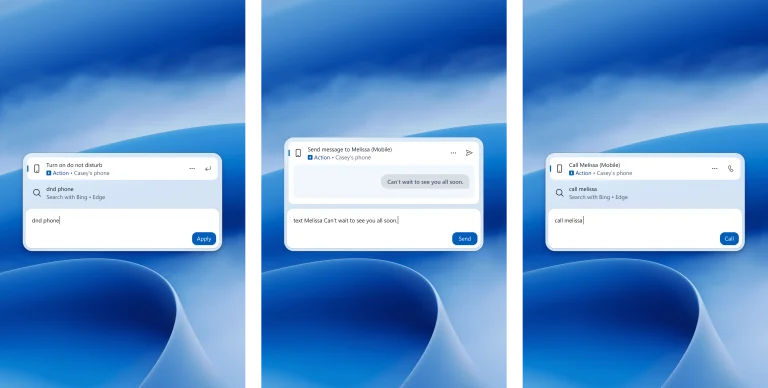
Windows 11 Android Apps Return via Taskbar Search Windows 11 Android apps streaming interface showing taskbar search results and Phone Link mobile mirroring
  • Windows

Windows 11 Android Apps Return via Taskbar Search

Do Son November 5, 2026 0

Microsoft revives Windows 11 Android apps integration via Phone Link and taskbar search, streaming mobile software directly from compatible devices.
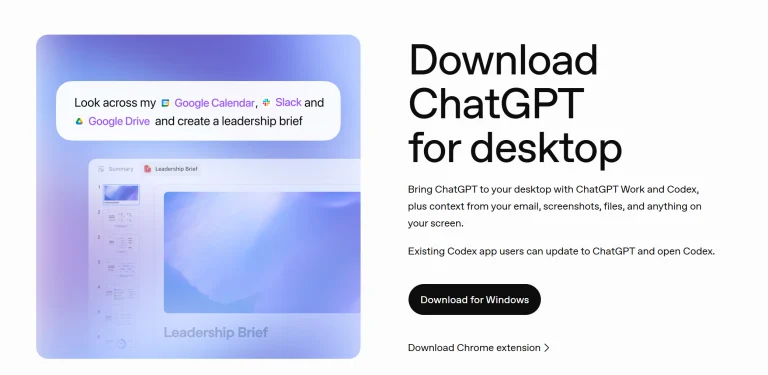
Classic ChatGPT Desktop App Set for Retirement Classic ChatGPT desktop app retirement notice diagram illustrating new ChatGPT desktop app migration
  • Technology

Classic ChatGPT Desktop App Set for Retirement

Do Son November 5, 2026 0

OpenAI announced that the classic ChatGPT desktop app will retire on January 30, 2027, as chat and Work features merge into a unified application.
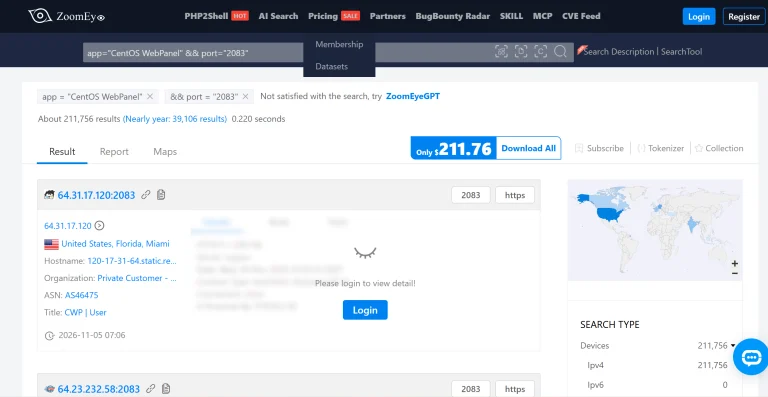
Control Web Panel Patches Ten Flaws Allowing Unauthenticated Root Code Execution Control Web Panel security advisory for CVE-2026-73695 and CVE-2026-73696
  • Vulnerability Report

Control Web Panel Patches Ten Flaws Allowing Unauthenticated Root Code Execution

Do Son November 5, 2026 0

Update Control Web Panel to version 1.29 now to patch CVE-2026-73695, CVE-2026-73696, and eight other flaws allowing unauthenticated root RCE.
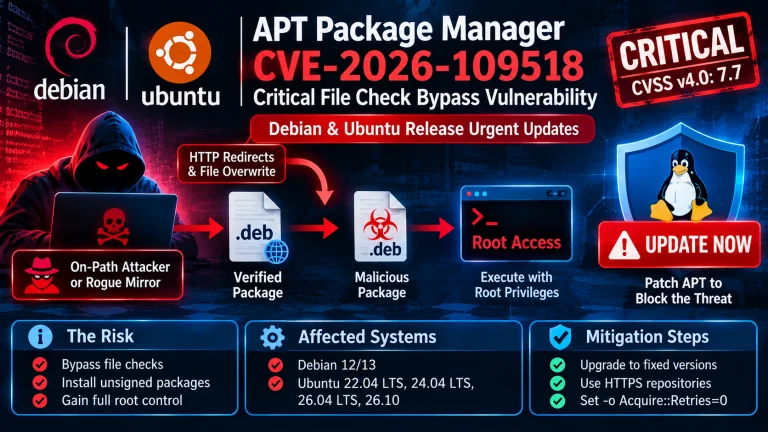
Debian and Ubuntu Patch Critical APT Package Manager Flaw Allowing Root Code Execution APT package manager security update for CVE-2026-109518 on Debian and Ubuntu
  • Vulnerability Report

Debian and Ubuntu Patch Critical APT Package Manager Flaw Allowing Root Code Execution

Do Son November 5, 2026 0

Update your Linux systems now to fix CVE-2026-109518, a critical APT package manager flaw that lets on-path attackers run arbitrary code as root.
Apache Vulnerabilities in ZooKeeper, OpenOffice, ActiveMQ and Juneau Get Fixes Apache vulnerabilities in Apache ZooKeeper, OpenOffice, ActiveMQ and Juneau including CVE-2026-115448
  • Vulnerability Report

Apache Vulnerabilities in ZooKeeper, OpenOffice, ActiveMQ and Juneau Get Fixes

Do Son November 5, 2026 0

35 Apache vulnerabilities fixed, including Apache ZooKeeper flaws CVE-2026-115448 and CVE-2026-100252, plus OpenOffice, ActiveMQ and Juneau bugs.
ASUS Security Vulnerabilities Patched in New Updates ASUS security vulnerabilities diagram showing ASUS security vulnerabilities update for router and PC software
  • Vulnerability Report

ASUS Security Vulnerabilities Patched in New Updates

Do Son November 5, 2026 0

Install the ASUS security vulnerabilities update to fix four critical ASUS security vulnerabilities affecting ASUS routers and Windows system software.
Citrix Security Vulnerabilities: Patch 9.8 CVSS Flaws Citrix security vulnerabilities diagram showing Citrix security vulnerabilities update for XenServer and Scout
  • Vulnerability Report

Citrix Security Vulnerabilities: Patch 9.8 CVSS Flaws

Do Son November 5, 2026 0

Install the Citrix security vulnerabilities update to patch critical Citrix security vulnerabilities affecting XenServer hypervisors and Scout gateways.
Persistent iOS Lockdown Mode Jailbreak Demonstrated iOS Lockdown Mode jailbreak diagram illustrating persistent iPhone exploitation via AirDrop PDF payload
  • Vulnerability Report

Persistent iOS Lockdown Mode Jailbreak Demonstrated

Do Son November 5, 2026 0

Researchers demonstrated a persistent iOS Lockdown Mode jailbreak via AirDrop, maintaining root access across reboots and major updates.
The Hidden Security Danger of Using Multiple File Storage Tools Cloud
  • Technique

The Hidden Security Danger of Using Multiple File Storage Tools

Do Son November 4, 2026 0
Most businesses don’t plan to use five different places to store their files; it just happens. When...
Read More Read more about The Hidden Security Danger of Using Multiple File Storage Tools
WatchGuard Patches Four Critical and High Flaws in AuthPoint Gateway WatchGuard AuthPoint Gateway security advisory for CVE-2026-121639 and CVE-2026-121638
  • Vulnerability Report

WatchGuard Patches Four Critical and High Flaws in AuthPoint Gateway

Do Son November 4, 2026 0

Update WatchGuard AuthPoint Gateway to version 7.6.0 now to fix CVE-2026-121639, CVE-2026-121638, and two other critical authentication flaws.
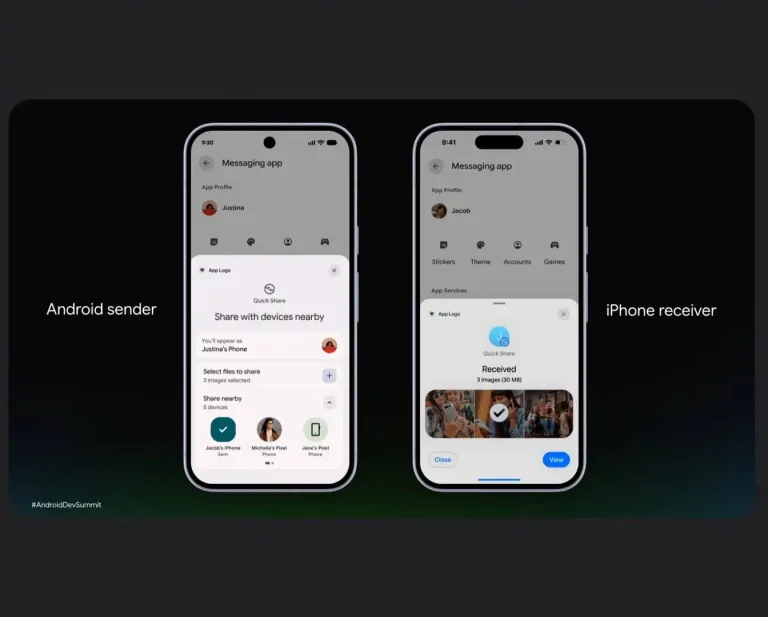
Google Quick Share SDK Brings Seamless Cross-Platform Sharing Google Quick Share SDK interface diagram illustrating cross-platform file sharing and AirDrop interoperability
  • Android

Google Quick Share SDK Brings Seamless Cross-Platform Sharing

Do Son November 4, 2026 0

Google announced the Google Quick Share SDK for Android and iOS, bringing cross-platform file sharing and native AirDrop compatibility to third-party apps.
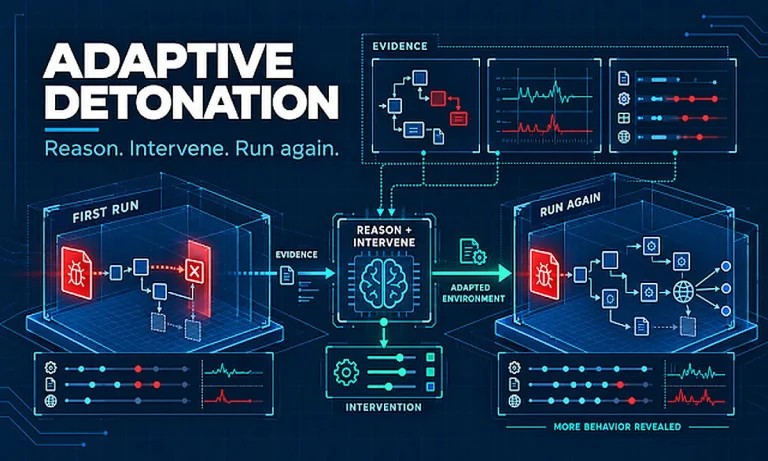
The Sandbox Fights Back: Joe Security Launches Adaptive Detonation download_1_1793785960hBrJU0xbdD
  • Press Release

The Sandbox Fights Back: Joe Security Launches Adaptive Detonation

cybernewswire November 4, 2026 0
Reinach, Switzerland, 4th November 2026, CyberNewswire
Read More Read more about The Sandbox Fights Back: Joe Security Launches Adaptive Detonation
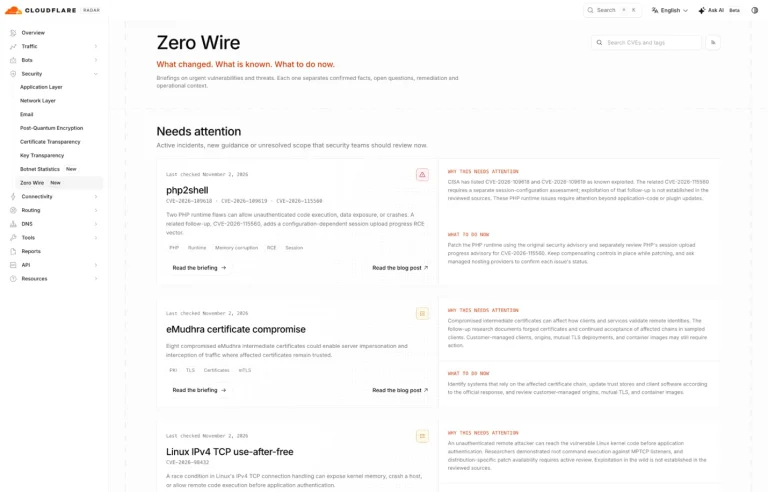
Cloudflare Launches Zero Wire Vulnerability Platform Cloudflare Zero Wire vulnerability intelligence platform dashboard displaying threat telemetry and security briefs
  • Technology

Cloudflare Launches Zero Wire Vulnerability Platform

Do Son November 4, 2026 0

Cloudflare launched Cloudflare Zero Wire, a public vulnerability intelligence feed tracking critical software flaws, active exploits, and AI audit prompts.
Rails 8.0.5.2 and 8.1.4.1 Fix 21 Security Flaws, Including Critical Active Storage File Write Bug Rails security update 8.0.5.2 and 8.1.4.1 fixing critical Active Storage file write flaw
  • Vulnerability Report

Rails 8.0.5.2 and 8.1.4.1 Fix 21 Security Flaws, Including Critical Active Storage File Write Bug

Do Son November 4, 2026 0

Rails security update 8.0.5.2 and 8.1.4.1 fixes 21 flaws, including a critical Active Storage file write bug (CVSS 9.8). Rails 8.0 support ends Nov 7.
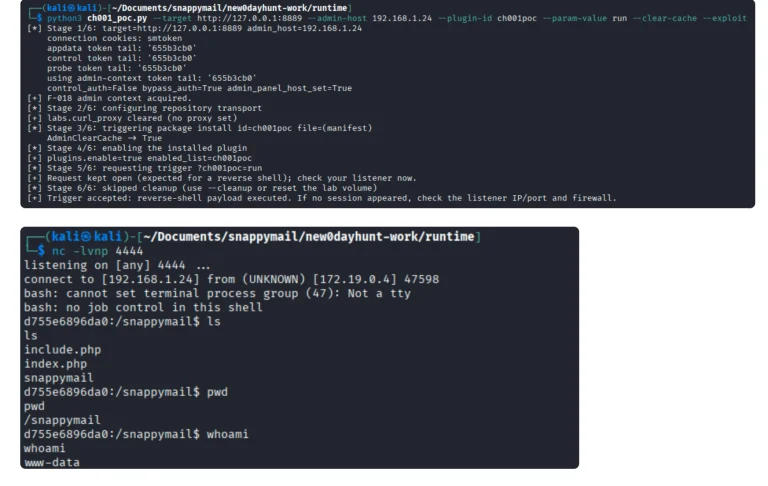
SnappyMail Remote Code Execution Chain Disclosed With Public PoC Exploit Code SnappyMail RCE exploit chain with proof-of-concept exploit code publicly disclosed
  • Vulnerability Report

SnappyMail Remote Code Execution Chain Disclosed With Public PoC Exploit Code

Do Son November 4, 2026 0

SnappyMail RCE chain disclosed with a public proof-of-concept exploit. The auth bypass hit dev builds only; avoid master builds from Oct 22-Nov 4.

Threat Actors Hijack Enterprise AI Models in Costly LLMJacking Cloud Attacks CRussian Market, "Fly" (Flyded) hange Healthcare Cyberattack - CVE-2024-50603 Exploit
  • Cybercriminals

Threat Actors Hijack Enterprise AI Models in Costly LLMJacking Cloud Attacks

Do Son November 4, 2026 0

Mandiant warns that enterprise LLMJacking cloud attacks drain API quotas. Attackers use LLMJacking cloud attacks to resell access via illicit mixer portals.
Airbyte Vulnerability Exploited in the Wild Lets Attackers Run Code in Connector Builder Airbyte vulnerability exploited in the wild in Connector Builder allowing code execution
  • Vulnerability Report

Airbyte Vulnerability Exploited in the Wild Lets Attackers Run Code in Connector Builder

Do Son November 4, 2026 0

Airbyte vulnerability exploited in the wild lets users run code in Connector Builder containers. Upgrade self-managed Airbyte to 2.2.0 now.
Kimsuky Operation GitPower Staging Infrastructure Stays Live on GitHub Operation GitPower and Kimsuky Operation GitPower GitHub infrastructure diagram
  • Cybercriminals

Kimsuky Operation GitPower Staging Infrastructure Stays Live on GitHub

Do Son November 4, 2026 0

The VULONE Team reveals that the Kimsuky Operation GitPower campaign remains live on GitHub, with Operation GitPower repos staging AnyDesk malware.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.