Skip to content
September 27, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
AmateraStealer (ACRStealer) Evolves: New Version Uses Low-Level NTAPIs & Heaven’s Gate for Evasion AmateraStealer, Infostealer Evolution
  • Malware

AmateraStealer (ACRStealer) Evolves: New Version Uses Low-Level NTAPIs & Heaven’s Gate for Evasion

Do Son July 23, 2025 0
Read More Read more about AmateraStealer (ACRStealer) Evolves: New Version Uses Low-Level NTAPIs & Heaven’s Gate for Evasion
DCHSpy Android Spyware Linked to Iran’s MuddyWater APT, Targets Geopolitical Foes with Starlink Lures Android Spyware, MuddyWater APT
  • Cyber Security
  • Malware

DCHSpy Android Spyware Linked to Iran’s MuddyWater APT, Targets Geopolitical Foes with Starlink Lures

Do Son July 23, 2025 0
Read More Read more about DCHSpy Android Spyware Linked to Iran’s MuddyWater APT, Targets Geopolitical Foes with Starlink Lures
AccuKnox Named Top AI Security Startup at Security BSides Bangalore 2025 image1_1753095381Q5ghkaV51r
  • Press Release

AccuKnox Named Top AI Security Startup at Security BSides Bangalore 2025

cybernewswire July 22, 2025 0
Read More Read more about AccuKnox Named Top AI Security Startup at Security BSides Bangalore 2025
New Report Reveals Just 10% of Employees Drive 73% of Cyber Risk Cyberwire_Image_Cyentia_1753106017AQGHGG6c1J
  • Press Release

New Report Reveals Just 10% of Employees Drive 73% of Cyber Risk

cybernewswire July 22, 2025 0
Read More Read more about New Report Reveals Just 10% of Employees Drive 73% of Cyber Risk
Urgent: Cisco ISE Flaws (CVSS 10.0) Actively Exploited in the Wild – Patch Immediately! Cisco ISE Exploitation
  • Vulnerability Report

Urgent: Cisco ISE Flaws (CVSS 10.0) Actively Exploited in the Wild – Patch Immediately!

Do Son July 22, 2025 0
Read More Read more about Urgent: Cisco ISE Flaws (CVSS 10.0) Actively Exploited in the Wild – Patch Immediately!
Firefox 141 Arrives: AI Tab Grouping, Linux Memory Boosts, and WebGPU on Windows Firefox 32-bit Linux Firefox, CRLite Firefox 141, AI Tab Groups Firefox Focus Android
  • Technology

Firefox 141 Arrives: AI Tab Grouping, Linux Memory Boosts, and WebGPU on Windows

Do Son July 22, 2025 0
Read More Read more about Firefox 141 Arrives: AI Tab Grouping, Linux Memory Boosts, and WebGPU on Windows
GitHub Now Supports Google Social Login: Streamlined Sign-in for Developers GitHub Social Login, Google Integration
  • Technology

GitHub Now Supports Google Social Login: Streamlined Sign-in for Developers

Do Son July 22, 2025 0
Read More Read more about GitHub Now Supports Google Social Login: Streamlined Sign-in for Developers
Critical Kubernetes Image Builder Flaw: Default Credentials Grant Root Access to Windows Nodes Ingress-Nginx Vulnerability Kubernetes RCE Vulnerability CVE-2025-9708 Kubernetes Security, Image Builder Vulnerability CVE-2024-10220 - OPA Gatekeeper Bypass
  • Vulnerability

Critical Kubernetes Image Builder Flaw: Default Credentials Grant Root Access to Windows Nodes

Do Son July 22, 2025 0
Read More Read more about Critical Kubernetes Image Builder Flaw: Default Credentials Grant Root Access to Windows Nodes
UK Forges Strategic AI Alliance with OpenAI to Boost Infrastructure and Safety Research ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

UK Forges Strategic AI Alliance with OpenAI to Boost Infrastructure and Safety Research

Do Son July 22, 2025 0
Read More Read more about UK Forges Strategic AI Alliance with OpenAI to Boost Infrastructure and Safety Research
Chrome for iOS Levels Up: New Features Enhance Data Separation for Work and Personal Accounts Chrome iOS, Enterprise Features
  • Technology

Chrome for iOS Levels Up: New Features Enhance Data Separation for Work and Personal Accounts

Do Son July 22, 2025 0
Read More Read more about Chrome for iOS Levels Up: New Features Enhance Data Separation for Work and Personal Accounts
ChatGPT Now Handles 2.5 Billion Requests Daily, Challenging Google’s Search Dominance AI Empire, Sam Altman OpenAI Government, AI Procurement ChatGPT Usage, AI Growth ChatGPT Enterprise, AI Business Tools ChatGPT Free ChatGPT Memory AI Personalization
  • Technology

ChatGPT Now Handles 2.5 Billion Requests Daily, Challenging Google’s Search Dominance

Do Son July 22, 2025 0
Read More Read more about ChatGPT Now Handles 2.5 Billion Requests Daily, Challenging Google’s Search Dominance
Google Teases Pixel 10 Design on Store Page: New Colors, Telephoto Lens for Standard Model Pixel Switch 2 Webcam Google UVC Fix Pixel 10, Google Store Teaser
  • Android

Google Teases Pixel 10 Design on Store Page: New Colors, Telephoto Lens for Standard Model

Do Son July 22, 2025 0
Read More Read more about Google Teases Pixel 10 Design on Store Page: New Colors, Telephoto Lens for Standard Model
Microsoft 365 UWP App is Dying: Move to Click-to-Run Before October 2025 EOL student discount Microsoft 365, Intelligent Services Microsoft 365 UWP, App Deprecation Microsoft 365, Startup Boost Windows 10 EOL, Microsoft 365 Support Protocol Deprecation Microsoft 365 Updates, IT Admin Alert Microsoft 365 VPN shut down Microsoft Authenticator, password manager Windows 10 Microsoft 365 Microsoft nonprofit policy, software donations
  • Technology

Microsoft 365 UWP App is Dying: Move to Click-to-Run Before October 2025 EOL

Do Son July 22, 2025 0
Read More Read more about Microsoft 365 UWP App is Dying: Move to Click-to-Run Before October 2025 EOL
Xbox Unleashes “Cross-Device Play History”: Seamless Cloud Gaming Across All Your Devices Xbox Cloud Gaming, Cross-Device Play History
  • Technology

Xbox Unleashes “Cross-Device Play History”: Seamless Cloud Gaming Across All Your Devices

Do Son July 22, 2025 0
Read More Read more about Xbox Unleashes “Cross-Device Play History”: Seamless Cloud Gaming Across All Your Devices
India’s Chip Ambition: First “Made in India” Semiconductor & 6 New Fabs by 2025 India Semiconductors, Chip Manufacturing Linux Malware Campaign
  • Technology

India’s Chip Ambition: First “Made in India” Semiconductor & 6 New Fabs by 2025

Do Son July 22, 2025 0
Read More Read more about India’s Chip Ambition: First “Made in India” Semiconductor & 6 New Fabs by 2025
Corning Avoids Massive EU Fine by Ending Exclusive Smartphone Glass Deals Apple Google EU alliance DMA European Commission Breach Trivy Supply Chain Attack Europa.eu Breach EU Cloud Infrastructure EU Cyber Sanctions State-Sponsored Hacking EU 2040 Emissions Target, Europe Climate Leadership AWS Azure DMA Cloud Gatekeeper DSA violation, illegal content Apple DMA Delay, iPhone Mirroring EU EU Age Verification, Google Play Integrity Corning Antitrust, EU Competition Apple EU Digital Markets Act App Store commission European Union cyberattacks - InvestAI EU Targets Musk’s X Digital Markets Act, EU fines
  • Technology

Corning Avoids Massive EU Fine by Ending Exclusive Smartphone Glass Deals

Do Son July 22, 2025 0
Read More Read more about Corning Avoids Massive EU Fine by Ending Exclusive Smartphone Glass Deals
Urgent Sophos Firewall Update: Two Critical RCE Flaws (CVE-2025-6704, CVE-2025-7624) Patched via Hotfixes Sophos Firewall, Remote Code Execution
  • Vulnerability Report

Urgent Sophos Firewall Update: Two Critical RCE Flaws (CVE-2025-6704, CVE-2025-7624) Patched via Hotfixes

Do Son July 22, 2025 0
Read More Read more about Urgent Sophos Firewall Update: Two Critical RCE Flaws (CVE-2025-6704, CVE-2025-7624) Patched via Hotfixes
Critical Flaw (CVE-2025-24936, CVSS 9.0) in Nokia WaveSuite NOC Expose Telecom Networks to RCE Nokia WaveSuite, Command Injection
  • Vulnerability Report

Critical Flaw (CVE-2025-24936, CVSS 9.0) in Nokia WaveSuite NOC Expose Telecom Networks to RCE

Do Son July 22, 2025 0
Read More Read more about Critical Flaw (CVE-2025-24936, CVSS 9.0) in Nokia WaveSuite NOC Expose Telecom Networks to RCE
Greedy Sponge Reemerges: New AllaKore RAT Variant and SystemBC Target Mexico’s Financial Sector Greedy Sponge, AllaKore RAT
  • Cybercriminals

Greedy Sponge Reemerges: New AllaKore RAT Variant and SystemBC Target Mexico’s Financial Sector

Do Son July 22, 2025 0
Read More Read more about Greedy Sponge Reemerges: New AllaKore RAT Variant and SystemBC Target Mexico’s Financial Sector
Android Malware Strikes: Fake Facebook & TikTok Apps Impersonate Brands for Traffic Monetization BadBox 2.0, Android Botnet Alien spyware - CVE-2024-43093
  • Malware

Android Malware Strikes: Fake Facebook & TikTok Apps Impersonate Brands for Traffic Monetization

Do Son July 22, 2025 0
Read More Read more about Android Malware Strikes: Fake Facebook & TikTok Apps Impersonate Brands for Traffic Monetization
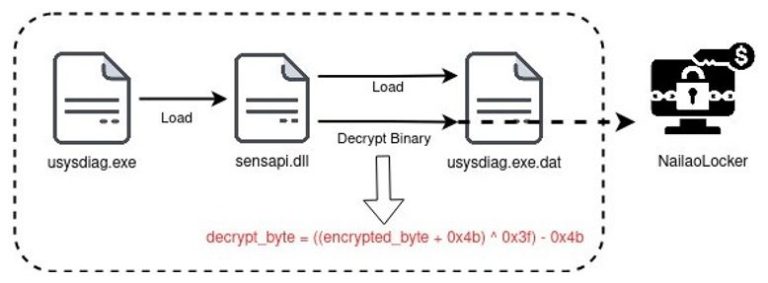
NailaoLocker Ransomware: Chinese SM2 Crypto and Built-in Decryptor Raise Questions NailaoLocker, SM2 Ransomware
  • Malware

NailaoLocker Ransomware: Chinese SM2 Crypto and Built-in Decryptor Raise Questions

Do Son July 22, 2025 0
Read More Read more about NailaoLocker Ransomware: Chinese SM2 Crypto and Built-in Decryptor Raise Questions
Important wolfSSL Update: Critical Apple Trust Store Bypass & Predictable Randomness Flaws Patched wolfSSL Vulnerabilities, TLS/SSL Security
  • Vulnerability Report

Important wolfSSL Update: Critical Apple Trust Store Bypass & Predictable Randomness Flaws Patched

Do Son July 22, 2025 0
Read More Read more about Important wolfSSL Update: Critical Apple Trust Store Bypass & Predictable Randomness Flaws Patched
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-65660CVSS 8.8
    Improper control of generation of code (\'code injection\') in Microsoft Office SharePoint allows an authorized attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 25, 2026
  • CVE-2026-5430CVSS 10.0
    The JWT authentication mechanism accepts tokens signed with algorithms other than those explicitly configured or supported. This allows...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-48842CVSS 8.1
    Roundcube Webmail 1.6.x before 1.6.16 and 1.7.x before 1.7.1 has Pre-authentication SQL injection in the virtuser_query plugin via...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-87902
    Unauthenticated path traversal in page-template resolution leading to conditional RCE An unauthenticated attacker can make get_page_template() page-template resolution...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 23, 2026
  • CVE-2026-94127CVSS 9.8
    When a BIG-IP APM access policy and an OAuth profile is configured on a virtual server, specific malicious...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-85102CVSS 9.8
    Improper certificate trust validation during VPN negotiation in Check Point Quantum Security Gateway may allow an unauthenticated remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93616CVSS 9.8
    A directory traversal and file upload vulnerability allows an unauthenticated attacker to upload and execute arbitrary scripts on...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-100741CVSS 9.8
    Eval injection in the JScript event-script dispatcher in Progressive Robot Ltd's hMailServer, versions 6.0.0 through 6.3.3 on Windows,...
    📅 Updated: Sep 27, 2026
  • CVE-2026-94130CVSS 9.3
    Joomla Extension - joomlaboat.com - Unauthenticated SQL injection in YouTube Gallery extension < 5.7.3 - An SQL injection...
    📅 Updated: Sep 27, 2026
  • CVE-2026-97161CVSS 9.2
    Joomla Extension - lomart.fr - Various path traversal / file access vectors in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-97163CVSS 10.0
    Joomla Extension - lomart.fr - Unauthenticated remote code installation in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-94132CVSS 9.5
    Joomla Extension - acymailing.com - Remote Code Execution vulnerability in mailbox action feature in AcyMailing Enterprise extension <...
    📅 Updated: Sep 27, 2026
  • CVE-2026-97160CVSS 9.4
    Joomla Extension - lomart.fr - Authenticated, privileged PHP command injection in UP plugin extension 5.0.0-5.2.0, 6.0.0-6.0.29
    📅 Updated: Sep 27, 2026
  • CVE-2026-100835CVSS 9.1
    Contrast before 1.16.0 is susceptible to remote attestation relay attacks. Contrast accepted any TEE attestation report that verified...
    📅 Updated: Sep 27, 2026
  • CVE-2026-100721CVSS 9.5
    vm2 before 3.12.2 contains an authorization bypass in the NodeVM external-module resolver. When an embedder configures `require.external` with...
    📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.