Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
DCHSpy Android Spyware Linked to Iran’s MuddyWater APT, Targets Geopolitical Foes with Starlink Lures Android Spyware, MuddyWater APT
  • Cyber Security
  • Malware

DCHSpy Android Spyware Linked to Iran’s MuddyWater APT, Targets Geopolitical Foes with Starlink Lures

Do Son July 23, 2025 0

Lookout uncovers an evolved DCHSpy Android spyware linked to Iran's MuddyWater APT, targeting high-value geopolitical entities with new Starlink and VPN lures.

AccuKnox Named Top AI Security Startup at Security BSides Bangalore 2025 image1_1753095381Q5ghkaV51r
  • Press Release

AccuKnox Named Top AI Security Startup at Security BSides Bangalore 2025

cybernewswire July 22, 2025 0
Menlo Park, United States, 22nd July 2025, CyberNewsWire
Read More Read more about AccuKnox Named Top AI Security Startup at Security BSides Bangalore 2025
New Report Reveals Just 10% of Employees Drive 73% of Cyber Risk Cyberwire_Image_Cyentia_1753106017AQGHGG6c1J
  • Press Release

New Report Reveals Just 10% of Employees Drive 73% of Cyber Risk

cybernewswire July 22, 2025 0
Austin, United States / TX, 22nd July 2025, CyberNewsWire
Read More Read more about New Report Reveals Just 10% of Employees Drive 73% of Cyber Risk
Urgent: Cisco ISE Flaws (CVSS 10.0) Actively Exploited in the Wild – Patch Immediately! Cisco ISE Exploitation
  • Vulnerability Report

Urgent: Cisco ISE Flaws (CVSS 10.0) Actively Exploited in the Wild – Patch Immediately!

Do Son July 22, 2025 0

Cisco warns of active exploitation for three critical ISE flaws (CVSS 10.0), allowing unauthenticated RCE and full system control. Update ISE 3.3 and 3.4 immediately!

Firefox 141 Arrives: AI Tab Grouping, Linux Memory Boosts, and WebGPU on Windows Firefox 32-bit Linux Firefox, CRLite Firefox 141, AI Tab Groups Firefox Focus Android
  • Technology

Firefox 141 Arrives: AI Tab Grouping, Linux Memory Boosts, and WebGPU on Windows

Do Son July 22, 2025 0

Firefox v141.0 rolls out with new AI-powered tab grouping that keeps your data local, significant memory optimizations for Linux, and WebGPU support for Windows users.

GitHub Now Supports Google Social Login: Streamlined Sign-in for Developers GitHub Social Login, Google Integration
  • Technology

GitHub Now Supports Google Social Login: Streamlined Sign-in for Developers

Do Son July 22, 2025 0

GitHub now allows users to sign in and create new accounts using their Google credentials, offering a streamlined login experience for developers.

Critical Kubernetes Image Builder Flaw: Default Credentials Grant Root Access to Windows Nodes Ingress-Nginx Vulnerability Kubernetes RCE Vulnerability CVE-2025-9708 Kubernetes Security, Image Builder Vulnerability CVE-2024-10220 - OPA Gatekeeper Bypass
  • Vulnerability

Critical Kubernetes Image Builder Flaw: Default Credentials Grant Root Access to Windows Nodes

Do Son July 22, 2025 0

Kubernetes warns of CVE-2025-7342 (CVSS 8.1) in Image Builder. Default credentials in Windows VM images (Nutanix/OVA) allow unauthenticated root access to clusters. Patch immediately!

UK Forges Strategic AI Alliance with OpenAI to Boost Infrastructure and Safety Research ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

UK Forges Strategic AI Alliance with OpenAI to Boost Infrastructure and Safety Research

Do Son July 22, 2025 0

The UK government has signed an MoU with OpenAI, focusing on AI infrastructure, safety research, and public sector integration to accelerate its national AI agenda.

Chrome for iOS Levels Up: New Features Enhance Data Separation for Work and Personal Accounts Chrome iOS, Enterprise Features
  • Technology

Chrome for iOS Levels Up: New Features Enhance Data Separation for Work and Personal Accounts

Do Son July 22, 2025 0

Chrome for iOS now offers enhanced data separation for work and personal Google accounts, alongside new Enterprise controls like URL filtering and audit log streaming for IT.

ChatGPT Now Handles 2.5 Billion Requests Daily, Challenging Google’s Search Dominance AI Empire, Sam Altman OpenAI Government, AI Procurement ChatGPT Usage, AI Growth ChatGPT Enterprise, AI Business Tools ChatGPT Free ChatGPT Memory AI Personalization
  • Technology

ChatGPT Now Handles 2.5 Billion Requests Daily, Challenging Google’s Search Dominance

Do Son July 22, 2025 0

OpenAI's ChatGPT now processes 2.5 billion requests daily, with 330 million from the US. This surge signals a rapid shift in AI adoption, challenging traditional search engines like Google.

Google Teases Pixel 10 Design on Store Page: New Colors, Telephoto Lens for Standard Model Pixel Switch 2 Webcam Google UVC Fix Pixel 10, Google Store Teaser
  • Android

Google Teases Pixel 10 Design on Store Page: New Colors, Telephoto Lens for Standard Model

Do Son July 22, 2025 0

Google's own store page subtly revealed the Pixel 10 design, showing a new color, a refined camera module with a telephoto lens, and hinting at a TSMC-made Tensor chip.

Microsoft 365 UWP App is Dying: Move to Click-to-Run Before October 2025 EOL student discount Microsoft 365, Intelligent Services Microsoft 365 UWP, App Deprecation Microsoft 365, Startup Boost Windows 10 EOL, Microsoft 365 Support Protocol Deprecation Microsoft 365 Updates, IT Admin Alert Microsoft 365 VPN shut down Microsoft Authenticator, password manager Windows 10 Microsoft 365 Microsoft nonprofit policy, software donations
  • Technology

Microsoft 365 UWP App is Dying: Move to Click-to-Run Before October 2025 EOL

Do Son July 22, 2025 0

Microsoft is deprecating its UWP-based Microsoft 365 app. Functional updates end Oct 2025, security updates Dec 2026. Users must switch to Click-to-Run for continued support.

Xbox Unleashes “Cross-Device Play History”: Seamless Cloud Gaming Across All Your Devices Xbox Cloud Gaming, Cross-Device Play History
  • Technology

Xbox Unleashes “Cross-Device Play History”: Seamless Cloud Gaming Across All Your Devices

Do Son July 22, 2025 0

Xbox introduces "Cross-Device Play History" for Insiders, harmonizing gameplay across Xbox and Windows via cloud sync for a seamless, consistent gaming experience.

India’s Chip Ambition: First “Made in India” Semiconductor & 6 New Fabs by 2025 India Semiconductors, Chip Manufacturing Linux Malware Campaign
  • Technology

India’s Chip Ambition: First “Made in India” Semiconductor & 6 New Fabs by 2025

Do Son July 22, 2025 0

India aims to launch its first "Made in India" chip and open six fabs by late 2025 to boost domestic semiconductor manufacturing and reduce 90% import reliance.

Corning Avoids Massive EU Fine by Ending Exclusive Smartphone Glass Deals Apple Google EU alliance DMA European Commission Breach Trivy Supply Chain Attack Europa.eu Breach EU Cloud Infrastructure EU Cyber Sanctions State-Sponsored Hacking EU 2040 Emissions Target, Europe Climate Leadership AWS Azure DMA Cloud Gatekeeper DSA violation, illegal content Apple DMA Delay, iPhone Mirroring EU EU Age Verification, Google Play Integrity Corning Antitrust, EU Competition Apple EU Digital Markets Act App Store commission European Union cyberattacks - InvestAI EU Targets Musk’s X Digital Markets Act, EU fines
  • Technology

Corning Avoids Massive EU Fine by Ending Exclusive Smartphone Glass Deals

Do Son July 22, 2025 0

Corning has settled an EU antitrust probe, agreeing to terminate exclusive supply deals for smartphone glass and avoid a substantial fine, ensuring fair competition.

Urgent Sophos Firewall Update: Two Critical RCE Flaws (CVE-2025-6704, CVE-2025-7624) Patched via Hotfixes Sophos Firewall, Remote Code Execution
  • Vulnerability Report

Urgent Sophos Firewall Update: Two Critical RCE Flaws (CVE-2025-6704, CVE-2025-7624) Patched via Hotfixes

Do Son July 22, 2025 0

Sophos patched five flaws in Sophos Firewall, including two critical RCEs (CVE-2025-6704, CVE-2025-7624) allowing remote attackers to take control under specific conditions.

Critical Flaw (CVE-2025-24936, CVSS 9.0) in Nokia WaveSuite NOC Expose Telecom Networks to RCE Nokia WaveSuite, Command Injection
  • Vulnerability Report

Critical Flaw (CVE-2025-24936, CVSS 9.0) in Nokia WaveSuite NOC Expose Telecom Networks to RCE

Do Son July 22, 2025 0

Nokia's WaveSuite NOC platform has two severe command injection vulnerabilities (CVE-2025-24938, CVE-2025-24936) allowing remote code execution, even with low privileges.

Greedy Sponge Reemerges: New AllaKore RAT Variant and SystemBC Target Mexico’s Financial Sector Greedy Sponge, AllaKore RAT
  • Cybercriminals

Greedy Sponge Reemerges: New AllaKore RAT Variant and SystemBC Target Mexico’s Financial Sector

Do Son July 22, 2025 0

Greedy Sponge, a financially motivated group, is back with an upgraded AllaKore RAT and SystemBC, targeting Mexican organizations for banking credentials and financial fraud.

Android Malware Strikes: Fake Facebook & TikTok Apps Impersonate Brands for Traffic Monetization BadBox 2.0, Android Botnet Alien spyware - CVE-2024-43093
  • Malware

Android Malware Strikes: Fake Facebook & TikTok Apps Impersonate Brands for Traffic Monetization

Do Son July 22, 2025 0

Trustwave uncovers an Android malware cluster using fake Facebook & TikTok apps to lure victims via brand impersonation, abusing permissions for data collection and traffic monetization.
NailaoLocker Ransomware: Chinese SM2 Crypto and Built-in Decryptor Raise Questions NailaoLocker, SM2 Ransomware
  • Malware

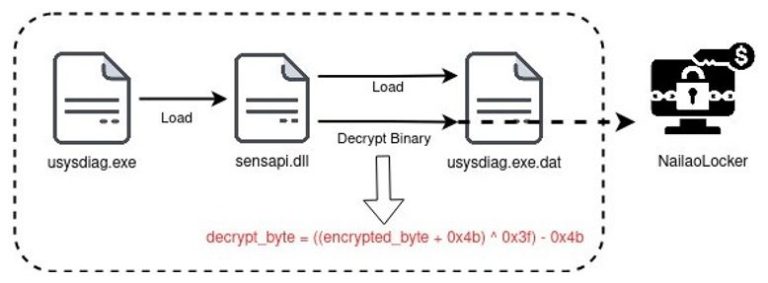
NailaoLocker Ransomware: Chinese SM2 Crypto and Built-in Decryptor Raise Questions

Do Son July 22, 2025 0

FortiGuard Labs unveils NailaoLocker, a new ransomware using Chinese SM2 encryption and a built-in, non-functional decryptor, suggesting a prototype or decoy.

Important wolfSSL Update: Critical Apple Trust Store Bypass & Predictable Randomness Flaws Patched wolfSSL Vulnerabilities, TLS/SSL Security
  • Vulnerability Report

Important wolfSSL Update: Critical Apple Trust Store Bypass & Predictable Randomness Flaws Patched

Do Son July 22, 2025 0

wolfSSL 5.8.2 patches four vulnerabilities, including a critical Apple trust store bypass (CVE-2025-7395) and predictable randomness after fork(), impacting secure communications.

From MDifyLoader to Fscan: JPCERT Uncovers Deep Exploitation of Ivanti VPN Flaws in Advanced Malware Campaign Ivanti Exploitation, Multi-Malware Campaign
  • Vulnerability Report

From MDifyLoader to Fscan: JPCERT Uncovers Deep Exploitation of Ivanti VPN Flaws in Advanced Malware Campaign

Do Son July 22, 2025 0

JPCERT/CC details a sophisticated, ongoing malware campaign exploiting Ivanti Connect Secure (CVE-2025-0282, -22457) using MDifyLoader, Cobalt Strike, vshell, and Fscan for stealthy persistent access.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17150CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17239CVSS 9.9
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.