
 Do Son
While continuing to shape Copilot into its flagship AI service, Microsoft has announced the launch of two...
Latest news

Massachusetts-based nuclear fusion startup Commonwealth Fusion Systems (CFS) has announced the completion of a new $863 million...

Following the release of the Llama 4 series of AI models this April, Meta’s trajectory in the...

Microsoft continues to enhance the Xbox Cloud Gaming experience. Following earlier trials under the updated Xbox Insiders...

IBM has released a security advisory warning of a SQL injection vulnerability affecting its watsonx Orchestrate Cartridge...

The Plone Zope Security Team has released an advisory addressing a denial-of-service (DoS) vulnerability in Volto, the...
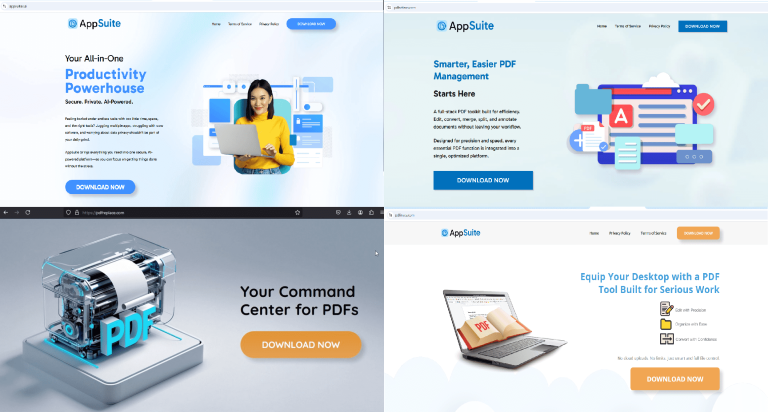
Security researchers at G DATA Security Lab have exposed the AppSuite PDF Editor as a malware-laden backdoor,...

Why ChatGPT Turned Into an AI Tutor Students Actually Use ChatGPT has moved far beyond being a...

Bitdefender Labs has issued a new warning about a global malvertising campaign abusing Meta’s advertising system to...

At DEF CON 2025, Akamai security researcher Yuval Gordon revealed the story of BadSuccessor (CVE-2025-53779), an Active...

One of your goals is to keep customers happy when you’re an insurance company. However, the competition...

Licensing essentially refers to an agreement that licensees must comply with to use specific products. Various items...

CVE-2022-37021 is the "deserialization of untrusted data flaw when using JMX over RMI on Java 8," and affects Apache Geode versions

Tracked as CVE-2022-2992 (CVSS 9.9/10 severity), the security flaw can be exploited via the Import from GitHub API endpoint

For each article that states a golden marketing rule, you’ll see another article disapproving of that theory...

Twilio disclosed that the threat actors managed to gain access to the accounts of 93 individual users of its Authy two-factor authentication service.

If you are interested in cybersecurity, you have definitely heard of Zero Trust and SASE, as they...

Linux kernel is affected by a potentially serious flaw (CVE-2022-2961) that can be exploited by attackers to grant elevated privileges

If you want to build an Android app, the assistance of Android SDK is essential. Let’s look at how to get started with these tools and install Android SDK on macOS and Windows.
Learn how to discover the best online coding courses and resources that can help your kids learn web development and become future-ready.
A transportation management system (TMS) is a software application designed to streamline the process of shipping goods...

By sending a specially crafted request, an attacker could exploit the CVE-2022-25625 flaw to gain elevated privileges on the affected system.

When you apply for a credit card, the bank will offer you a credit limit based on...
Crypto cards are different from traditional credit cards in a number of ways. They’re usually issued by...

Trading stocks online is a great way to build your wealth and diversify your portfolio. It’s also...

CVE-2022-38556 can allow an unauthenticated, remote attacker to take full control of the device to take control vulnerable devices

The buffer overflow security vulnerability, tracked as CVE-2022-38555, is related to the ej_get_web_page_name function

CVE-2022-38557 credential flaw exists in the Telnet service of D-Link DAP1522. The expert has published detailed technical information

Every day we collect more and more data on our cell phones. Therefore, it is essential to...

an attacker could exploit this vulnerability to execute arbitrary commands as a YARN user on the system, track as CVE-2021-25642

Stellar Repair for Exchange is the right tool to recover and retrieve data from any version of...

The investigation revealed that only part of the LastPass source code and part of some proprietary technical documents were stolen