 Do Son
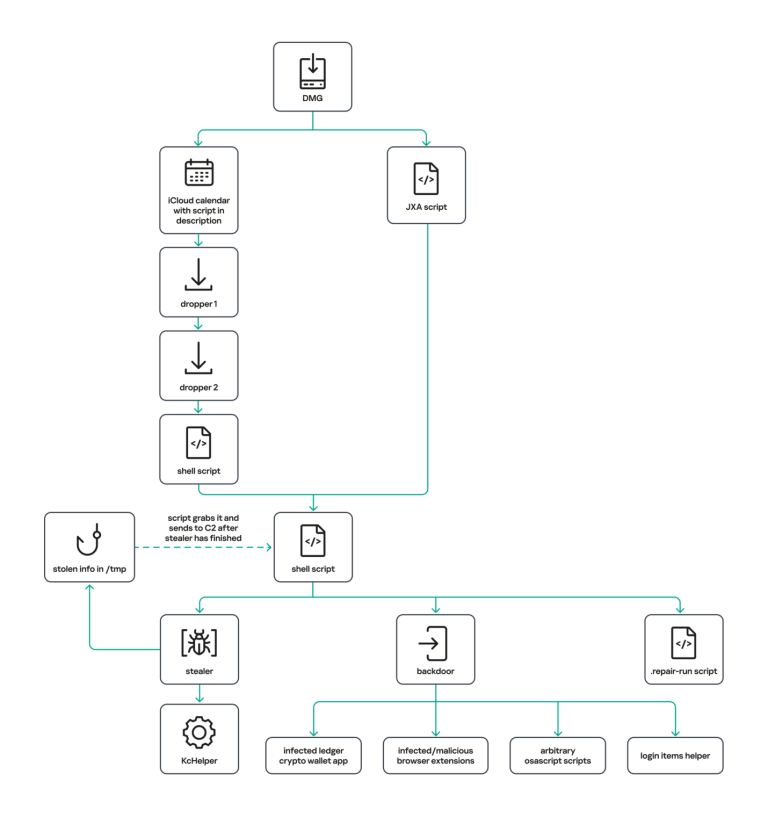
A new MacSync macOS infostealer spreads via fake apps. Learn how the MacSync macOS infostealer abuses iCloud to compromise Apple systems.
macOS Malware
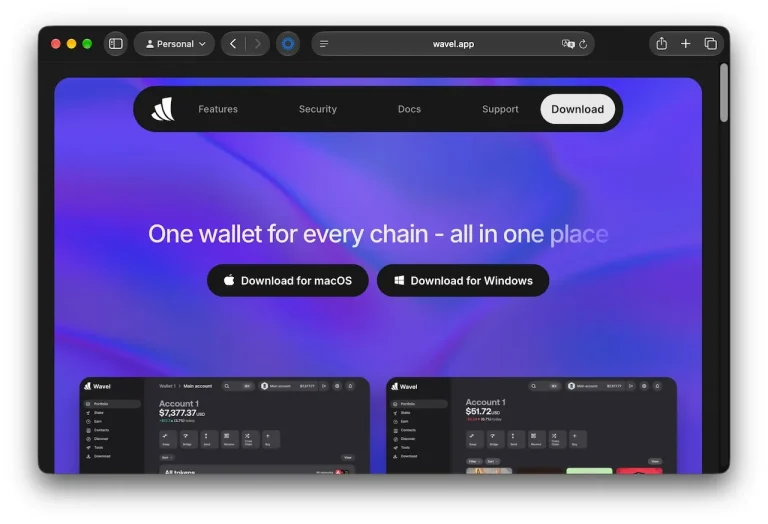
A new PamStealer macOS infostealer spreads via fake Wavel apps. Learn how the PamStealer macOS infostealer steals system passwords and browser data.

SentinelOne discovered how new TraderTraitor macOS backdoors hit IT firms. Learn how TraderTraitor macOS backdoors use weaponized Terraform files.
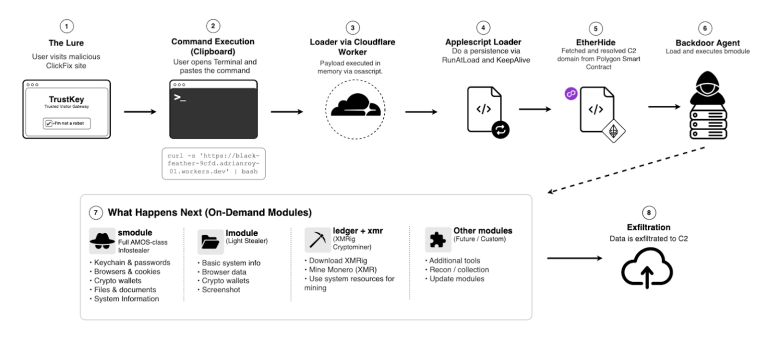
A new macOS ClickFix malware campaign hides C2 servers on the blockchain. See how this macOS ClickFix malware steals crypto wallets and credentials.

Jamf Threat Labs has discovered a new AmnesiaStealer macOS infostealer malware. The AmnesiaStealer macOS infostealer steals data and hijacks browsers.

A fake Zoom installer delivers Overlord RAT on macOS via a .NET downloader. Jamf Threat Labs details the infection chain and defenses.

XCSSET v40 malware infects macOS developers through poisoned Xcode projects on GitHub, then hides in memory. Unit 42 found 17 modules and Chrome hijacking.

ClickLock Stealer is macOS malware that freezes your Mac until you type your password. Group-IB found 100+ victims across 33 countries.

CrashStealer is a native C++ macOS infostealer posing as Apple's crash reporter. Jamf details its notarized dropper, AES-GCM theft, and persistence.
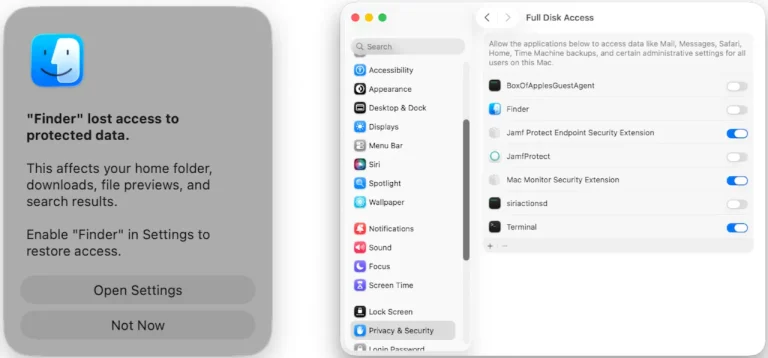
PamStealer macOS malware hides in a fake Maccy app and drops a Rust infostealer that checks your password via PAM before stealing it.

A dangerous macOS cryptocurrency malware wave drives the latest JINX-0164 developer campaign. Learn how to secure your repositories now.
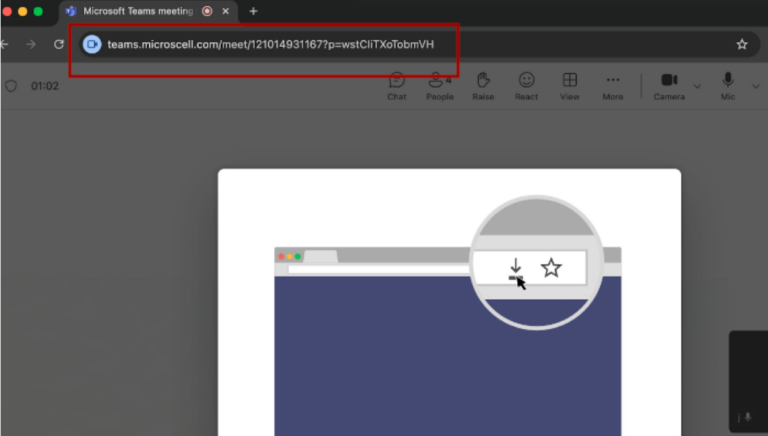
North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!

Attackers are impersonating Linux leaders on Slack to drop malware via fake Google Workspace links. Protect your dev environment—verify before acting!
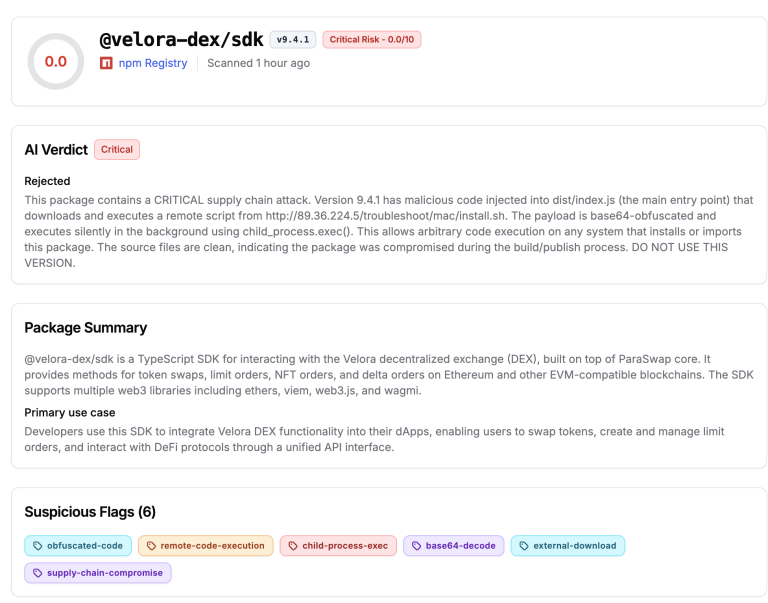
A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.

Jamf Threat Labs uncovers GhostClaw, a macOS threat exploiting GitHub stars and AI workflows to steal credentials. Protect your dev environment today!

Security researchers uncover a massive macOS malware campaign using "cracked" audio plugins and "ClickFix" tactics to deliver Odyssey and MacSyncStealer.
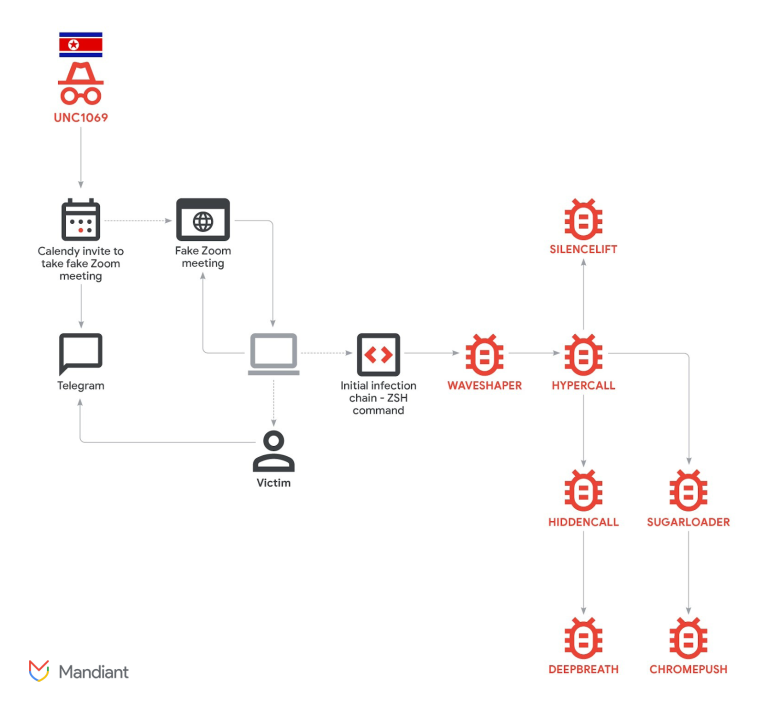
North Korean hackers (UNC1069) use AI deepfakes & "ClickFix" tactics to deploy SILENCELIFT malware. Learn how they target crypto firms via Zoom.

Darktrace finds Mac malware using a fake "Compatibility Wizard" to trick users. The AppleScript attack bypasses TCC to drop a Node.js backdoor.
Microsoft warns: Infostealers now target macOS & use WhatsApp worms. "Eternidade" & "Crystal PDF" steal credentials via cross-platform attacks.

New macOS malware "MacSync" uses fake cloud installers & "ClickFix" terminal commands to steal crypto. It bypasses Gatekeeper to trojanize wallet apps.

New macOS malware "MonetaStealer" disguises itself as a Windows .exe to steal crypto & Keychain data. It currently has zero VirusTotal detection.

North Korea's "Contagious Interview" campaign uses DriverFixer0428 to steal macOS credentials via fake prompts and Dropbox C2. Stay alert!