
 Do Son
A critical flaw (CVE-2025-4517, CVSS 9.4) in Python's tarfile module allows arbitrary file reads/writes outside the extraction directory. PoC is public; update immediately
Python

Banana Squad has compromised over 60 GitHub repos with malicious Python files, using UI quirks to hide malware and steal data from developers via a sophisticated supply chain attack.

A high-severity flaw (CVE-2025-4565) in Google's pure-Python Protobuf backend allows unauthenticated attackers to crash applications via crafted nested messages.

Critical and high-severity flaws in Python's tarfile module allow arbitrary filesystem writes and bypasses. Update to the latest patched version immediately.

A sophisticated PyPI supply chain attack, "cappership," steals Solana private keys by monkey-patching, leveraging transitive dependencies and blockchain exfiltration.

Critical vulnerabilities (CVSS 9.8) in the Langroid Python framework allow remote code execution in LLM applications. Update to version 0.53.15 now!

A high-severity path traversal flaw in setuptools can allow RCE, exposing millions of Python users. Update to 78.1.1 now.

Tornado is vulnerable to DoS attacks due to its default parser. Details on CVE-2025-47287 and how to mitigate the high-severity threat.

Discover a serious Reflex Python framework vulnerability and how to fix it. Learn about the CVE-2025-47425 flaw and secure your web applications.

Socket discovers Python packages abusing Gmail SMTP for covert C2 tunnels, evading firewalls and exfiltrating data through trusted email infrastructure.

Cyfirma uncovers a Python-based RAT using Discord for command and control. It can lock screens, simulate BSOD, move the mouse, and steal data.
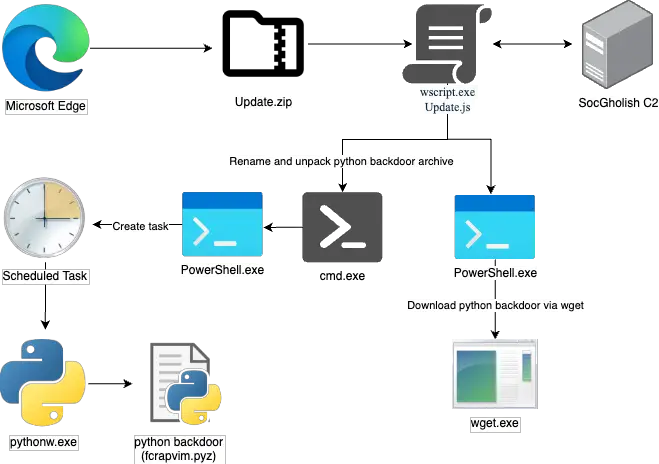
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.

A CVE-2025-43859 vulnerability in Python’s h11 library may lead to request smuggling attacks when paired with buggy proxies. Patch to version 0.15.0 now.

PyPI resolved a security issue on April 14, 2025, where users retained team privileges after organization removal. The swift 2-hour fix prevented potential escalation.

Learn about AkiraBot, an AI-powered spam bot that uses OpenAI to generate personalized messages and flood website contact forms and chat widgets, as detailed in a SentinelLABS report.

Learn about CVE-2025-29783, a critical vulnerability in vLLM affecting LLM deployments and remote code execution risks.
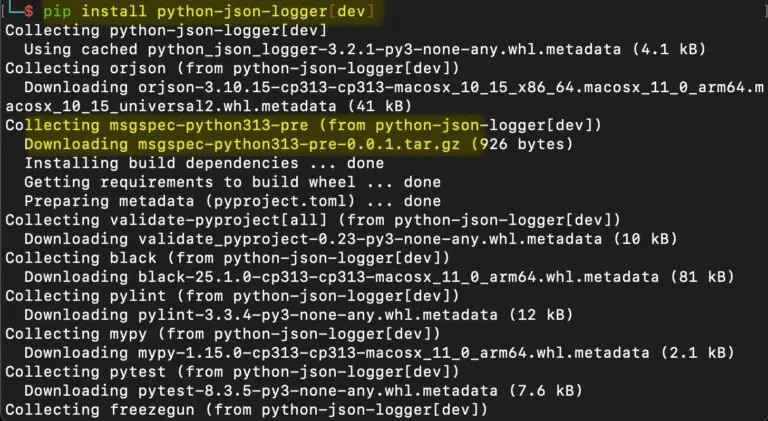
Understand the implications of CVE-2025-27607. Attackers could exploit the python-json-logger vulnerability for remote code execution.

Learn about the ISP Infostealer Campaign and its severe impacts on ISP infrastructure through brute force and data exfiltration.

Uncover the GitVenom campaign targeting GitHub users with malicious repositories designed to steal credentials and cryptocurrency.

Stay informed about the critical RCE vulnerability (CVE-2025-1077) affecting IBL Software Engineering's Visual Weather and derived products. Learn how to protect your servers.

Discover the latest campaign spreading the AsyncRAT malware. Learn how cybercriminals are utilizing trusted infrastructure to evade detection.

Discover the latest cyber threat: RedCurl APT group. Learn about their sophisticated techniques and targeted cyber espionage campaigns.