Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Reversed Phishing Attack: New Campaign Triggers Victims to Call Hackers NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Cybercriminals

The Reversed Phishing Attack: New Campaign Triggers Victims to Call Hackers

Do Son August 28, 2025 0

A new phishing campaign called ZipLine reverses the attack by tricking victims into initiating contact. It targets supply chains and deploys a custom in-memory implant.

NVIDIA Warns of a High-Severity Flaw in NeMo AI Curator (CVE-2025-23307) NeMo Curator, NVIDIA vulnerability
  • Vulnerability Report

NVIDIA Warns of a High-Severity Flaw in NeMo AI Curator (CVE-2025-23307)

Do Son August 27, 2025 0

NVIDIA has issued a high-severity security update for a flaw (CVE-2025-23307) in NeMo Curator. The vulnerability allows code injection and could compromise AI training pipelines.

A New AI Header: The IETF Is Building a Standard to Label AI-Generated Content Yoshua Bengio AI sycophancy, reverse deception AI feedback AI chatbots, FTC investigation AI-generated content Trump AI Policy, AI Deregulation Military AI, DoD Funding Stargate Project AI Art Restoration
  • Technology

A New AI Header: The IETF Is Building a Standard to Label AI-Generated Content

Do Son August 27, 2025 0

The IETF has proposed a new HTTP header to label AI-generated content. The voluntary "AI-Disclosure" header would help bots and archives filter out low-quality material.

PoC Available: D-Link Router Flaw with CVSS 9.8 and No Patch D-Link EOL RCE, Unauthenticated Command Injection D-Link Command Injection CVE-2025-57105
  • Vulnerability

PoC Available: D-Link Router Flaw with CVSS 9.8 and No Patch

Do Son August 27, 2025 0

A critical command injection flaw (CVE-2025-57105) has been found in D-Link's end-of-life DI-7400G+ router series. Because the devices are unsupported, no patch is coming.

Nx Build System Compromise Targets Developers with AI-Enhanced Supply Chain Attack Nx supply chain attack
  • Cybercriminals

Nx Build System Compromise Targets Developers with AI-Enhanced Supply Chain Attack

Do Son August 27, 2025 0

A supply chain attack on the Nx build system is stealing crypto wallets and SSH keys from developers. The malware also abuses AI tools for data exfiltration.

Apple’s Big AI Gamble: Internal Rift Over Perplexity and Mistral AI Acquisitions Vibe Coding apps Vibe Coding App Store surge Vibe Coding App Store Apple 50th Anniversary hardware Brazil CADE Apple settlement, iOS third-party app stores Brazil Tim Cook Succession Apple CEO Rumors App Store Mini Apps 15% Commission Fee iOS Japan Sideloading, Third-Party App Stores Web App Store, App Discovery Apple Age Verification, Texas SB2420 Apple AI acquisitions App Store, Antitrust Apple WebKit, Japan Regulations App Store Age Ratings, Parental Controls Apple App Store, Epic Games Lawsuit
  • Technology

Apple’s Big AI Gamble: Internal Rift Over Perplexity and Mistral AI Acquisitions

Do Son August 27, 2025 0

Apple is reportedly weighing acquisitions of AI startups Perplexity AI and Mistral AI, a move that highlights a major internal rift over the company's AI strategy.

Windows 10 Gets a Preview Update with Enterprise-Grade Backup & ESU Fixes Windows 10 MSMQ Bug, KB5071546 Write Permissions Windows 10 Lawsuit Windows 10 ESU, Free Security Updates Windows 10 ESU program
  • Windows

Windows 10 Gets a Preview Update with Enterprise-Grade Backup & ESU Fixes

Do Son August 27, 2025 0
Microsoft has released a new preview update, KB5063842, for Windows 10 version 22H2 to address several known...
Read More Read more about Windows 10 Gets a Preview Update with Enterprise-Grade Backup & ESU Fixes
Retail Giant Walmart Selects Broadcom as Strategic Private Cloud Partner VMware Telco Cloud Platform 9 Tesco, Broadcom, VMware Walmart Broadcom Jericho4, Distributed AI Infrastructure Broadcom VMware, Perpetual Licenses AI Data Centers, Network Switch Unix automation security, Broadcom vulnerability
  • Technology

Retail Giant Walmart Selects Broadcom as Strategic Private Cloud Partner

Do Son August 27, 2025 0

Walmart has selected Broadcom's VMware Cloud Foundation to modernize its tech stack. The partnership will enable the retail giant to scale its private cloud and edge computing infrastructure.
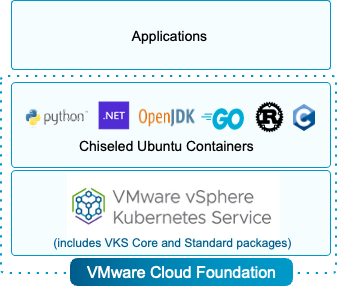
Broadcom & Canonical Join Forces to Supercharge AI and Cloud with Ubuntu Broadcom Canonical
  • Technology

Broadcom & Canonical Join Forces to Supercharge AI and Cloud with Ubuntu

Do Son August 27, 2025 0

Broadcom and Canonical have partnered to integrate Ubuntu into VMware Cloud Foundation, providing streamlined, secure, and efficient AI and cloud-native application deployment.

Gemini’s New AI Image Generation Model Prioritizes Consistency, Control, and Trust AI image generation, Gemini image editing
  • Technology

Gemini’s New AI Image Generation Model Prioritizes Consistency, Control, and Trust

Do Son August 27, 2025 0

Google's new Gemini model brings major upgrades to AI image editing, focusing on character consistency, multi-stage edits, and digital watermarks for transparency.

End of Anonymous Sideloading: Google to Require Developer Verification on Android Sideloading, Android security
  • Android

End of Anonymous Sideloading: Google to Require Developer Verification on Android

Do Son August 27, 2025 0

Google will soon require all sideloaded Android apps to come from a verified developer. The move aims to combat malware, which is 50x more common in unverified apps.

Beyond Compliance: Broadcom’s New Private Cloud Tools Secure AI Workloads Private cloud security, AI security
  • Technology

Beyond Compliance: Broadcom’s New Private Cloud Tools Secure AI Workloads

Do Son August 27, 2025 0

Broadcom has unveiled new security services for VMware Cloud Foundation, focusing on compliance, Zero Trust, and post-quantum cryptography to secure AI workloads.

A New AI Frontier: Claude’s Chrome Extension Opens the Door to New Dangers Anthropic valuation $350 billion AI agent, prompt injection
  • Technology

A New AI Frontier: Claude’s Chrome Extension Opens the Door to New Dangers

Do Son August 27, 2025 0

Anthropic's new Claude AI extension for Chrome allows it to read websites, but the tool also introduces a risk of prompt injection attacks that could lead to data theft.

Awe Dropping: Apple Announces September 9 Event, Teasing a Groundbreaking Design Apple silicon, in-house chips Apple Event, iPhone 17 Air TSMC, 2nm chips
  • Technology

Awe Dropping: Apple Announces September 9 Event, Teasing a Groundbreaking Design

Do Son August 27, 2025 0

Apple has confirmed its "Awe dropping" event for September 9, where it's expected to unveil a new iPhone 17 Air, Apple Watch 11, and AirPods Pro 3.

Google Chrome Patches Critical ANGLE Vulnerability (CVE-2025-9478) Discovered by AI Agent Big Sleep Chrome Security Update Use After Free Chrome Security Update Critical Vulnerabilities Chrome Security Update CVE-2026-3062 Chrome Security Update V8 Engine Vulnerability Chrome Security Update CVE-2026-1862 CVE-2026-0628 Chrome 143 Update Chrome Safe Browsing UAF, CVE-2025-11756 Chrome Memory Flaws, CVE-2025-11460 Google Chrome, vulnerability CVE-2025-10200, CVE-2025-10201 Big Sleep CVE-2025-9478 Chrome Update, Security Vulnerabilities
  • Vulnerability Report

Google Chrome Patches Critical ANGLE Vulnerability (CVE-2025-9478) Discovered by AI Agent Big Sleep

Do Son August 27, 2025 0

A new report reveals that Google's AI agent, Big Sleep, discovered and fixed a critical use-after-free vulnerability (CVE-2025-9478) in Chrome's ANGLE engine.

Hook v3: The Banking Trojan That’s Evolving into a Hybrid Ransomware-Spyware Threat Hook malware, Android trojan
  • Malware

Hook v3: The Banking Trojan That’s Evolving into a Hybrid Ransomware-Spyware Threat

Do Son August 27, 2025 0

A new report reveals the Hook Android trojan has evolved into a hybrid threat with ransomware-style overlays, lockscreen bypasses, and stealthy screen-streaming.

CVE-2025-41702 (CVSS 9.8): Critical Flaw in Welotec egOS Puts Industrial Systems at Risk Welotec Vulnerability CVE-2025-41702
  • Vulnerability Report

CVE-2025-41702 (CVSS 9.8): Critical Flaw in Welotec egOS Puts Industrial Systems at Risk

Do Son August 27, 2025 0

A critical flaw (CVE-2025-41702) in Welotec egOS allows unauthenticated attackers to impersonate administrators, gain full control, and disrupt industrial systems.

Google Threat Intelligence Exposes UNC6384’s Stealthy Espionage Campaign UNC6384, cyber-espionage
  • Cyber Security
  • Malware

Google Threat Intelligence Exposes UNC6384’s Stealthy Espionage Campaign

Do Son August 27, 2025 0

A new Google report reveals a Chinese APT group is hijacking captive portals and disguised plugins to deliver malware for espionage against diplomats in Southeast Asia.

SpyNote’s New Lure: The Stealthy Campaign Using Fake App Stores Android RAT, SpyNote
  • Malware

SpyNote’s New Lure: The Stealthy Campaign Using Fake App Stores

Do Son August 27, 2025 0

A new report reveals a SpyNote Android RAT campaign using fake Google Play Store clones to steal data, with the malware abusing Accessibility Services for control.

Cephalus: The New Ransomware That Abuses Legitimate Tools to Bypass Security Cephalus Ransomware
  • Cybercriminals

Cephalus: The New Ransomware That Abuses Legitimate Tools to Bypass Security

Do Son August 27, 2025 0

A new ransomware strain called Cephalus is using compromised RDP, DLL sideloading, and abused security tools to bypass defenses and intimidate victims.

The Underground Ransomware Gang Is Back with a Vicious New Global Campaign underground
  • Cybercriminals

The Underground Ransomware Gang Is Back with a Vicious New Global Campaign

Do Son August 27, 2025 0

A new report from AhnLab reveals the Underground ransomware gang is back with a global campaign that uses sophisticated multi-layered encryption and customized malware.

Still on Windows 10? Microsoft Is Rolling Out Your Last Chance for Security Updates Windows 10 MSMQ Bug, KB5071546 Write Permissions Windows 10 Lawsuit Windows 10 ESU, Free Security Updates Windows 10 ESU program
  • Windows

Still on Windows 10? Microsoft Is Rolling Out Your Last Chance for Security Updates

Do Son August 27, 2025 0
Microsoft has now opened registration for the Extended Security Updates (ESU) program to Windows 10 Home users....
Read More Read more about Still on Windows 10? Microsoft Is Rolling Out Your Last Chance for Security Updates
❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-112346CVSS 9.3
    OpenHands Software Agent SDK before 1.52.0 contains an unauthenticated remote code execution vulnerability where the DockerWorkspace and Apptainer...
    📅 Updated: Nov 8, 2026
  • CVE-2026-10042CVSS 9.2
    manga-image-translator contains a remote code execution vulnerability in the shared API server mode due to unsafe deserialization of...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71325CVSS 9.3
    picklescan before 0.0.27 contains a parsing logic error in the _list_globals function when handling STACK_GLOBAL opcodes, failing to...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71323CVSS 9.3
    picklescan before 0.0.33 fails to block the ctypes module, allowing attackers to achieve remote code execution by invoking...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71320CVSS 9.3
    picklescan before 0.0.33 contains an incomplete deny-list that fails to block pydoc.locate and operator.methodcaller functions, allowing attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2025-71321CVSS 9.3
    picklescan before 0.0.33 contains an arbitrary file writing vulnerability that allows attackers to bypass the dangerous blocklist by...
    📅 Updated: Nov 8, 2026
  • CVE-2024-58351CVSS 9.3
    Flowise before 2.1.4 allows configuration to be injected into the Chainflow during execution via the overrideConfig option, supported...
    📅 Updated: Nov 8, 2026
  • CVE-2020-37282CVSS 9.3
    office-converter through 1.0.2 contains an OS command injection vulnerability that allows attackers to execute commands by supplying a...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.