Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Cyber Security
  • Dark web marketplace RaidForums shuts down
  • Cyber Security

Dark web marketplace RaidForums shuts down

Do Son April 12, 2022 2 minutes read
RaidForums shuts down
Add Daily CyberSecurity as a preferred source on Google

According to the news released by the U.S. Department of Justice on April 12, the international law enforcement operation TOURNIQUET, led by the United States, coordinated by the Europol-European Cybercrime Center, and jointly participated by law enforcement agencies of the United Kingdom, Sweden, Portugal, and Romania, recently, the illegal Dark web marketplace RaidForums shuts down, and related infrastructure assets were confiscated.
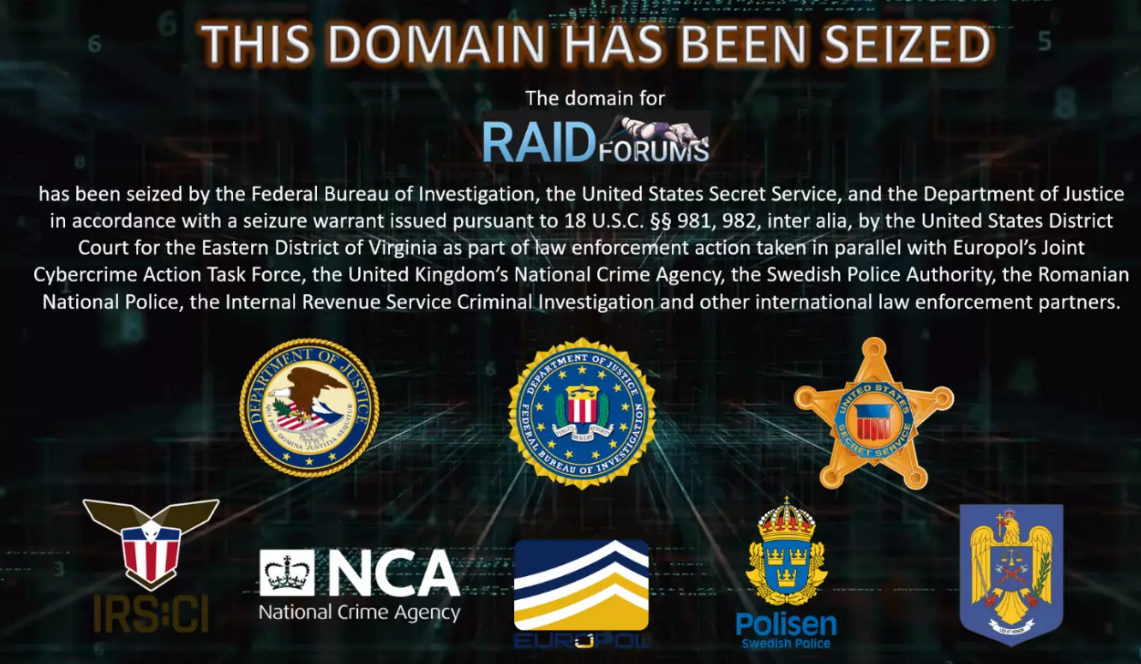
During the operation, law enforcement arrested three suspects, including the founder and CEO of RaidForums, Diogo Santos Coelho, a 21-year-old Portuguese national. Police arrested Coelho in the U.K. on January 31 on criminal charges brought by the U.S.

RaidForums was founded in 2015 and has more than 500,000 community users. It has long targeted companies in various industries in the United States and sold the stolen data, including information on millions of credit cards, bank accounts, and routing information, as well as usernames and related passwords for a large number of online accounts.

“This marketplace had made a name for itself by selling access to high-profile database leaks belonging to a number of US corporations across different industries. These contained information for millions of credit cards, bank account numbers and routing information, and the usernames and associated passwords needed to access online accounts.” reads the announcement published by Europol. “These datasets were obtained from data breaches and other exploits carried out in recent years.”

In order to profit from the platform, under the operation strategy of Coelho, RaidForums also conducts membership business internally and obtains the corresponding membership level by paying different fees to obtain the corresponding access rights and functions, if you want to “unlock” some high-value stolen information, the user must become a higher-level member by recharging. Members can also earn points in other ways, such as posting action tutorials related to illegal behavior.

According to Europol, joint efforts and close information sharing were keys to the success of Operation TOURNIQUET, allowing investigators to determine the structure of RaidForums and the roles and responsibilities of the members behind them. In the future, Europol will continue to work with other countries to combat cybercrime.

Related coverage

  • Data of 478,000 RaidForums members leaked online
  • Phishing Campaigns Exploit YouTube URLs and Microsoft 365 Themes to Steal Credentials
  • WazirX Faces Backlash Over Socialized Losses from $230M Cyberattack
  • APT41 Uses Google Calendar as Covert C2 in Stealthy Cyberespionage Campaign
  • From Confluence Vulnerability (CVE-2023-22527) to LockBit Encryption: A Rapid Attack Chain
  • Microsoft reveals some details of the Russian hacking group’s attack on Ukraine
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: RaidForums RaidForums shuts down

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-119597CVSS 9.3
    OpenDeepWiki through 2.0.6 contains a hard-coded JWT signing key vulnerability that allows unauthenticated attackers to forge administrator tokens...
    📅 Updated: Oct 30, 2026
  • CVE-2026-86413CVSS 9.1
    When using an *ambient user* in a first transfer doing Negotiate authentication and asked to follow redirects, curl...
    📅 Updated: Oct 30, 2026
  • CVE-2026-86414CVSS 9.1
    An HTTP proxy can trick libcurl into sending the origin's credentials (Basic password, or a Negotiate/Kerberos ticket) to...
    📅 Updated: Oct 30, 2026
  • CVE-2026-87861CVSS 9.1
    When using ambient user credentials, an HTTP request directed to one origin may be dispatched over a connection...
    📅 Updated: Oct 30, 2026
  • CVE-2026-119568CVSS 9.1
    vsftpd through 3.0.5 contains an authentication bypass vulnerability in ssl_data_accept() that allows unauthenticated attackers to hijack FTPS data...
    📅 Updated: Oct 30, 2026
  • CVE-2026-119418CVSS 9.2
    CakePHP through 5.4.3 contains an sql injection vulnerability that allows attackers to inject SQL by supplying unvalidated frame...
    📅 Updated: Oct 30, 2026
  • CVE-2026-119419CVSS 9.2
    CakePHP through 5.4.3 contains an sql injection vulnerability that allows attackers to inject SQL by supplying unvalidated collation...
    📅 Updated: Oct 30, 2026
  • CVE-2025-31704CVSS 9.8
    A vulnerability has been found in the Dahua Intelligent Connection Center. A remote attacker could send a specially...
    📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.