
 Do Son
Explore how the Operation RapidRust APT36 malware campaign by Zscaler ThreatLabz exposes new tools like RUSTYSHADE and RUSTYMOVE targeting governments.
APT36

Acronis ties a new PATCHCORD malware APT36 campaign to Afghan telecom and Indian targets. SHEETCORD malware abuses Google Sheets for C2.

Operation ShadowRecruit targets Indian job seekers with SheetAgent RAT, abusing ControlR and Google Sheets for C2. Seqrite links it to APT36.
SHEETCREEP malware is a C# Google Sheets RAT tied to APT36. It hides command-and-control inside Google Sheets to evade network detection.
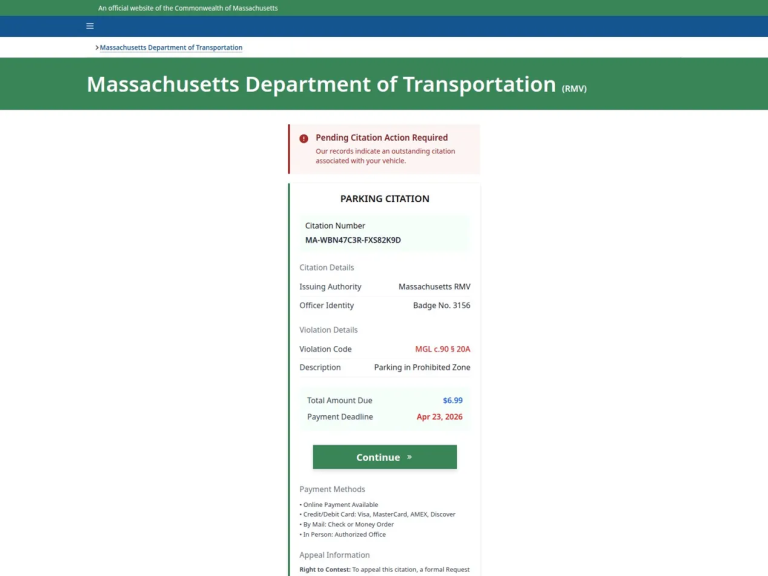
Cyble uncovers "Operation Trust Trap," a 16,800-domain network weaponizing *.gov trust to steal credentials. See how APT36 and others hijack the human eye.

CYFIRMA reveals a new cyber espionage campaign by Transparent Tribe (APT36) targeting Indian defense with stealthy multi-stage malware and decoy PDFs.

Pakistan-linked spies target India with "Sheet Attack," using Google Sheets for C2 and GenAI to build malware. Learn about SHEETCREEP and FIREPOWER.

New "Gopher Strike" & "Sheet Attack" campaigns hit Indian govt. Linked to Pakistan, attackers use GitHub C2 & GenAI malware to evade detection.
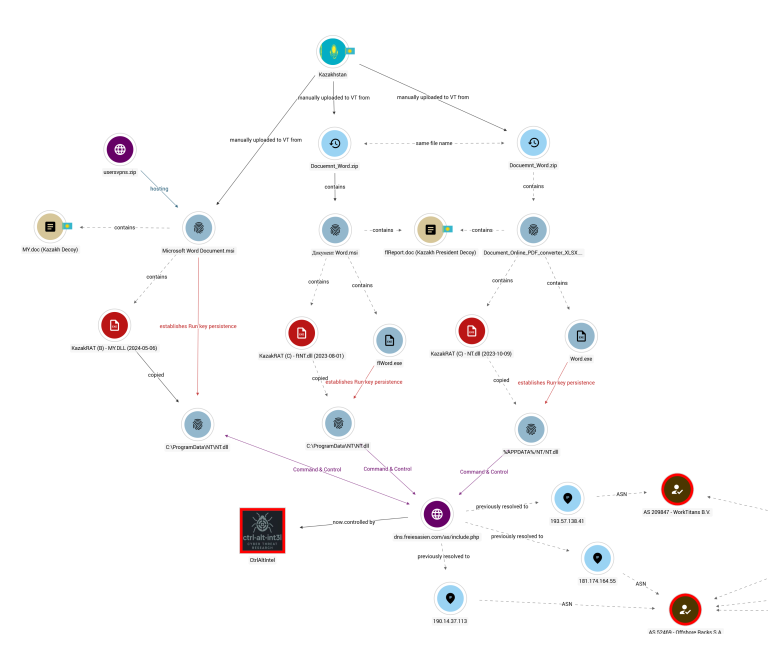
Researchers uncover "KazakRAT," a state-affiliated spyware targeting Kazakhstan & Afghanistan. A lapsed domain allowed experts to sinkhole the C2.
CYFIRMA unmasks APT36's latest campaign: a fake JLPT exam lure using fileless LNK malware to evade antivirus and spy on Indian government targets.

Transparent Tribe (APT36) evolves with new Linux malware targeting Indian government BOSS systems via weaponized shortcut files.

Sekoia exposed TransparentTribe (Pakistan-linked APT) targeting Indian government with AI-assisted DeskRAT malware. The Golang RAT infects BOSS Linux via malicious .desktop files and staging servers.

A new report reveals that the Pakistan-linked APT36 is now targeting Indian government and defense entities with Linux-specific malware delivered via Google Drive.

A new report reveals that the Pakistan-based APT36 is targeting Indian government entities using spear-phishing and Linux-specific malware to steal sensitive data.
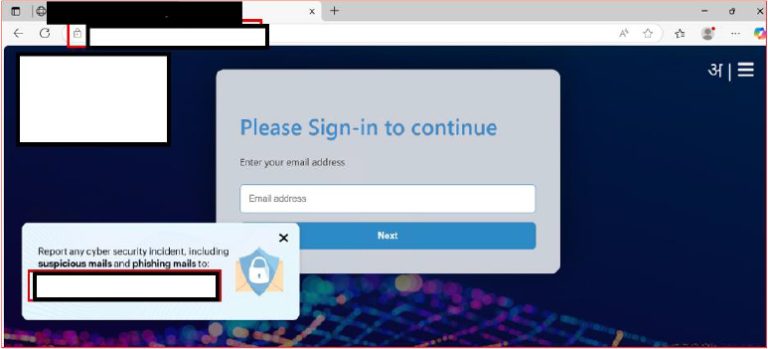
APT36, a Pakistan-linked threat actor, is targeting Indian government officials with phishing campaigns that mimic official websites to harvest credentials and Kavach MFA OTPs in real time.

A new report reveals APT36 (Transparent Tribe) is escalating cyber-espionage against India, using phishing and .desktop files to deploy the Poseidon backdoor for long-term access.
APT36 (Transparent Tribe) is now targeting Indian government agencies via BOSS Linux with spear-phishing. It uses malicious .desktop files to deploy Go-based malware for espionage.

APT36 is targeting Indian defense personnel with sophisticated phishing, using fake NIC documents and multi-layered malware to steal sensitive data and evade analysis.
A sophisticated phishing campaign, possibly by APT36, spoofs Indian government sites and uses ClickFix tactics to target Windows and Linux users.

Uncover the latest findings on a Pakistan-Linked APT targeting Indian users with sophisticated malware distribution tactics.

Learn about the evolution of ElizaRAT and how APT36 has refined its malware to target high-profile entities in India.
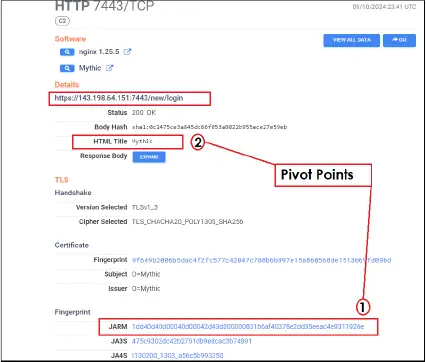
Uncover the activities of Transparent Tribe APT group and their new tactics of espionage. Learn how they target Indian government officials and defense sectors.