 Do Son
Exim 4.100.1 patches a serious Exim vulnerability set: Proxy Protocol heap flaws, a GnuTLS use-after-free, and SMTP smuggling (CVE-2026-94054). Upgrade now.
Exim
A new Exim vulnerability lets a local attacker escape the spool directory and escalate privileges. Upgrade to Exim 4.99.5 to close the hole now.
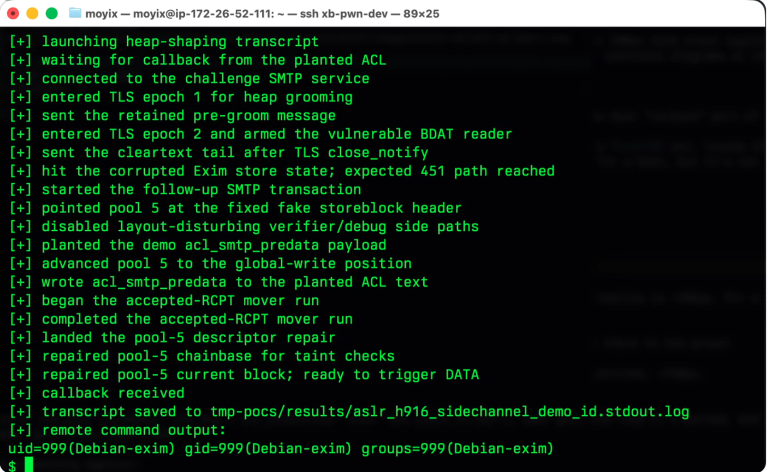
Urgent: Exim fixes a 9.8 severity RCE (CVE-2026-45185) affecting GnuTLS builds. A single-byte heap corruption allows for server takeover. Update to 4.99.3 now!

NIST warns of a critical Exim 4.99 flaw. A failed SQLi patch allows attackers to poison SQLite records and trigger a 1.5MB heap buffer overflow.
Understand the critical security issues related to CVE 2025-30232 in Exim and how it can affect Unix systems.
Learn about CVE-2025-26794, a new vulnerability in Exim that allows remote SQL injection attacks on specific configurations.

A new attack technique named SMTP Smuggling has emerged, threatening the integrity of email communication worldwide.
With a towering CVSS score of 9.8, the CVE-2023-42115 vulnerability unveils a gateway for remote attackers to embed arbitrary codes
The flaw tracked as CVE-2022-37452, classified as critical, is a heap-based buffer overflow for the alias list in host_name_lookup