Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Malware
  • Kaspersky Lab found Calisto malware, a Precursor to Dangerous Proton macOS Malware
  • Malware

Kaspersky Lab found Calisto malware, a Precursor to Dangerous Proton macOS Malware

Do Son July 22, 2018 3 minutes read
Calisto malware
Add Daily CyberSecurity as a preferred source on Google
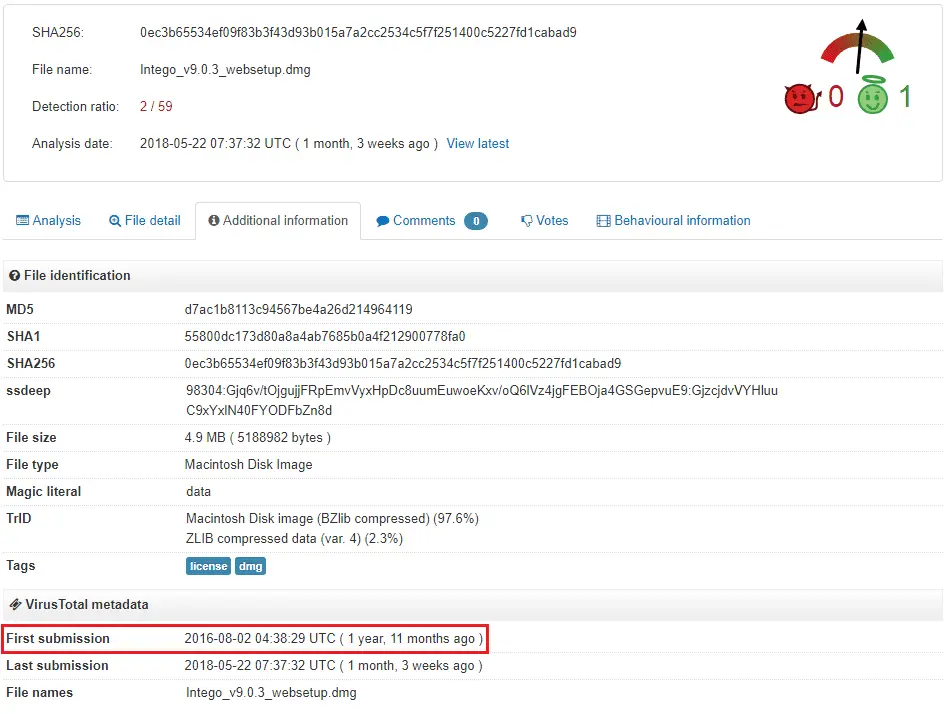
Kaspersky Lab’s security experts recently found a virus called Calisto malware, the guy who was the predecessor of the notorious Proton virus on macOS.  Kaspersky wrote in the analysis that the virus was uploaded to VirusTotal after it created in 2016. Now, Calisto is still bypassing almost of anti-virus solutions, only recently have someone valued this issue.

“We recently came across one such sample: a macOS backdoor that we named Calisto.The malware was uploaded to VirusTotal way back in 2016, most likely the same year it was created. But for two whole years, until May 2018, Calisto remained off the radar of antivirus solutions, with the first detections on VT appearing only recently.”

“Conceptually, the Calisto backdoor resembles a member of the Backdoor.OSX.Proton family.”

According to Kaspersky, Calisto’s installation file is an unsigned DMG image, but it is camouflaged with the Intego security solution (Mac version). At the same time, Kaspersky also noted that although the same roots as Proton, some features of Proton did not appear in Calisto.
Proton’s real face was only revealed in March last year, and the hacker created the virus in the underground hacking forum. The price of the whole project ranged from $1200-830.000.
A few weeks later, Proton was involved in the hacking for the first time, and the criminals blacked out the HandBrake app’s website and implanted the virus into the app. In October 2017, Proton RAT embedded into legitimate applications such as Elmedia Player and download manager Folx. Both Proton RAT and Calisto are remote access Trojan horses (RATs), and once infected, hackers gain control of the system.
If the Mac infected with Calisto, the hacker could quickly implement the following features remotely:
  • Enables remote login
  • Enables screen sharing
  • Configures remote login permissions for the user
  • Allows remote login to all
  • Enables a hidden “root” account in macOS and sets the password specified in the Trojan code
After static analysis by experts, several other unfinished functions have been discovered, such as:
  • Loading/unloading of kernel extensions for handling USB devices
  • Data theft from user directories
  • Self-destruction together with the OS
Security experts pointed out that Calisto developed before Apple introduced the SIP (System Integrity Protection) security mechanism, so it could not bypass SIP.
“Calisto’s activity on a computer with SIP (System Integrity Protection) enabled is rather limited. Announced by Apple back in 2015 alongside the release of OSX El Capitan, SIP is designed to protect critical system files from being modified — even by a user with root permissions. Calisto was developed in 2016 or earlier, and it seems that its creators simply didn’t take into account the then-new technology.”

Kaspersky issues the suggestion to protect against Calisto, Proton

  • Always update to the current version of the OS
  • Never disable SIP
  • Run only signed software downloaded from trusted sources, such as the App Store
  • Use antivirus software

Source, Image: securelist

Related coverage

  • Dream Job or Nightmare? Lazarus Group Hunts Crypto Devs with “Graphalgo” Malware
  • QakBot Returns with Evasive Tactics, Posing Renewed Threat
  • GoldenJackal Bypasses Air-Gaps in Sophisticated Espionage Campaigns
  • US Hospitals Targeted in Ransomware Attack, Ardent Health Services Confirms
  • Spirals Ransomware Encrypts a South Asian IT Network in Under 24 Hours
  • HOLLOWGRAPH Malware Hides Command-and-Control in Microsoft 365 Calendars
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Calisto malware

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 30, 2026
  • CVE-2023-22793CVSS 9.3
    A vulnerability allowing an unauthenticated attacker to perform remote code execution (RCE) on servers running the Veeam Virtualization...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61707CVSS 9.0
    SOCFortress CoPilot focuses on providing a single pane of glass for all your security operations needs. Prior to...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61645CVSS 9.1
    Docat is a tool for hosting versioned static documentation. In the affected implementation, an arbitrary file upload vulnerability...
    📅 Updated: Oct 29, 2026
  • CVE-2026-31158CVSS 9.8
    SQL Injection vulnerability in CRM SOFTTRADE Infotech (aka softtradeindia) 1.0 allows a remote attacker to execute arbitrary code...
    📅 Updated: Oct 29, 2026
  • CVE-2026-107032CVSS 9.1
    Insecure permissions in Bulk Share : Location Sender v2.1.0 (versionCode 5) allows unauthorized attackers to invoke an exported...
    📅 Updated: Oct 29, 2026
  • CVE-2024-8517CVSS 9.8
    SPIP before 4.3.2, 4.2.16, and 4.1.18 is vulnerable to a command injection issue. A remote and unauthenticated attacker...
    📅 Updated: Oct 29, 2026
  • CVE-2026-82854CVSS 9.3
    Nodemailer before 8.0.4 is vulnerable to SMTP command injection through the unsanitized envelope.size parameter. When an application passes...
    📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.